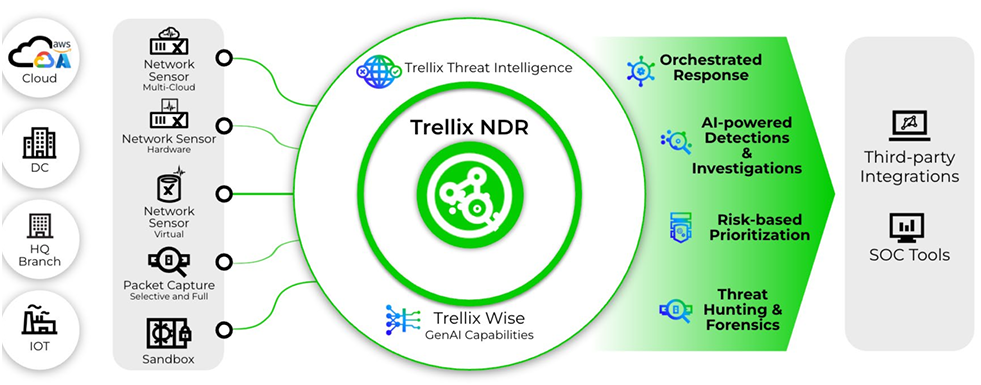
Trellix NDR correlates network sensor telemetry, threat intelligence, and Trellix Wise™ AI analysis to detect lateral movement and automate response across IT, cloud, and OT environments.
Trellix Network Detection and Response (NDR) delivers AI-powered visibility, real-time threat detection, and automated response across IT, OT, and ICS environments. Available in Essentials, Core, and Enterprise editions, Trellix NDR unifies five core capabilities:
NDR Console & Visibility — Risk-prioritized alert analysis, asset discovery, and IT/OT MITRE ATT&CK views.
NDR Sensor & Packet Capture (PX) — High-speed L7 metadata and selective PCAP in Defend, Boost, or Flare modes.
AI Investigation & Forensics — Trellix Wise™ (GenAI) triage plus packet, session, web, and email reconstruction.
Attack Path Discovery (APD) — Lateral movement path visualization and choke-point analysis using vulnerability data.
Integration Hub & Hyperautomation — Native SOAR workflows with Mandiant, GTI, ePO, Tenable, Splunk, and Nozomi.
Configure Trellix NDR
Perform initial appliance configuration
Integrate Trellix NDR
Supported integrations overview
Configure SIEM, Tenable, and ePO integrations
Hunt for threats and manage risk
Investigate threats and Attack Path Discovery