Trellix Drive Encryption protects the data on a system by taking control of the hard disk or self-encrypting drive (Opal) from the operating system. When you use it with self-encrypting drives, Drive Encryption manages the disk authentication keys with drives that are not self-encrypted.
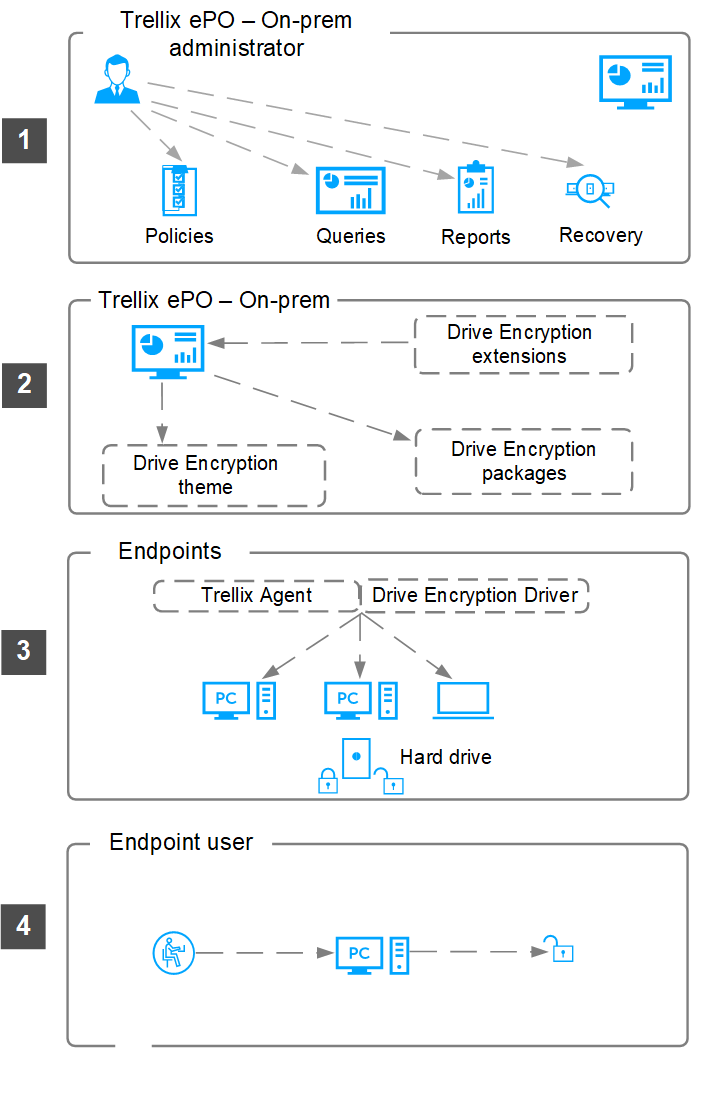
The ePO - On-prem administrator configures Drive Encryption policies, runs Drive Encryption queries and reports, and performs Drive Encryption system recovery if required.
The ePO - On-prem administrator installs the Drive Encryption extension on the ePO - On-prem server. The Drive Encryption software is checked in to ePO - On-prem and the Drive Encryption packages are deployed to the client system. When Drive Encryption is installed and activated, it takes control of the hard disk or self-encrypting drive (Opal), and policies are assigned to the client system.
Note
During the activation process, the system synchronizes with ePO - On-prem and acquires user data, token data, and pre-boot theme data. You can also use the Offline Activation feature to activate Drive Encryption on a client system without connecting to the ePO - On-prem server.
The Trellix DEAgent package is deployed to the required client systems. The Drive Encryption driver encrypts all data that is written to the disk and decrypts the data that is read on the disk.
After successful activation and system restart, the user is authenticated and logs on through the pre-boot environment, which then loads the operating system.
 |