In Adaptive mode, the precedence method is followed, but differently than in Regular mode.
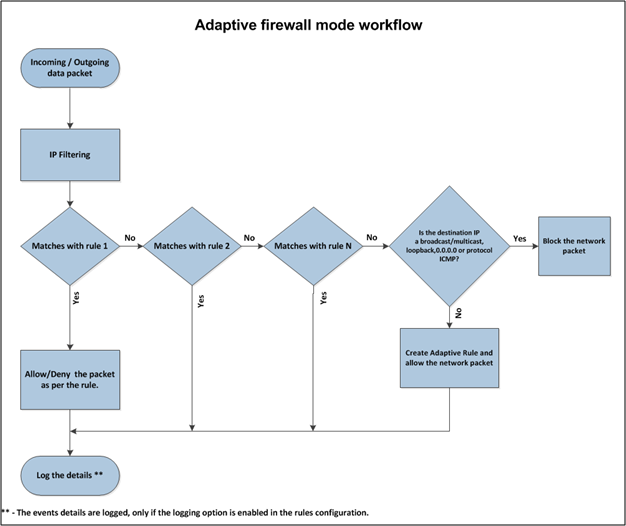
In Adaptive mode, firewall uses precedence to apply rules. The rule at the top of the rules list is applied first. When the network packet does not match the defined rules from the list, an allow rule is created to allow the non-matching packet.
Note
If the IP destination is a broadcast, multicast, loopback, or ICMP protocol, the network packet is blocked. No additional rules are created for these types of traffic.
For security reasons, when Adaptive mode is enabled, incoming pings are blocked unless an explicit allow rule is created for incoming ICMP traffic.
This diagram shows how network packets are handled in Adaptive mode.
Note
To change the firewall protection from Adaptive mode to Regular mode, click
| Preferences | Firewall | Regular Mode.