Evolving security challenges require open, collaborative approaches to detect threats, reduce risk, and ensure compliance. Trellix Enterprise Security Manager (Trellix ESM) integrates with other Trellix products to resolve threats quickly without overloading resources.
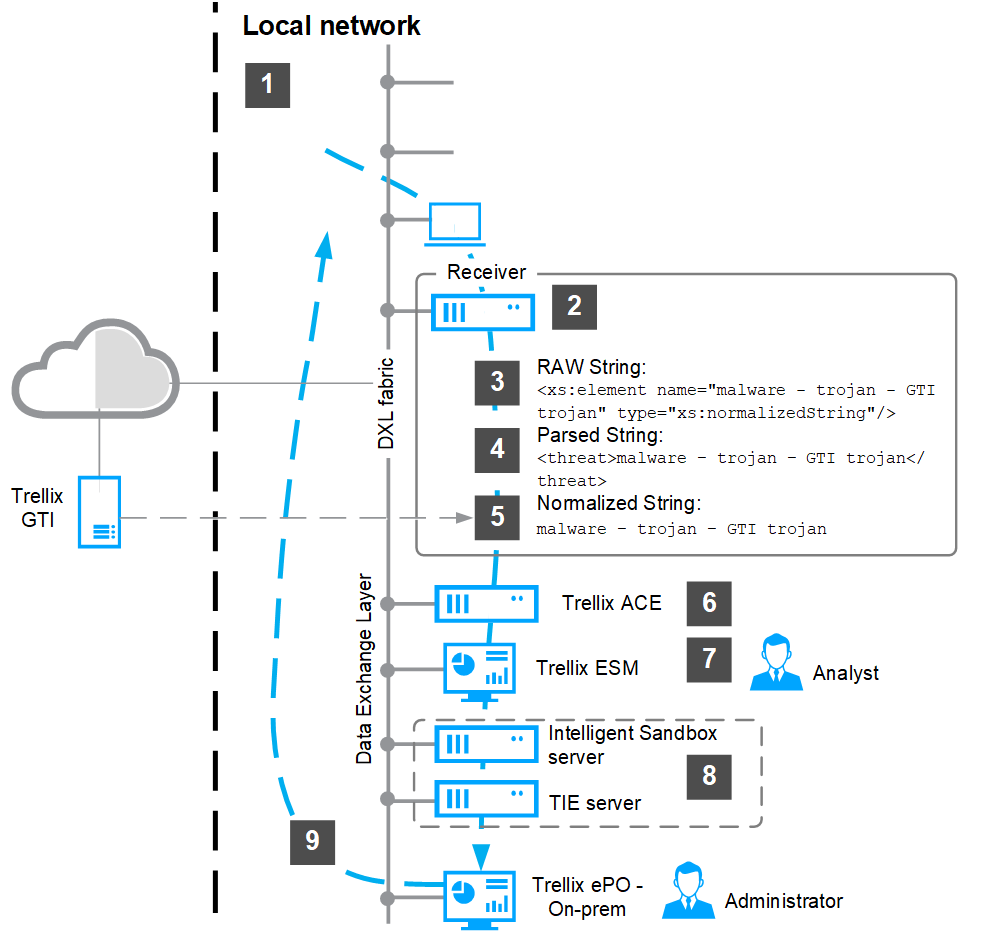
What is the Trellix ESM workflow?
Threat enters your organization.
The Trellix Enterprise Security Manager - Event Receiver (SIEM Collector) collects data and events from security devices, databases, networks, systems, and applications.
The SIEM Collector collects raw data.
The SIEM Collector parses (or extracts) data into parts and relationships based on your specific syntax rules.
The SIEM Collector normalizes (or aligns) collected values to one common scale and uses to identify known threats.
The Trellix Enterprise Security Manager - Advanced Correlation Engine (Trellix ESM - ACE) correlates (or identifies) patterns in the information to identify potential security threats.
Analyst monitors and identifies threats using dashboard, alarms, watchlists, incidents, and reports.
Analyst identifies threat using Data Exchange Layer (DXL), Trellix Intelligent Sandbox, and Trellix® Threat Intelligence Exchange (TIE).
Analyst uses Trellix ePolicy Orchestrator - On-premises to respond to threat immediately and automatically.
|