Consider this scenario to understand the advantages of VLAN Bridging:
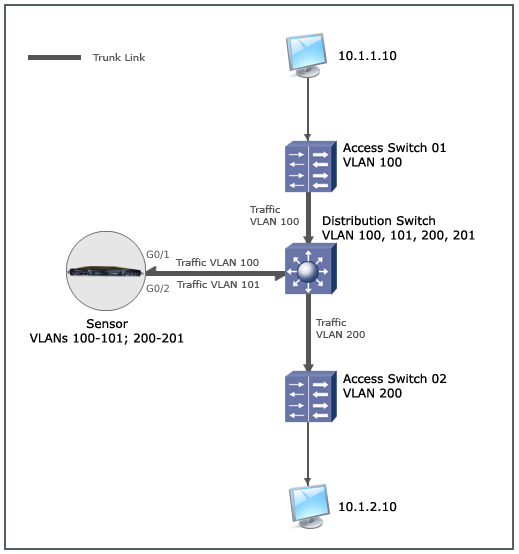
Host 10.1.1.10 in VLAN 100 tries to communicate with a host 10.1.2.10 in VLAN 200.
Access Switch 01 tags the packet with VLAN 100 and forwards it to the Distribution Switch. The Distribution Switch is an L3 switch, which has trunk links to the Sensor.
In the distribution switch, only the ports connected to G0/1 of the Sensor and Access Switch 01 are configured for VLAN 100. No other ports are configured for 100. This is a very critical configuration for enforcing IPS. When the Distribution Switch receives VLAN 100 traffic, the only network path available is to the Sensor.
In the distribution switch, only the ports connected to G0/2 are configured for VLAN 101.
The Sensor is configured to bridge VLANs. This is done by specifying the VLANs to be bridged as a pair at the interface level.
For this scenario, let us assume that you have configured VLANs 100 and 101 as a VLAN pair. Assuming the traffic is clean, the Sensor changes the VLAN tag to 101 and forwards it to the Distribution Switch through the corresponding peer port. Conversely, traffic tagged 101 is changed to tag 100 and sent through the corresponding peer port. Thus, the Sensor bridges VLANs 100 and 101.
The Distribution Switch receives the traffic tagged 101. Based on ARP, ARP replies, and the destination subnet, the switch forwards the traffic to the appropriate port so that it reaches host 10.1.2.10.
Note the following before you configure VLAN Bridging:
You can configure VLAN Bridging only on Sensors that are deployed inline fail-closed, unless you are attempting this on ports that have in-built fail-open.
Note that the distribution switch configuration has to keep the traffic separation of inbound/outbound on one Sensor's two links: the switch must restrict traffic from the outside net VLAN to only one link, and the inside net VLAN to only the other link. This switch configuration should be consistent with the Sensor's port designations of inbound/outbound.
If the traffic has a VLAN tag that is not configured on the Sensor, then post-IPS the traffic comes out from the Sensor to the switch with the same VLAN tag. Because both G0/1 and G0/2 are connected to the same switch, it will detect a loop and attempt to bring down the ports. For this reason, it is important that you disable Spanning Tree Protocol on the switch.
VLAN bridging will not work when Sensor enters L2 mode or when Sensor ports fail-open. This may result in traffic drop.