Once the Sensor validates the web server certificate, the Sensor uses the trusted certificates to encrypt the SSL session with the client.
Go to Devices → <Admin Domain Name> → Global → IPS Device Settings → SSL Decryption.
On the Outbound tab, select Re-Signing Certificate tab.
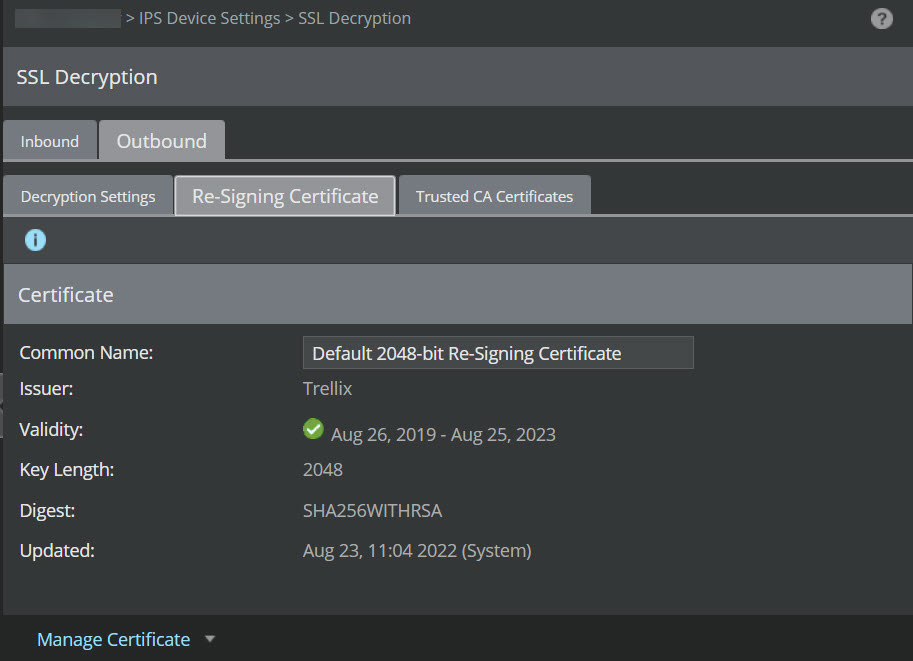
To import a trusted certificate:
Click Manage Certificate.
Click Import. The Import Re-Signing Certificate dialog box opens.
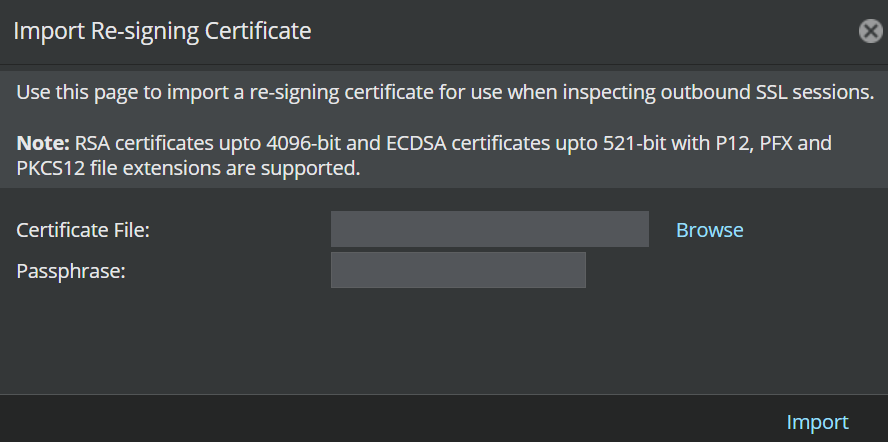
Click Browse.
Select the .p12 file stored in the local system.
Enter the Passphrase for the certificate file.
This is the phrase (export password) you used for encrypting your PKCS12 file.
Click Import.
Note
If you import a custom certificate, the default certificate is removed from the Sensor. If you want to use the default certificate, click the Use Default option to use the default certificate.
To export the public key of the certificate, click Export Public Key.
You need to export the public key of the Sensor and import it to the browsers in the client systems.
(Optional) Click Use Default.
(Optional) Click Regenerate Default to regenerate the default certificate.
You can use this option if the certificate you are using has expired.
To ensure that the Sensors are using the correct certificates, deploy the configuration changes to the Sensor.