You can quarantine endpoints from the list of alerts displayed in the Attack Log page.
Navigate to Analysis → <Admin Domain Name> → Attack Log.
Select the alert whose IP has to be quarantined.
Click Other Actions, and select Quarantine Endpoint. Click the endpoint IP address you want to quarantine.
Add to Quarantine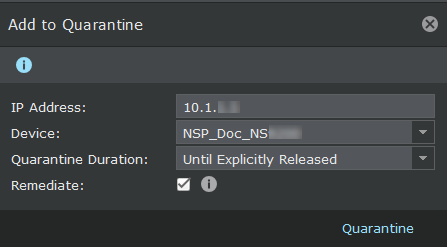
The Add to Quarantine pop-up opens.
Update the following fields:
Option
Definition
IP Address
Enter the IP address of the endpoint.
Device
Select the specific device of the endpoint whose traffic originating from the IP address you want to block.
Quarantine Duration
Select the quarantine duration from the drop-down list.
Remediate
Select the checkbox to redirect the configured endpoint to the configured remediation portal.
Note
You can configure the remediation portal settings in Devices → Global → IPS Device Settings → Quarantine → Remediation Portal.
Click Quarantine.