Use this file to discover all available pages before exploring further.
The new docs.trellix.com features a modernized UI and AI-powered conversational search. Content is currently available in English, with additional languages launching in early November 2026. We hope you enjoy the updated experience.
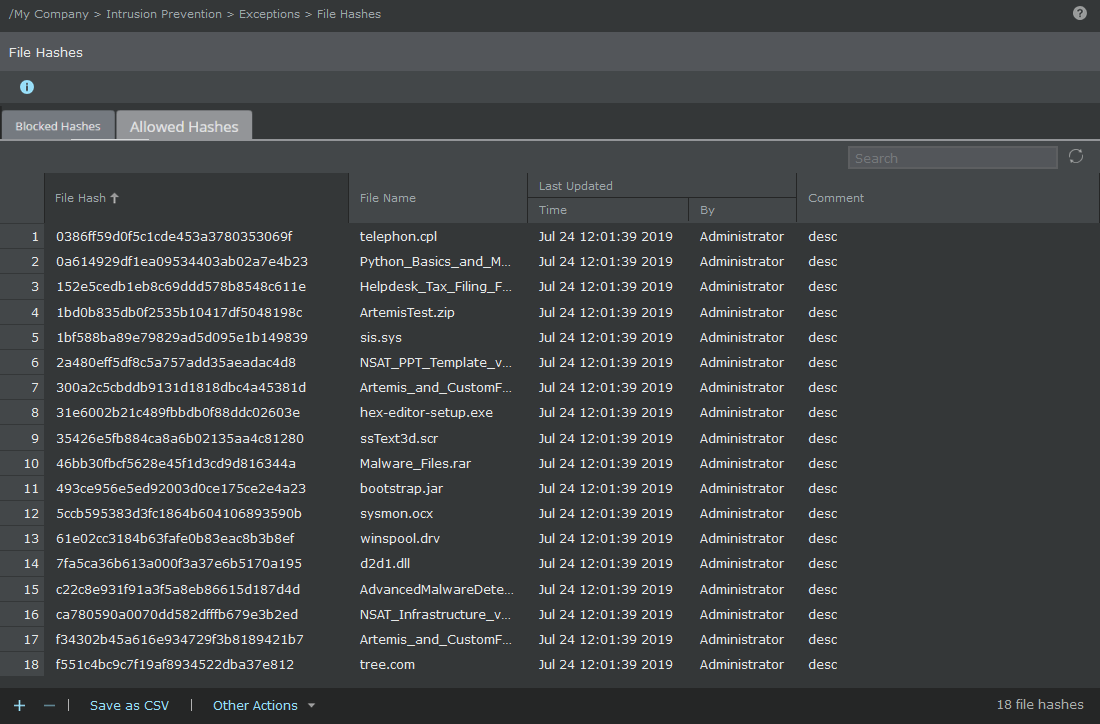
You can view the current list of allowed hashes on the
Allowed Hashes tab of the
File Hashes page.
Allowed Hashes The following table describes the details displayed on the
Allowed Hashes tab.
Format
Description
File Hash
Specifies the file hash. The
File Hash will be in the MD5 format.
File Name
Specifies the name of the file along with the file extension
Last Updated
Displays the following:
Time: Specifies the time stamp of the imported allow list
By: Specifies the user who imported the allow list
Comment
Any comments about the list
Click
Other Actions → Import to import a file containing the hash values.
Click
Browse to locate an XML or CSV file that contains the list of hashes you want to import.
Click
Import.
The file to be imported should be in the following CSV format.
<Name of the file with extension (like .exe, .com)>,<File size>,<Hash type>,<File hash>,<Description>
Note
The file hash should be in the MD5 format.
Example file format: Application.exe, 1024000, MD5, 30a4edd18db6dd6aaa20e3da93c5f425, textual description. Also note that if you are importing multiple files, each file has to be in a new line.
The following is a sample for a CSV file with multiple file hashes.
The following table describes the details of the files to be imported in the CSV or XML format.
Format
Description
<Name of the file with extension (like .exe, .com)>
Specifies the name of the file to be imported along with the file extension. This is an optional value.
<File size>
Specifies the size of the file to be imported. The file size should be a valid integer.
Note
File size value is mandatory. It is used by the Sensor as a secondary matching criterion when the same hash has been added to both the block list and allow list.
Note
If the file size is unknown, you can add a placeholder value like 1 to the CSV file as this value is mandatory.
<Hash type>
Specifies the format of the hash. The supported file hash type is the MD5 format.
<File hash>
Specifies the hash for the file to be imported
<Description>
Specifies the description of the file to be imported. This is an optional value.
Note
If you are importing using CSV, you can import the same file hash to both allow list and block list.
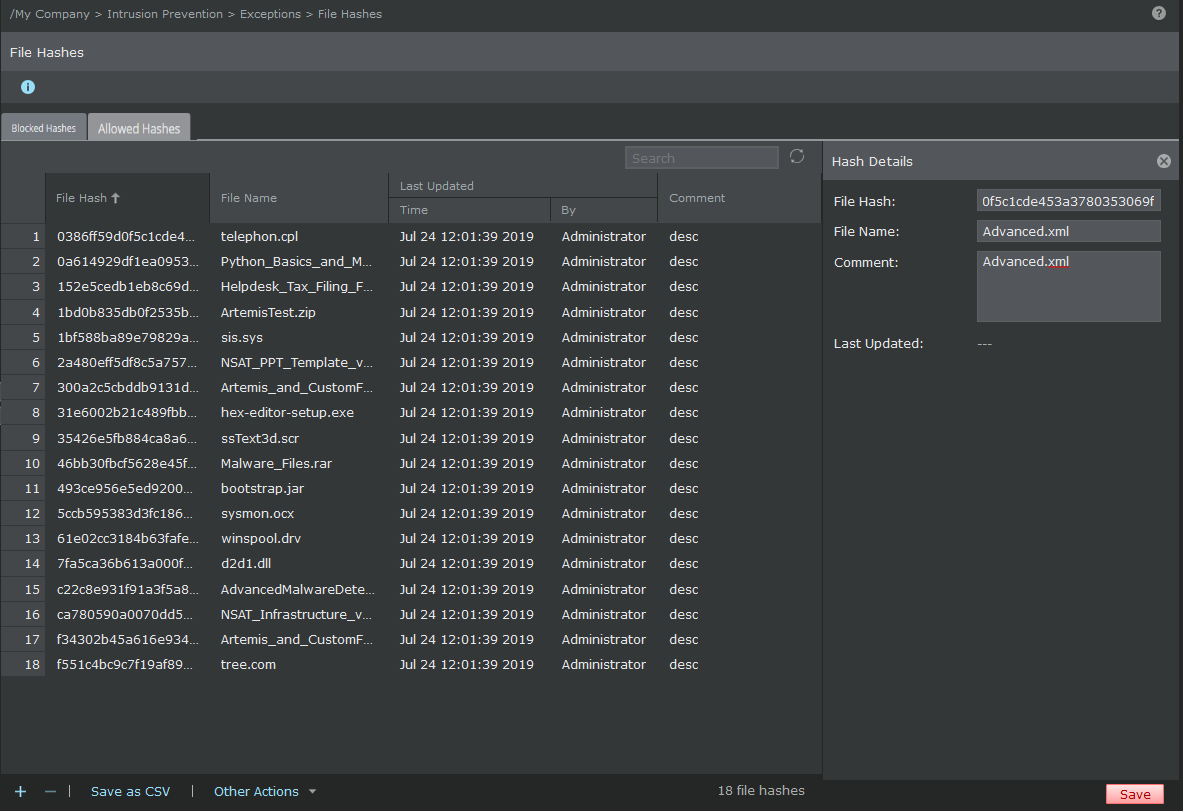
To add a single file hash to the allowed hashes, click
.
Click
Save after entering the values in
File Hash,
File Name, and
Comment. The
Comment field is optional.
Note
The
File Hash should be a 32 digit hexadecimal value.
Add a single allow list file hash value
To export the allowed hashes from the Manager to a local system, click
Other Actions → Export All.
To delete specific entries from the allow list, select them by holding the
Shift or
Ctrl key and clicking on the required rows. Then click
.
The deleted hashes are now neither in the allow list nor in the block list.
To remove all the entries, select
Other Actions → Delete All.
To move specific entries to the block list, select the entries and then select
Other Actions → Move to Block List.
A manual signature set push is not required each time the allow list or the block list is updated. The Manager updates the Sensor dynamically with the modified entries in the allow list or block list, at an interval of 5 minutes. These updates occur in bulk (the complete list of entries) or increments (added/deleted entries). To view the status of these updates, use the
show ab stats command. For more information, see the
CLI commands section in the
Trellix Intrusion Prevention System Product Guide.
You can configure a maximum of 99,000 entries (allowed and blocked).

 .
Click Save after entering the values in File Hash, File Name, and Comment. The Comment field is optional.
 .
The deleted hashes are now neither in the allow list nor in the block list.