You can add a list of allowed fingerprints (MD5 or SHA256 hash values) for files you want to be exempted from malware analysis when found in HTTP or SMTP downloads.
Select Policy → <Admin Domain Name> → Intrusion Prevention → Exceptions → File Hashes.
You can view the current list of allowed hashes on the Allowed Hashes tab of the File Hashes page.
Allowed Hashes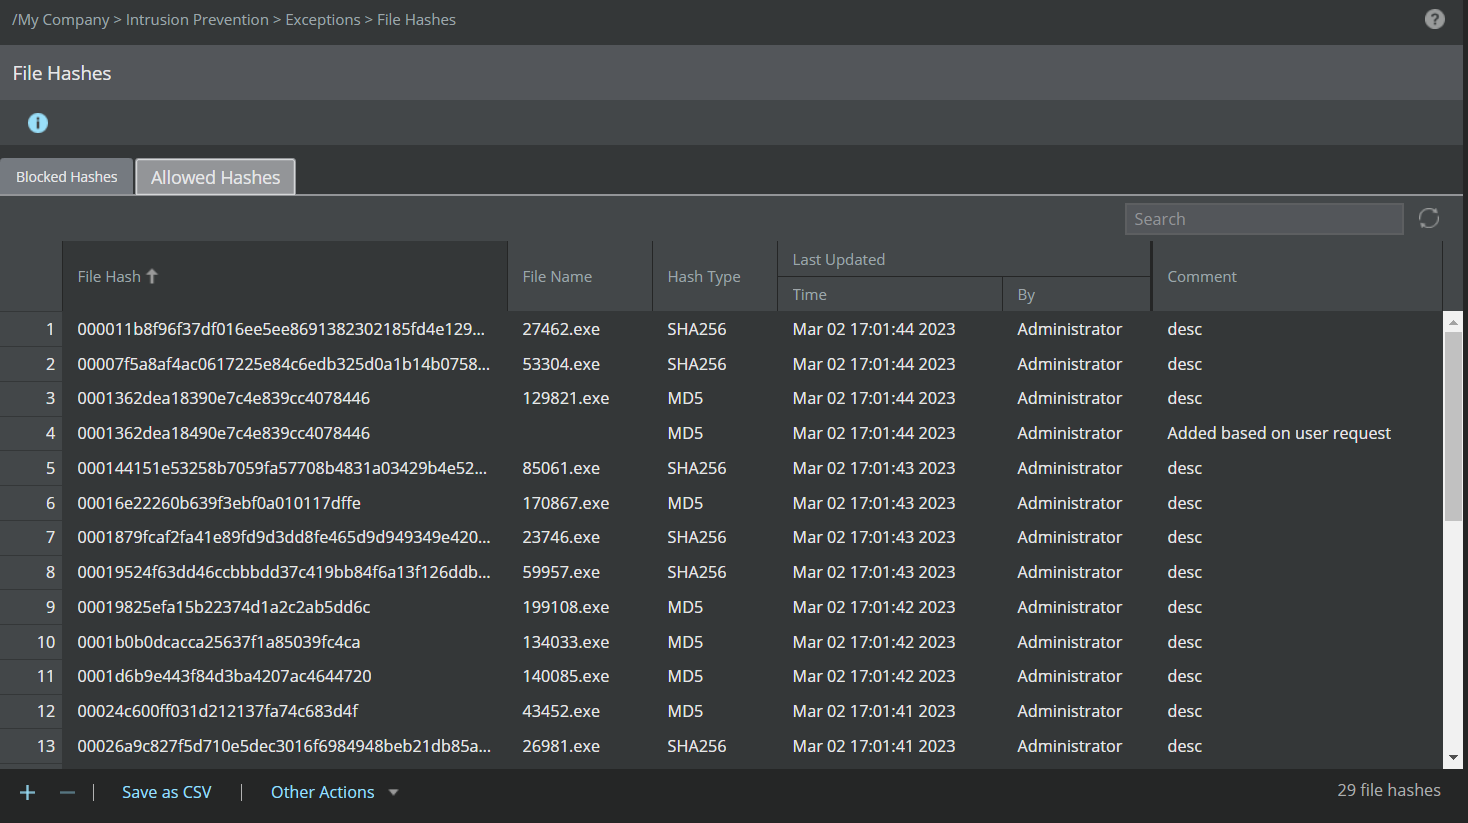
The following table describes the details displayed on the Allowed Hashes tab.
Format
Description
File Hash
Specifies the file hash. The File Hash should be in MD5 or SHA256 format
File Name
Specifies the name of the file along with the file extension
Hash Type
Specifies the format of the hash. The supported file hash types are MD5 and SHA256.
Last Updated
Displays the following:
Time: Specifies the time stamp of the imported allow list
By: Specifies the user who imported the allow list
Comment
Any comments about the list
File hashes can be added through this page in two ways — using the Import option or the
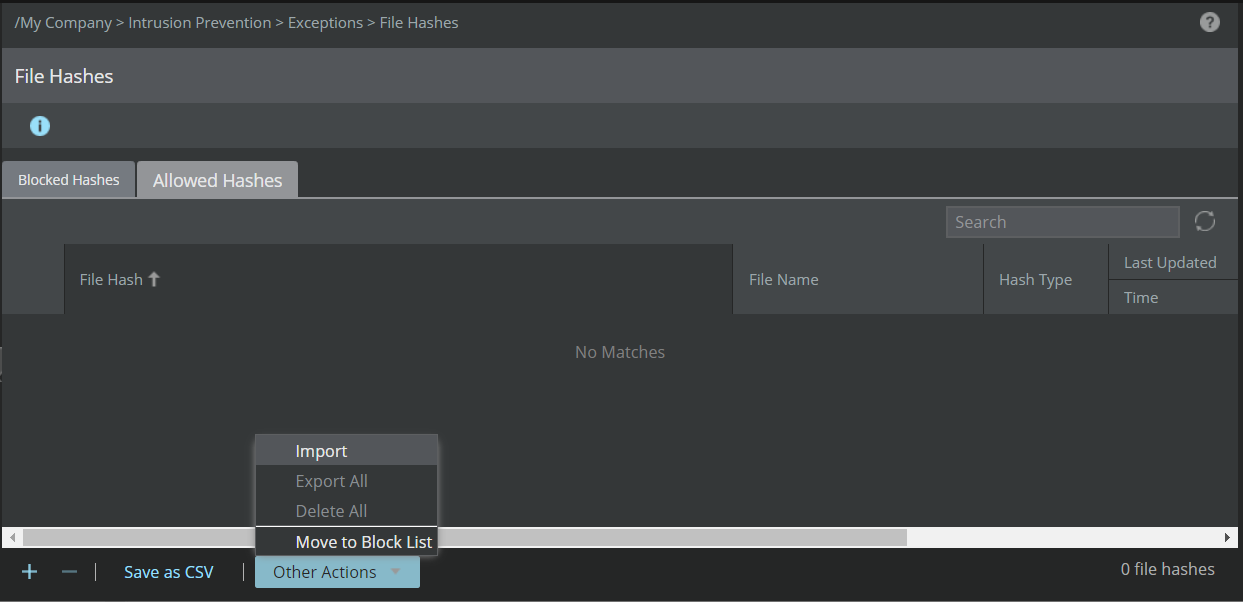
 icon. To import a file containing the hash values, click Other Actions → Import.
Import from CSV window appears. Use the Append option to add a new list of hashes or to append a list of hashes to an existing list. Use the Replace option to remove the existing list of hashes and add a new list from the file being imported.
The file to be imported should be in the following CSV format.
<Name of the file with extension (like .exe, .com)>,<File size>,<Hash type>,<File hash>,<Description>Example file format for MD5 hashes:
Application.exe, 1024000, MD5, 30a4edd18db6dd6aaa20e3da93c5f425, textual description.Example file format for SHA256 hashes:
Service.exe, 1024000, SHA256, a6279afa088a2e200b3b222c3169e9dce332a08759512800b48bf038e47bf528, textual description. Also note that if you are adding multiple entries in the CSV file, each entry has to be in a new line.The following is a sample for a CSV file with multiple file hashes.

The following table describes the details of the files to be imported in the CSV or XML format.
Format
Description
<Name of the file with extension (like .exe, .com)>Specifies the name of the file to be imported, along with the file extension. This is an optional value.
<File size>Specifies the size of the file to be imported. The file size should be a valid integer.
Note
File size value is mandatory. It is used by the Sensor as a secondary matching criterion when the same hash has been added to both the block list and allow list.
Note
If the file size is unknown, you can add a placeholder value like 1 to the CSV file as this value is mandatory.
<Hash type>Specifies the format of the hash. The supported file hash types are MD5 and SHA256.
<File hash>Specifies the hash for the file to be imported
<Description>Specifies the description of the file to be imported. This is an optional value.
Note
If you import the same file hashes to allow list first and then to block list, the hashes in the allow list will be removed and added to the block list. Similarly, if you import the same file hashes to block list first and then to allow list, the hashes in the block list will be removed and added to the allow list.
Click Browse to locate the CSV file that contains the list of hashes you want to import.
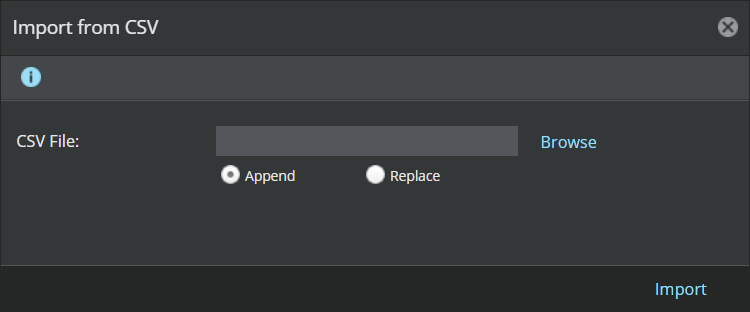
Click Import upon selecting the CSV file.
To add a single file hash to the allowed hashes, click
.Click Save after entering the values in File Hash, File Name, and Comment. The Comment field is optional.
Note
The File Hash should be a 32 or 64 digit hexadecimal value depending on the hash type.
Add a single allow list file hash value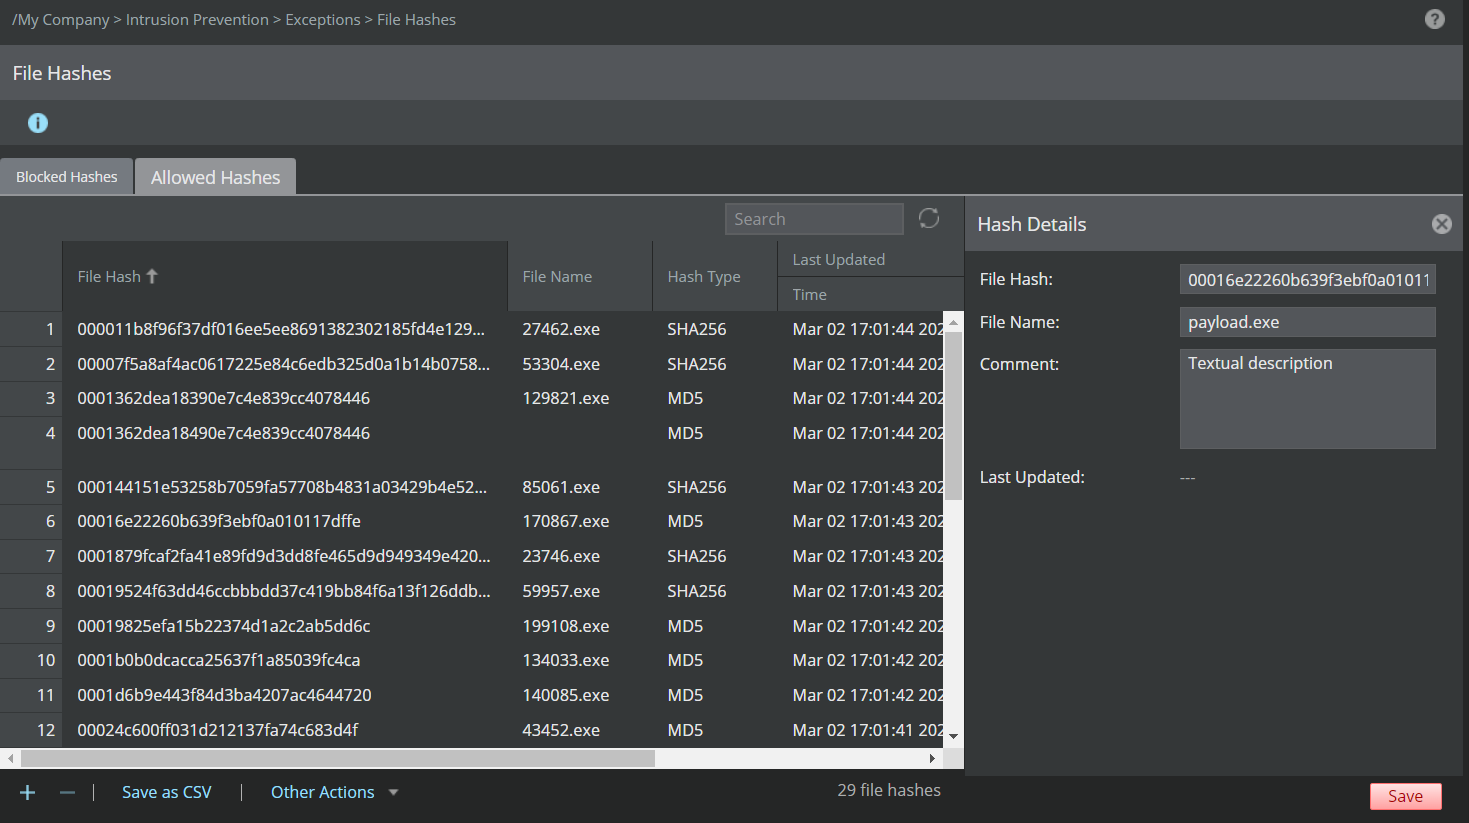
Note
The Manager running on 11.1 Update 1 or later releases supports addition of up to 400,000 hash entries (allowed and blocked combined) with a limit of 200,000 per each hash type. Manager prior to 11.1 Update 1 release supports addition of only MD5 hashes up to 100,000 entries (allowed and blocked combined).
Sensors prior to 11.1 Update 1 release do not support SHA256 hashes. The maximum number of hashes supported (cumulative of Blocked Hashes and Allowed hashes) by these Sensors is 100,000.
Sensors running on 11.1 Update 1 or later releases support both SHA256 and MD5 hashes. NS-series Sensors support a maximum of 200,000 hashes for each hash type while the Virtual IPS Sensors support a maximum of 100,000 hashes for each hash type. If the Manager has both NS-series and virtual Sensors, entries over 100,000 in each hash type are pushed only to the NS-series Sensors. The push fails on virtual Sensors and a fault is raised which can be noticed in the Faults (Manager → Troubleshooting → Logs → Faults) tab.
In case of heterogeneous environments, if the total MD5 hash entries exceed 100,000:
A limit exceed error can be seen in filetransfer.log during a bulk (full) update
A fault will be raised in the Faults tab and error count will be incremented at the Sensor level during an incremental update. Refer to
show ab statscommand for more information.Note
A Full update is triggered when the total entries are more than 4000; else, an incremental update is triggered to all the Sensors connected to the Manager.
In case MD5 and SHA256 hashes of the same file are added, the MD5 hash takes precedence over SHA256 hash of the file during analysis.
To export the allowed hashes from the Manager to a local system, click Other Actions → Export All.
To delete specific entries from the allow list, select them by holding the Shift or Ctrl key and clicking on the required rows. Then click
 .
The deleted hashes are now neither in the allow list nor in the block list.
To remove all the entries, select Other Actions → Delete All.
To move specific entries to the block list, select the entries and then select Other Actions → Move to Block List.
A manual signature set push is not required each time the allow list or the block list is updated. The Manager updates the Sensor dynamically with the modified entries in the allow list or block list, at an interval of 5 minutes. These updates occur in bulk (the complete list of entries) or increments (added/deleted entries). To view the status of these updates, use the
show ab statscommand. For more information, see the CLI commands section in the Trellix Intrusion Prevention System Product Guide.