You can select a particular alert and configure an ignore rule. If necessary, you can create a new ignore rule and apply it to the selected alert. You apply an ignore rule to the resource for which the attack is raised and the direction of the attack.
To create Ignore Rules for the alerts generated, complete the following steps:
Select Analysis → <Admin Domain Name> → Attack Log.
Select the alert for which you want to create the Ignore Rule, and click Other Actions.
Select Create Exception and click the Add Ignore Rule option.
The Add Ignore Rule panel appears.
Add ignore rule panel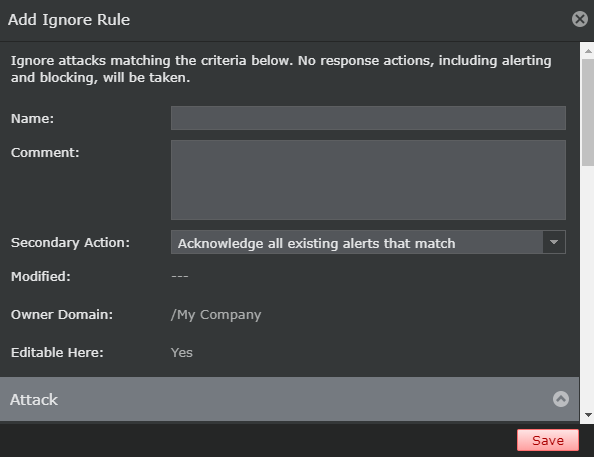
Specify your options in the corresponding fields.
Field
Description
Name
Type the name for the Ignore Rule.
Comment
Type additional comments if required.
Secondary Action
The secondary/additional action to be performed on the alert other than ignoring the alert.
None — No action taken other than ignoring the alert.
Acknowledge all existing alerts that match — Acknowledges all the alerts that match the criteria. You can later view these alerts as acknowledged alerts in the Attack Log.
Delete all exisitng alerts that match — Deletes all the alerts that match the ignore rule criteria. These alerts will not be available in the database also.
Modified
Displays the last modified user, date and time for the Ignore Rule. The field is blank when creating the rule for the first time.
Owner Domain
The name of the admin domain under which the Ignore Rules are added
Editable here
The status Yes indicates that the Ignore Rule is owned by the current admin domain. The status No indicates that the Ignore Rule is not owned by the current admin domain.
Attack
Select the attack to match the criteria.
Type the first few letters of the attack name in the Search attack name field, select the attack from the list.
Click the Add button to add the attack name to the list.
Select the Direction from the drop-down list. The options are Inbound, Outbound, and Any.
Click
 to remove the attack from the list.
Scope
Select one or more device or interface to match the criteria.
Select the device or interface from the Resource drop-down-list.
Click the Add button to add the device or interface to the list.
Click
to remove the item from the list.Attacker
Select the rule object from the Endpoint drop-down-list.
Click on the Add button to add the rule object to the list.
Click the Add icon to add a new rule object. The supported network objects are:
IPv4 Address Range
IPv4 Endpoint
IPv4 Network
IPv6 Address Range
IPv6 Endpoint
IPv6 Network
Network Group for Exception Object
Click
 to edit or view a rule object.
Click
to remove the rule object from the list.Select the type of port from the Port drop-down list. The available options are:
Any
TCP
UDP
TCP or UDP
Type the port values for TCP and UDP protocols in the field provided. The supported port values are 1 to 65535. To specify multiple ports used in the same protocol, provide the values separated by commas. Example: 15,25.
Target
Select one or more rule objects.
Select the rule object from the Endpoint drop-down-list.
Click on the Add button to add the rule object to the list.
Click
to add a new rule object. The supported network objects are:IPv4 Address Range
IPv4 Endpoint
IPv4 Network
IPv6 Address Range
IPv6 Endpoint
IPv6 Network
Network Group for Exception Object
Click
to edit or view a rule object.Click
to remove the rule object from the list.Select the type of port from the Port drop-down list. The available options are:
Any
TCP
UDP
TCP or UDP
Type the port values for TCP and UDP protocols in the field provided. The supported port values are 1 to 65535. To specify multiple ports used in the same protocol, provide the values separated by commas. Example: 15,25.
Click Save to save the Ignore Rule.
For more information on Ignore Rules, refer to Manage Ignore Rules in IPS Administration section.