To add Ignore Rules in the Manager, complete these tasks.
Select Policy → <Admin Domain Name> → Intrusion Prevention → Exceptions → Ignore Rules.
In the Ignore Rules page, click
 .
The Rule Details panel appears.
Add an Ignore Rule window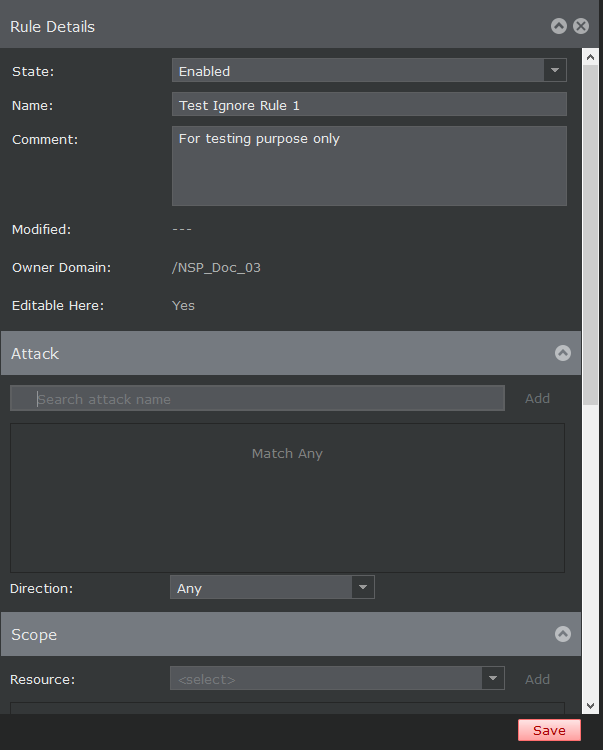
Specify your options in the corresponding fields.
Field
Description
State
Select the status of Ignore Rules as Enabled or Disabled from the drop-down list
Name
Type the name of the Ignore Rule
Comment
Type additional comments if required.
Modified
Name of the user who last modified the rule.
Owner Domain
The name of the admin domain under which the Ignore Rules is added.
Editable here
The status Yes indicates that the ignore rule is owned by the current admin domain. The status No indicates that the Ignore Rule is not owned by the current admin domain.
Attack
Select the attack to match the criteria.
Type the first few letters of the attack name in the Search attack name field select the attack from the list.
Click the Add button to add the attack name to the list.
Select the Direction from the drop-down list. The options are Inbound, Outbound and Any.
Click
 to remove the attack from the list.
Scope
Select one or more device or interface to match the criteria.
Select the device or interface from the drop-down list.
Click on the Add button to add the device or interface to the list.
Click
to remove the item from the list.Attacker
Select the rule object from the drop-down list.
Note
The Manager filters the rule objects containing more than 10 entries and lists only those which contain up to 10 entries, since the maximum supported rule object members per rule object in Ignore Rules is 10.
Click on the Add button to add a rule object to the list.
Click
to create a new rule object. The supported network objects are:IPv4 Address Range
IPv4 Endpoint
IPv4 Network
IPv6 Address Range
IPv6 Endpoint
IPv6 Network
Network Group (Network Group for Exception Object)
Click
 to edit or view a rule object.
Click
to remove the rule object from the list.Select the type of port from the Port drop-down list. The available options are:
Any
TCP
UDP
TCP or UDP
Type the port values in the field provided. The supported port values are 1 to 65535. To specify multiple ports used in the same protocol, provide the values separated by commas. Example: 15,25.
Target
Select one or more rule objects.
Select the rule object from the drop-down list.
Note
The Manager filters the rule objects containing more than 10 entries and lists only those which contain up to 10 entries, since the maximum supported rule object members per rule object in Ignore Rules is 10.
Click on the Add button to add the rule object to the list.
Click
to create a new rule object. The supported network objects are:IPv4 Address Range
IPv4 Endpoint
IPv4 Network
IPv6 Address Range
IPv6 Endpoint
IPv6 Network
Network Group for Ignore Rule
Click
to edit or view a rule object.Click
to remove the rule object from the list.Select the type of port from the Port drop-down list. The available options are:
Any
TCP
UDP
TCP or UDP
Type the port values in the field provided. The supported port values are 1 to 65535. To specify multiple ports used in the same protocol, provide the values separated by commas. Example: 15,25.
Click Save to save the Ignore Rule.