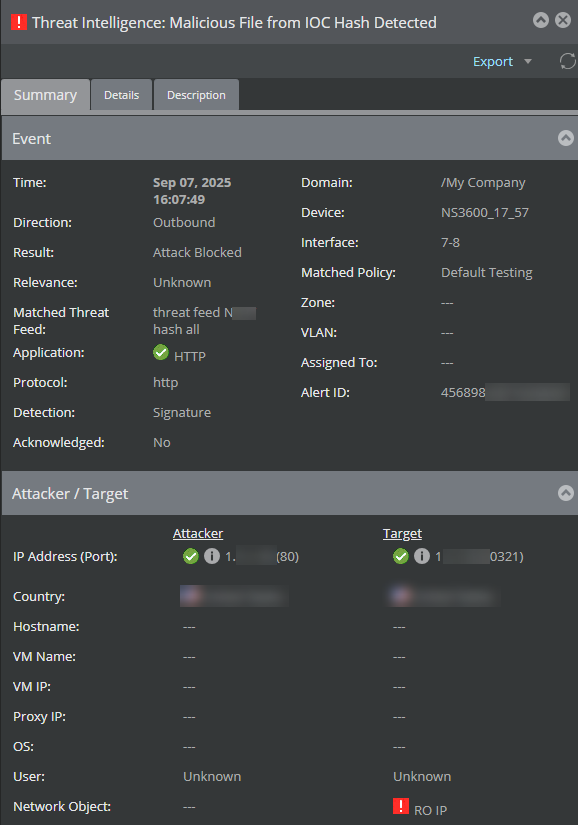
You can view the details of a specific attack for a clearer picture of the key information related to the attack. The information can then be used to augment your policy settings and/or to initiate a response action, such as a TCP reset or endpoint quarantine rule.
To view the details of a specific attack, do the following:
Steps:
Navigate to Analysis → <Admin Domain Name> → Attack Log.
Double-click on the alert for which you want to view the details.
The <Attack Name> panel opens on the right hand side.
The details of the alert are displayed as follows:
Option
Definition
Summary
Event — Displays the general alert details like the time, direction, device, matched threat feed etc.
Attacker/Target — Displays the IP address, hostname and other details of the attacker and the target. In case of mobile related alerts, the relevant fields related to mobile traffic are displayed.
Details
Matched Signature — Displays information about the configured signature conditions that matches with the attack.
Malware File — Displays the malware attack information such as the file name, file hash (MD5, SHA1, and SHA256), malware name, malware confidence, engine, size, description, and CVE ID.
Note
Malware File option is displayed only for malware attacks.
Layer 7 — Displays the layer 7 information for protocols like HTTP, SMTP, DNS, SMB, DCERPC etc.
Description
Displays further details about the alert like the BTP score, RfSB, protection category, etc.
Reference — Displays the different IDs created for the alert and attack, such as Trellix IPS ID, CVE ID etc. It also contains a collapsible subsection named Mitre Attack Details which displays the matching Tactic, Technique, Sub-Technique, and Technique/Sub-Technique ID for the attack or alert.
The Technique/Sub-technique ID is hyperlinked that connects to the specific technique/sub-technique web page on the MITRE ATT&CK website.
Note
Mitre Attack Details subsection is available in both Trellix IPS Manager and Central Manager.
Note
If an attack matches with multiple tactics, techniques, and/or sub-techniques, their names along with applicable technique/sub-technique IDs are displayed in the Mitre Attack Details subsection.
When an attack is mapped to multiple tactics, techniques, and/or sub-techniques, there is one-to-one correspondence among the tactics, techniques, sub-techniques, and technique/sub-technique IDs. For example, the first tactic corresponds to the first technique, sub-technique, technique/sub-technique ID, and so on.
Note
If the Tactic, Technique, Sub-Technique, or Technique/Sub-Technique ID is not available for any alert or attack, that particular field is displayed as --- within the subsection.
Note
Mitre attack related details are not shown for older alerts.
Component Attacks — Displays the component attacks in case of reconnaissance attacks only.
Signatures — Displays the signature associated with the attack.
Comments — You can add any comments for the alert if any.
Alert Details panel