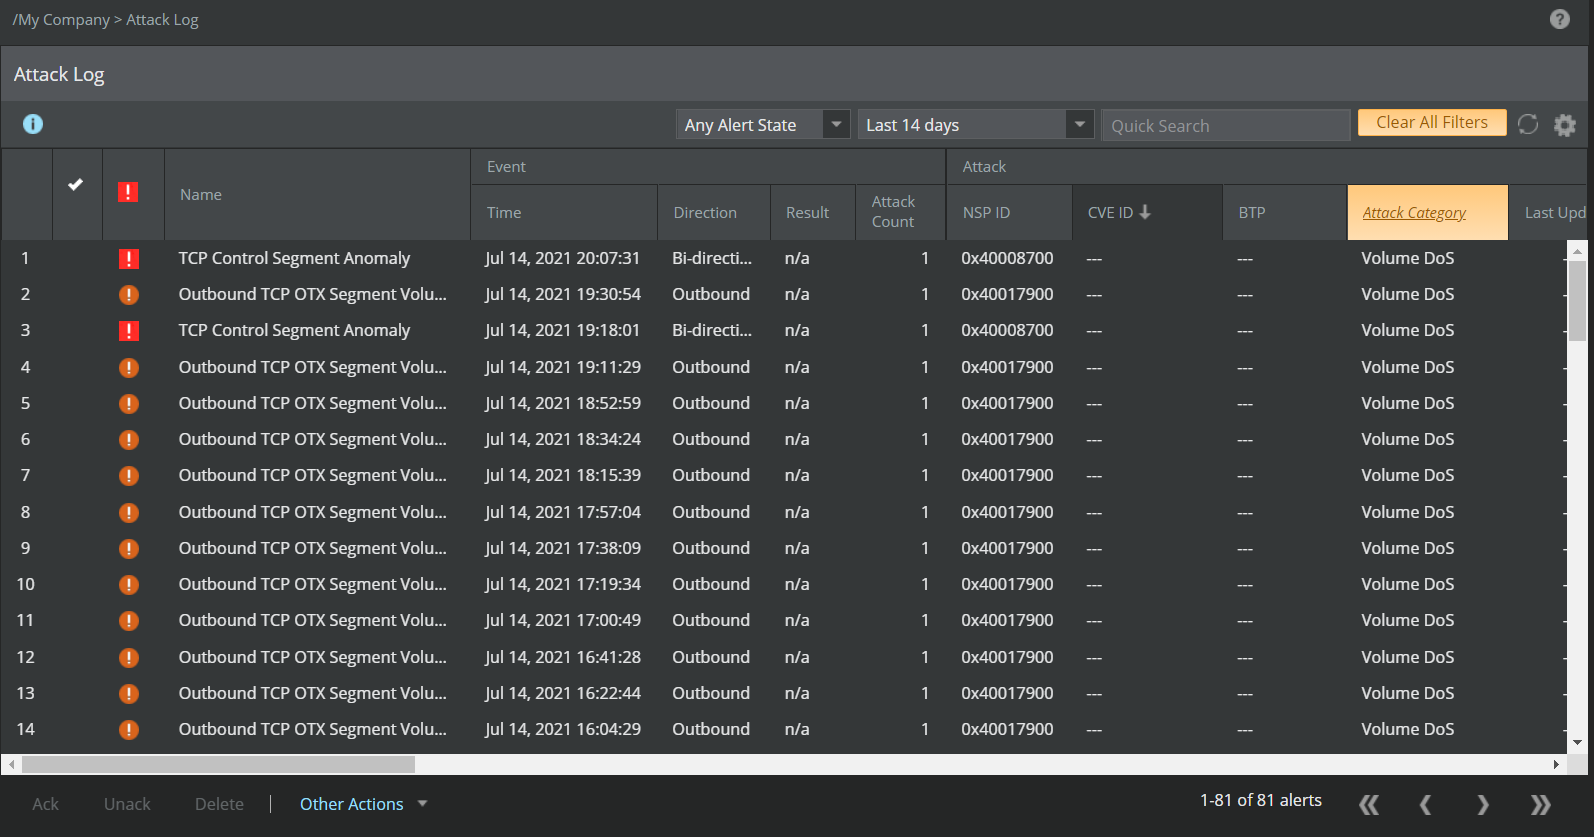
DoS related alerts are listed in the Attack Log page under the Analysis tab. DoS related alerts are either alerts relating to threshold violations or statistical attacks.
Simple threshold alerts are those in violation of DoS threshold mode settings.
Statistical attacks are those in violation of DoS learning mode settings.
To view details of a specific alert, double-click an alert. The alert details panel opens on the right side.
The alert details panel gives a clearer picture of the key information related to the attack. The information can then be used to augment your policy settings and/or to initiate a response action.
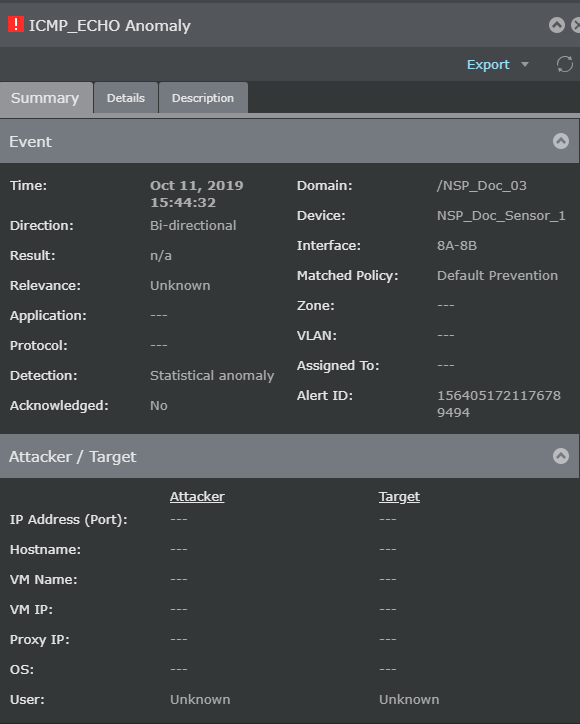
The alert details panel displays alert details that are specific to a type of attack. Hence, the information displayed varies from one type of attack to another.
Some alert details relating to DoS attacks are:
Simple Threshold Alerts
Simple Threshold alerts are those in violation of DoS threshold mode settings.
Threshold ID — This ID corresponds to where this threshold attack is listed in the DoS Threshold Mode catalog.
Observed Value — The number of times the instance occurred. Since an alert was sent, this value is larger than the threshold value.
Threshold Duration — The time limit value set within DoS threshold mode customization for the attack instance. This complements the Threshold Value. This duration is run to the end to capture all instances within the time limit rather than stopping after the first value over the threshold is detected.
Threshold Value — The limit set within DoS threshold mode customization for the attack instance and complements the Threshold Duration.
Statistical Alerts
Statistical attacks are those in violation of DoS learning mode settings.
Packet Rate Distribution — Displays bar graphs with packet rate data related to the violated learning mode measure. The violated measures are displayed with the corresponding packet rate over the last 1 minute. The graph displays the learned long-term rate (as established by the DoS profiling process) against recent activity, or short-term rate. The short-term rate is for the most recent 1 minute approximately. When the short-term rate is greater than the long-term rate and exceeds the specified response sensitivity (low, medium, or high - from DoS Learning Mode settings), an alert is generated.
The percentage value represents the percentage of all traffic for which the noted measure accounted. For example, if the normal percentage for IP fragments is approximately 2.5 percent, then IP fragments make up 2.5 percent of all traffic through the monitored segment. If the percentage of fragmented IP packets in the traffic during an interval was significantly higher than the established long-term percentage, it indicates an IP fragment flood attack.
DoS packet rate distribution graph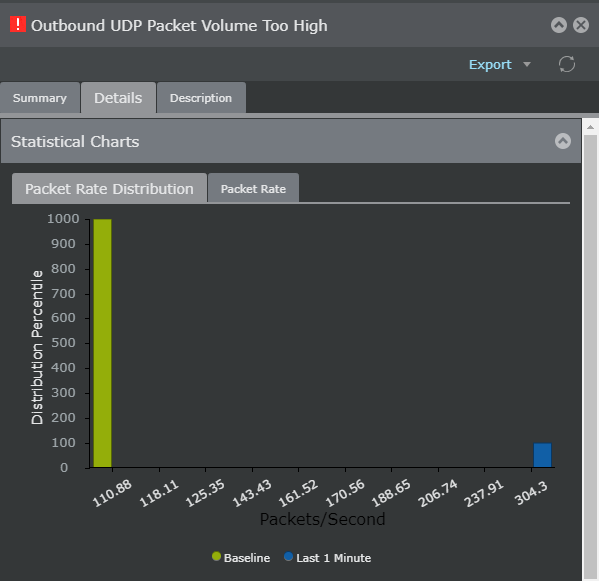
Packet Rate — Displays the violated measure's packet rate for the last minute when the alert was raised. Packet rates are shown in five-second intervals.
DoS packet rate graph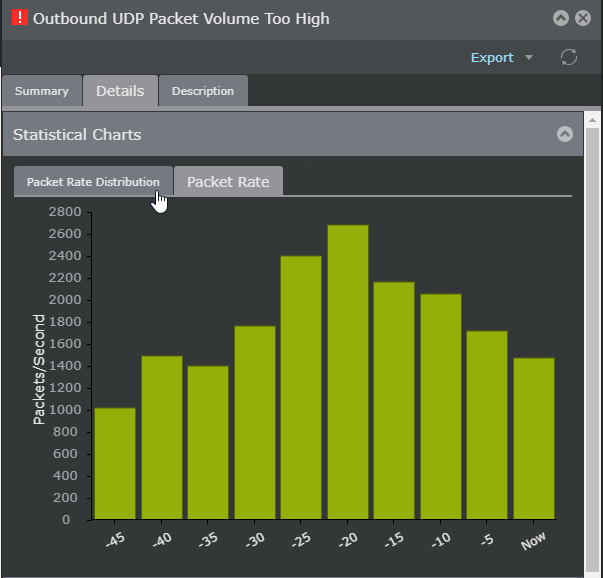
Traffic Volume — Displays the ranges of IP addresses, both source and destination that were involved in the DoS attack.
The packet type and total number of packets that were a part of the attack are also noted.
Total Packets Observed is the number of DoS packets seen from the given source and destination range. This includes both benign and attacking packets. All packets of various packet types, such as TCP SYN, destined to the particular network are displayed in the alert.
DoS IP range dialog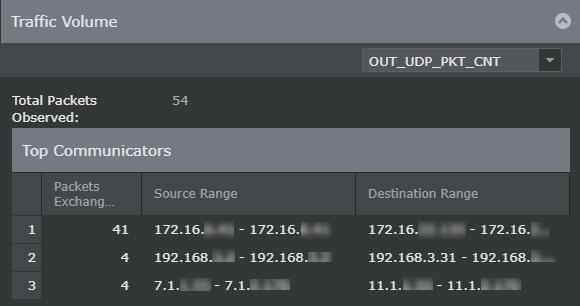
The first DoS alert shows packets counts received for 5 seconds before the alert. The subsequent suppressed alerts show the number of packets received since the last alert.
If you choose to drop packets, the Sensor drops only the bad packets. Thus, the Sensor might not always drop packets from what is determined as a good source IP address.