You can view the list of executables that have made outgoing connections using the Analysis → Endpoint Executables page, along with the classification and malware confidence computed for each executable. You can also view details, such as how many endpoints are running each executable, how many connections were made, etc. The Manager allows you to further drill down on each executable to view detailed information.
In an enterprise network, you can have hundred of thousands of executables making outgoing connections. To handle such a volume and yet quickly narrow down to a subset of endpoints or executables that exhibit malware like characteristics and require immediate attention, Trellix IPS supports the following options:
- You can enable auto-classification for executables based on file reputation provided by Trellix GTI. You can also enable auto-classification for executables signed by a trusted certificate authority.
- You can import a baseline computer profile for your organization under Policy → <Admin Domain Name> → Intrusion Prevention → Exceptions → File Hashes. This will help reduce the list of unclassified executables.
- You can also manually classify executables by monitoring their network behavior or based on the malware confidence computed by various engines. The manual classification will override the auto-classification as well as the classification imported using a baseline computer profile.
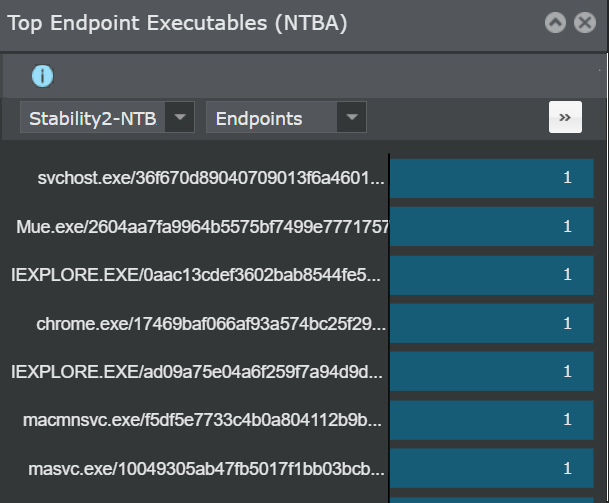
The Top Endpoint Executables is available in the Manager Dashboard page. You can filter the executables based on NTBA Appliance, attacks (default) or endpoints, or malware confidence. You can click on the graph to navigate to the Threat Explorer or the Endpoint Executables page for further investigation.