You can use any tactic, technique, and/or sub-technique displayed over the MITRE ATTACK View page to delve deeper into the attack data for further analysis. With the Show only matching attacks toggle button set to ON (default), the page displays all tactics as column headings within the grid view for which attack entries exist in the Attack Log. You can apply further filters (IP address and/or attack severity level) using the  button to get a more filtered and customized view of the adversarial tactics shown in the page.
Analyzing attack details using matching technique
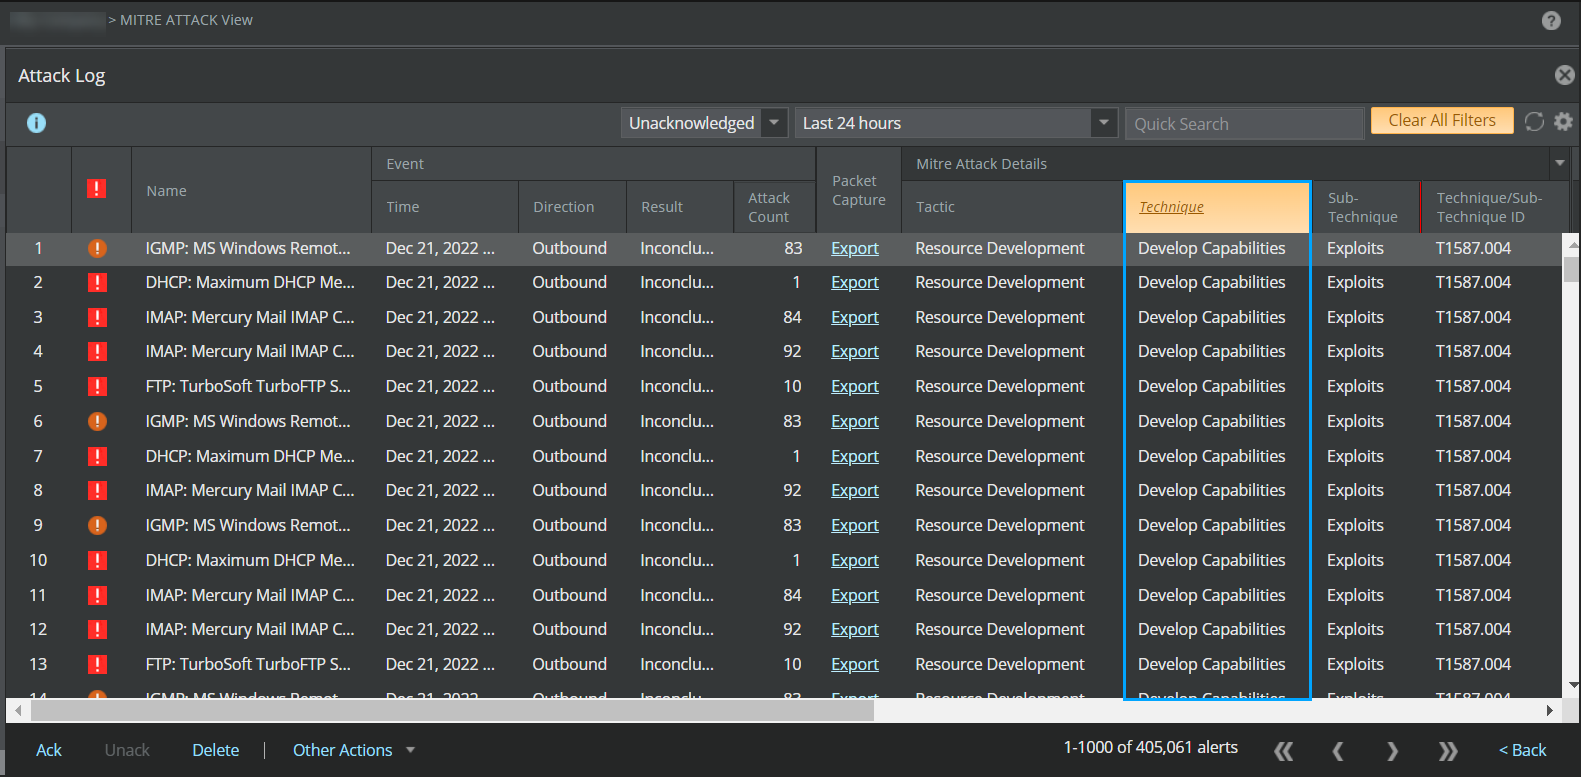
Click any hyperlinked technique under a specific tactic column in the MITRE ATTACK View page for which you want to view the attack details. It will redirect you to the Attack Log page with the selected technique applied as the filter. The Clear All Filters button color in the Attack Log page changes to orange which indicates that the filter is active.
The figure below shows the Attack Log page view after clicking the hyperlinked technique Develop capabilities under the tactic Resource Development in the MITRE ATTACK View page.
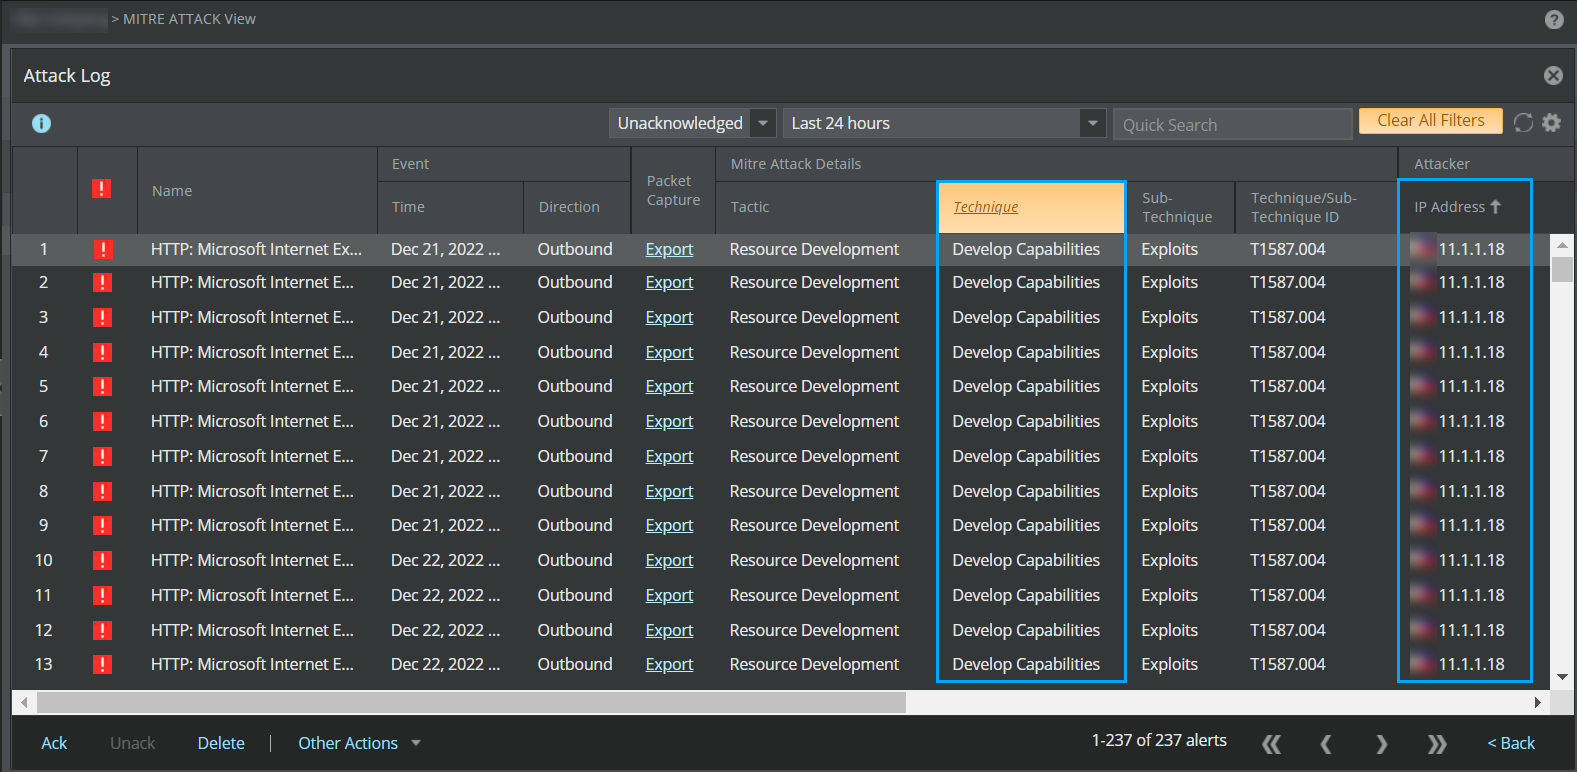
You can also apply the filters based on IP address and/or attack severity level in the MITRE ATTACK View page and then click any matching highlighted technique to view more filtered data in the Attack Log page. For example, the figure below shows the attack entries matching with technique Develop Capabilities and IP address 11.1.1.18 in the Attack Log page.
Analyzing attack details using matching sub-technique
Expand technique under a specific tactic column in the MITRE ATTACK View page to view the corresponding sub-technique(s) for which you want to view the attack details. You can then click any sub-technique of your preference. It will redirect you to the Attack Log page with the selected technique and sub-technique applied as filters.
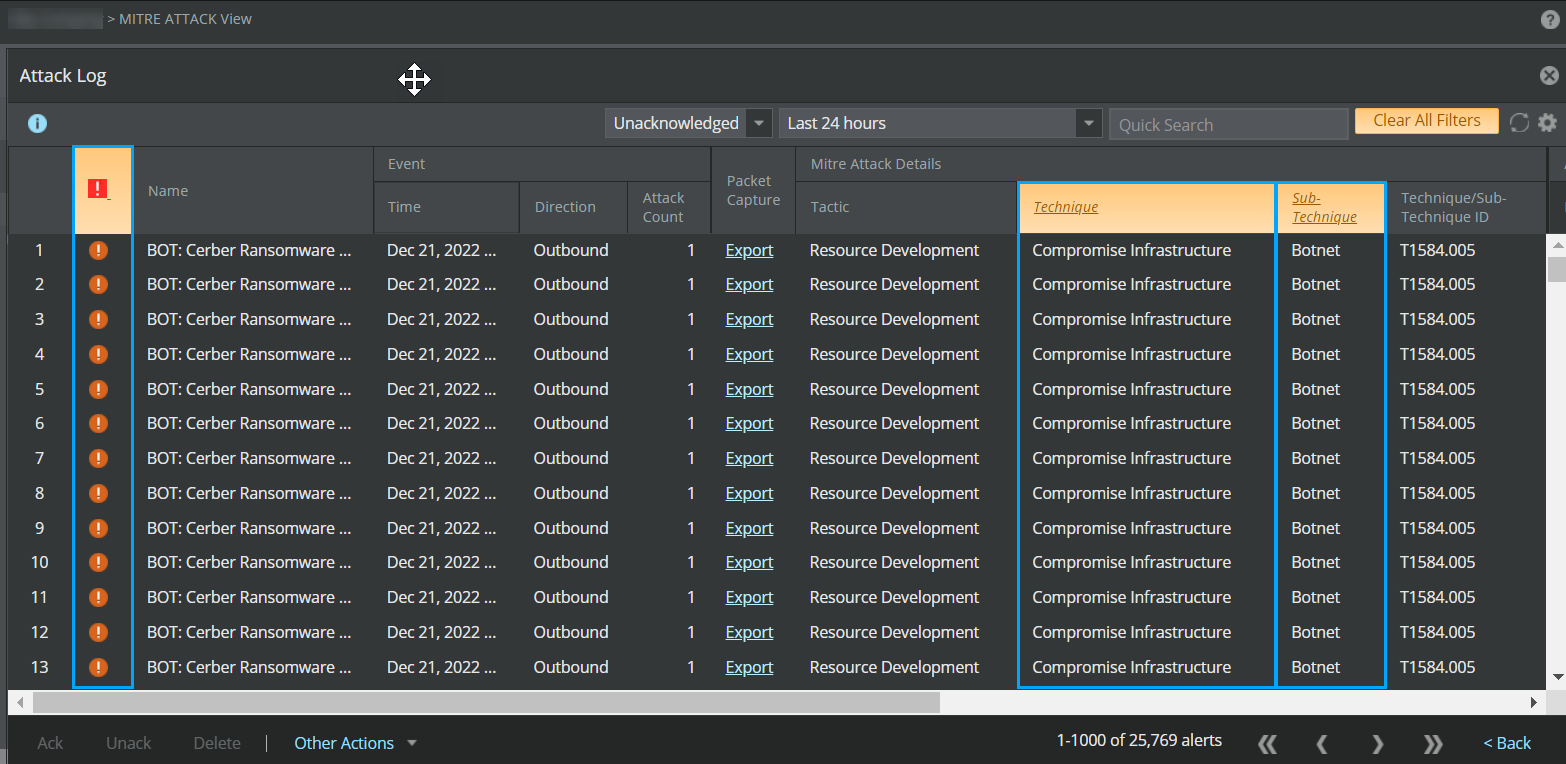
You can also apply the filters based on IP address and/or attack severity level in the MITRE ATTACK View page to get more filtered attack entries in the Attack Log page. For example, when medium attack severity is chosen as filter in the MITRE ATTACK View page, clicking the hyperlink for sub-technique Botnet under the corresponding technique Compromise Infrastructure shows specific attack entries in the Attack Log page with the selected technique, sub-technique, and severity level applied as filters.
Note the following:
You can further sort the filtered attack data by entering a keyword for any other applicable sub-technique, technique/sub-technique ID, IP address, or any other attributes in the Quick Search field. You can also apply filters for the same in the column level.
You can select any specific entry in this page and perform same actions as you can perform in Analysis → <Admin Domain Name> → Attack Log.
Mitre-based attack details are not shown for older alert data.
You can export and save the list of filtered data as a PDF file or CSV file from the Attack Log for future reference. To export, click Other Actions, select Save Attack Log as, and click the format in which you want the filtered data to be exported.
Click  or
 icon to close the Attack Log and go back to the MITRE ATTACK View page.