---
title: "Appendix: Audit Log Records"
slug: "appendix-audit-log-records-1"
tags: ["Certification", "IPS 11.1.x"]
updated: 2026-10-01T07:58:57Z
published: 2026-10-01T07:58:57Z
canonical: "docs.trellix.com/appendix-audit-log-records-1"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://docs.trellix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Appendix: Audit Log Records
This section describes the audit log records in relation to a user's activities. The general format of audit records is:
```
Time,Results,Category,Summary,Details,Domain,UserDate, Admin Domain, User, Attack Category, Action, Result, Description
```
An example of an audit record displayed in the GUI is:
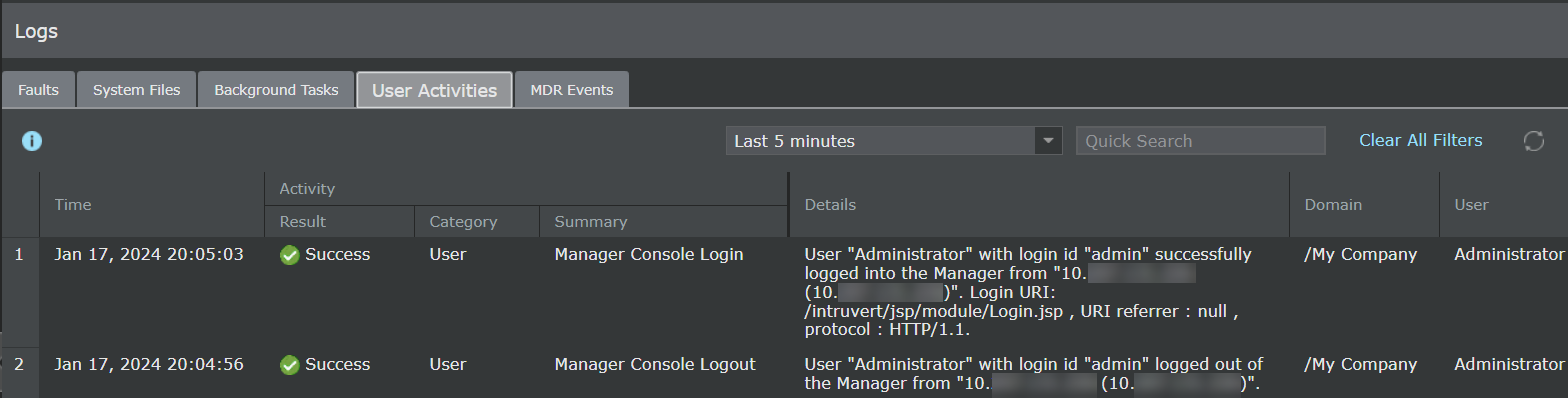
The following table documents the messages within audit log records generated by Trellix Intrusion Prevention System.
**Audit Log Records**
| Action | Log Message |
| --- | --- |
| Changes to the system time by an Administrator | Time has been changed |
| Communication between the Manager and Sensors | - **Enabling**: Successfully added sensor "*sensor_name*" - **Disabling**: Successfully deleted sensor "*sensor_name*" |
| Failure to establish a TLS Session | - Certificate having missing Extended keys - Mismatch between configured Server Name and Subject Alt Name in Imported certificate - The connection to syslog server *IP_Address:port_number* failed. Error: Syslog TCP connection failed. |
| Failure to establish an HTTPS Session | Mismatch between configured Server Name and Subject Alt Name in Imported certificate |
| Failure to establish an SSH session | - Disconnecting: Too many authentication failures [preauth] - Unable to negotiate with *IP_Address* port *port_number*: no matching host key type found. Their offer: *host_key_type* [preauth] - Unable to negotiate with *IP_Address* port *port_number*: no matching key exchange method found. Their offer: *key_exchange_method* [preauth] |
| Management activities of system data | - Read audit log - Successfully set Session Timeout - Logon Banner Configuration updated - Successfully set Password Content, Configuration is … |
| Trusted connections | - **Initiation**: - Pktlog Channel back up. Clear the Pktlog Channel Down event of sensor *sensor* - Alert Channel back up. Clear the Alert Channel Down event of sensor *sensor* - Syslog Client - Added to Retry Q - Syslog Client - Flushing and Shutting down - Request for Authentication for User name=*Username* - **Termination**: - The link on Port: *Port_identifier* is Down Count: *number*. The link between this port and the external device to which it is connected is down. - Received disconnect from *IP_Address* port *port_number*: disconnected by user - User "*User Name*" with login id "*Username*" logged off Trellix IPS Manager from "*Hostname* (*IP_Address*)" - **Failure**: - Certificate having missing Extended keys - Mismatch between configured Server Name and Subject Alt Name in Imported certificate - Received fatal alert: handshake_failure - Connection refused (Connection refused) - Disconnecting: Too many authentication failures [preauth] - Unable to negotiate with IP_Address port *port_number*: no matching host key type found. Their offer: *hostkey_type* [preauth] - Unable to negotiate with *IP_Address* port *port_number*: no matching key exchange method found. Their offer: *key_exchange_method* [preauth] |
| Unsuccessful attempt to validate an X.509 certificate | - Certificate having missing Extended keys - Mismatch between configured Server Name and Subject Alt Name in Imported certificate |
| Unsuccessful login attempts limit is met or exceeded | Login failed: Maximum allowable login attempts *number* have exceeded |
| Use of the identification and authentication mechanism | - Postponed keyboard-interactive/pam for *username* from *IP_Address* port *port_number* ssh2 [preauth] - Postponed publickey for *username* from *IP_Address* port *port_number* ssh2 [preauth] - Accepted keyboard-interactive/pam for *username* from *IP_Address* port *port_number* ssh2 - error: Could not load host key: *path_to_hostkey_file* - Failed keyboard-interactive/pam for *username* from *IP_Address* port *port_number* ssh2 - Failed publickey for *username* from *IP_Address* port *port_number* ssh2: RSA SHA256:*public_key_value* - User "*username*" failed to log in to Trellix IPS Manager from "*Hostname* (*IP_Address*)". Login URI: /intruvert/jsp/module/Login.jsp. URI referrer : [https://Hostname//intruvert/jsp/module/Login.jsp](https://Hostname//intruvert/jsp/module/Login.jsp) , protocol : HTTP/1.2 - Unknown login ID "*Username*". Login failed from "*Hostname* (*IP_Address*)". Login URI: /intruvert/jsp/module/Login.jsp. URI referrer : [https://Hostname//intruvert/jsp/module/Login.jsp](https://Hostname//intruvert/jsp/module/Login.jsp) , protocol : HTTP/1.2 - Starting Session *number* of user *Username* - Trellix IPS Manager Login failed at *timestamp* |
| User session terminated | - Removed session *number* - User "*User Name*" with login id "*Username*" logged out of the Manager from "*Hostname* (*IP_Address*)" - Close session: user *Username* from *IP_Address* port *port_number* id *number* |
**Manager FAU_GEN.1 Audit Records**
| Requirement | Auditable Events | Additional Audit Record Contents | Audit Logs |
| --- | --- | --- | --- |
| FAU_GEN.1 | - Start-up and shut-down of the audit functions - Auditable events for the not specified level of audit; and Administrative login and logout (name of user account shall be logged if individual user accounts are required for Administrators). - Changes to TSF data related to configuration changes (in addition to the information that a change occurred it shall be logged what has been changed). - Generating/import of, changing, or deleting of cryptographic keys (in addition to the action itself a unique key name or key reference shall be logged). - Resetting passwords (name of related user account shall be logged). | None | - Start-up and shut-down of the audit functions 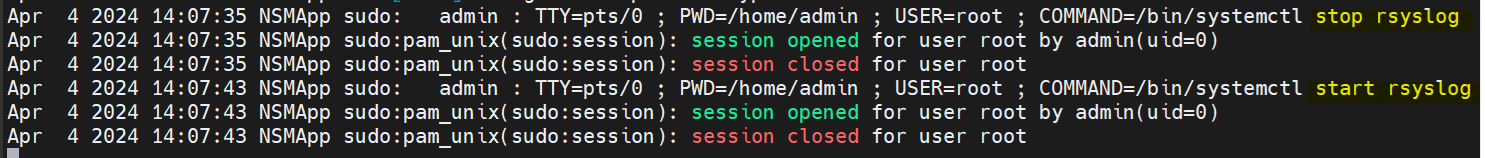 - Auditable events for the not specified level of audit; and Administrative login and logout (name of user account shall be logged if individual user accounts are required for Administrators). 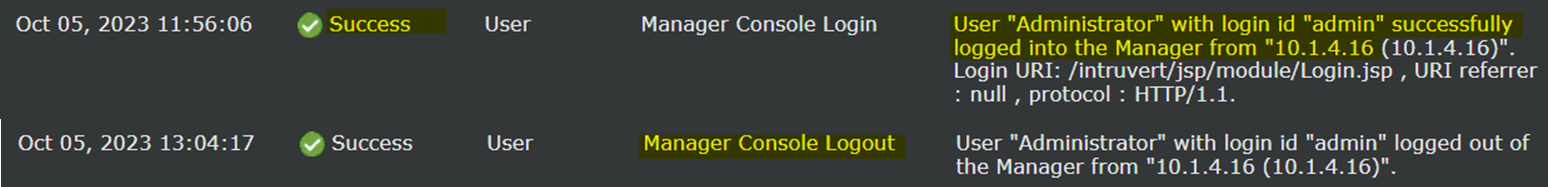 - Changes to TSF data related to configuration changes (in addition to the information that a change occurred it shall be logged what has been changed). 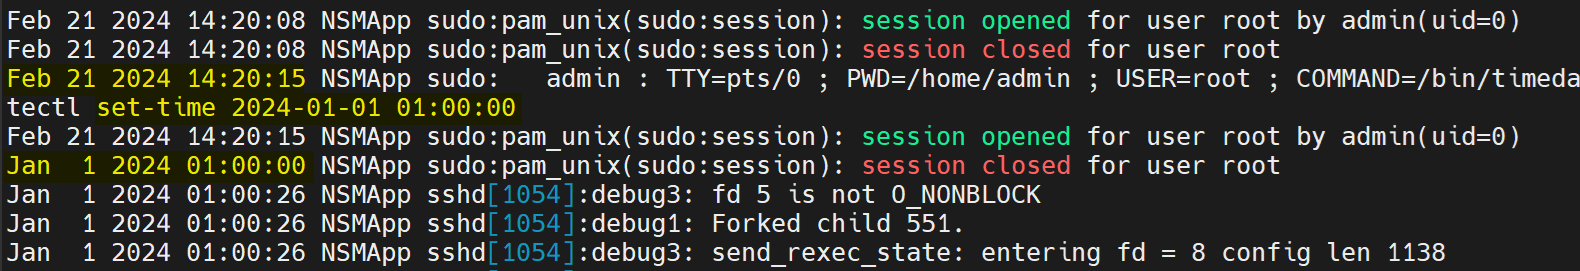 - Generating/import of, changing, or deleting of cryptographic keys (in addition to the action itself a unique key name or key reference shall be logged). 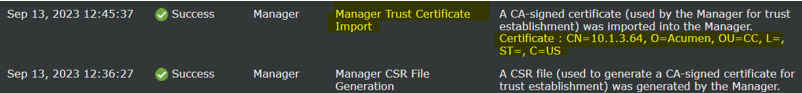 - Resetting passwords (name of related user account shall be logged).  |
| FAU_GEN_EXT.1 | None | None | - |
| FAU_GEN.2 | None | None | - |
| FAU_STG_EXT.1 | None | None | - |
| FCS_CKM.1 | None | None | - |
| FCS_CKM.2 | None | None | - |
| FCS_CKM.4 | None | None | - |
| FCS_COP.1/DataEncryption | None | None | - |
| FCS_COP.1/SigGen | None | None | - |
| FCS_COP.1/Hash | None | None | - |
| FCS_COP.1/KeyedHash | None | None | - |
| FCS_RBG_EXT.1 | None | None | - |
| FCS_TLSC_EXT.1 | Failure to establish a TLS Session | Reason for failure |  |
| FCS_TLSS_EXT.1 | Failure to establish a TLS Session | Reason for failure | 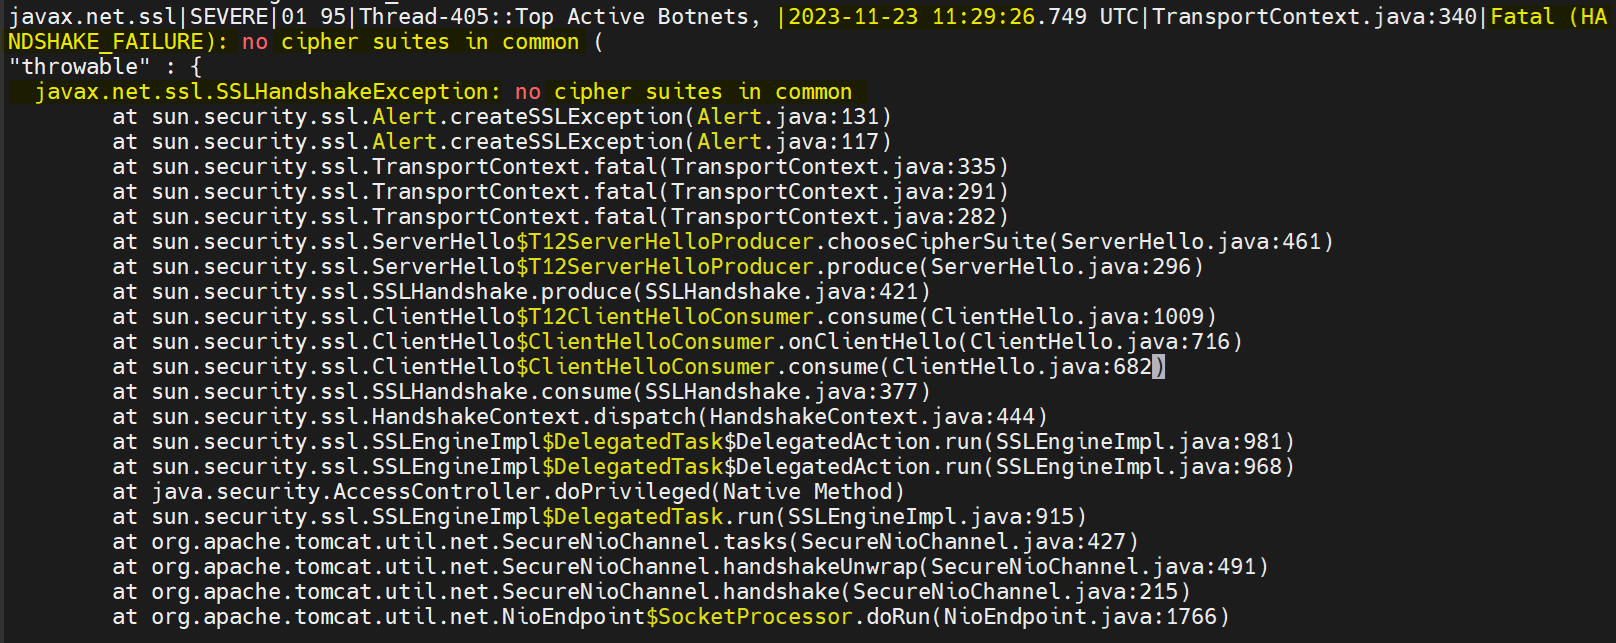 |
| FCS_TLSS_EXT.2 | Failure to establish a TLS Session | Reason for failure | 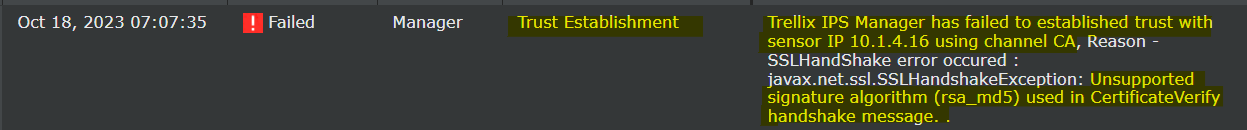 |
| FCO_CPC_EXT.1 | - Enabling communications between a pair of components - Disabling communications between a pair of components | Identities of the endpoints pairs enabled or disabled | Enabling communications: 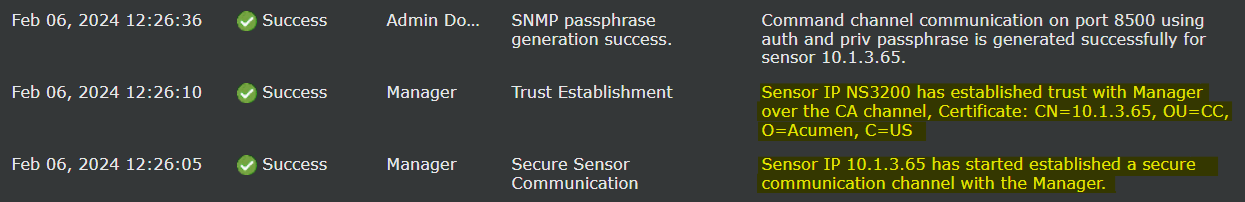 Disabling communications:  |
| FIA_AFL.1 | Unsuccessful login attempts limit is met or exceeded. | Origin of the attempt (e.g., IP address). | Web GUI: 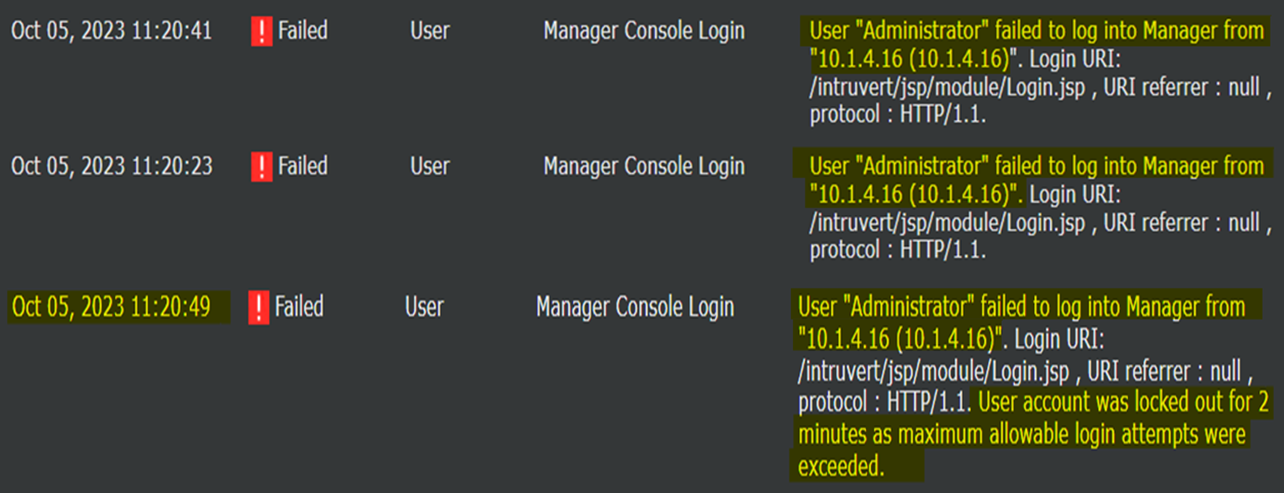 SSH:  |
| FIA_PMG_EXT.1 | None | None | - |
| FIA_UIA_EXT.1 | All use of the identification and authentication mechanism | Origin of the attempt (e.g., IP address) | Console:  SSH: 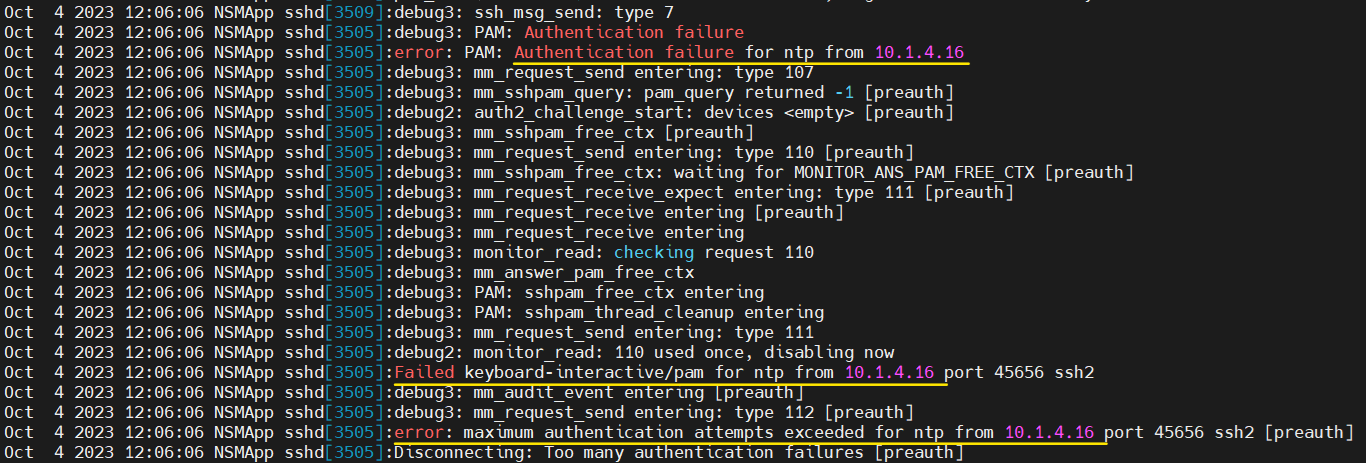 Web GUI:  |
| FIA_UAU_EXT.2 | All use of the identification and authentication mechanism | Origin of the attempt (e.g., IP address) | Console:  SSH: 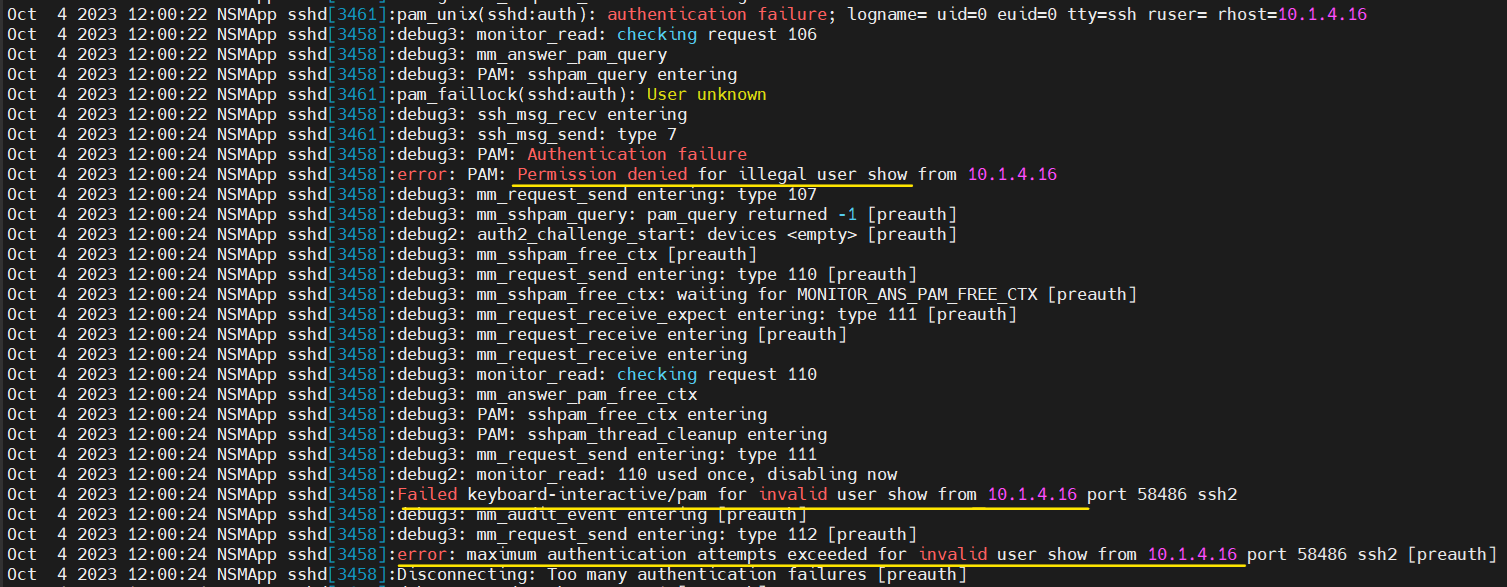 Web GUI:  |
| FIA_UAU.7 | None | None | - |
| FIA_X509_EXT.1/Rev | Unsuccessful attempt to validate a certificate | Reason for failure |  |
| FIA_X509_EXT.1/ITT | Unsuccessful attempt to validate a certificate | Reason for failure | 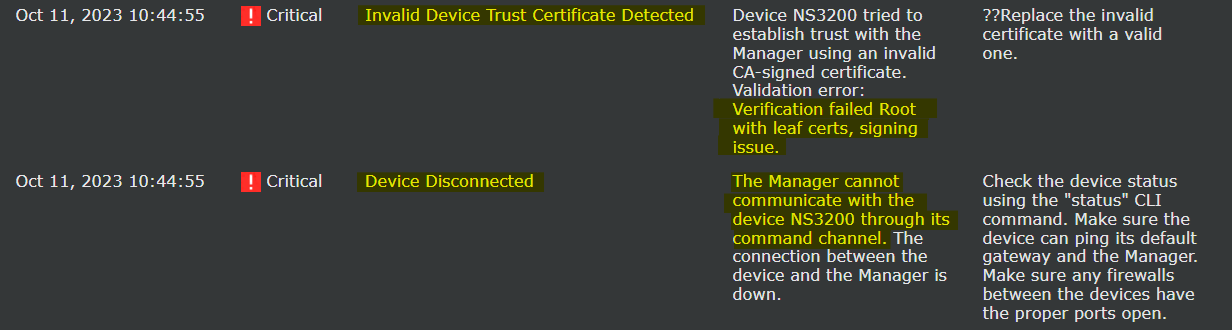 |
| FIA_X509_EXT.2 | None | None | - |
| FIA_X509_EXT.3 | None | None | - |
| FMT_MOF.1/ManualUpdate | Any attempt to initiate a manual update | None |  |
| FMT_MTD.1/CoreData | None | None | - |
| FMT_SMF.1 | All management activities of TSF data. | None | Refer to the below table Manager Management Functions |
| FMT_SMR.2 | None | None | - |
| FPT_APW_EXT.1 | None | None | - |
| FPT_ITT.1 | - Initiation of the trusted channel - Termination of the trusted channel - Failure of the trusted channel functions | Identification of the initiator and target of failed trusted channels establishment attempt | Initiation of trusted channel:  Termination of trusted channel:  Failure of trusted channel functions: 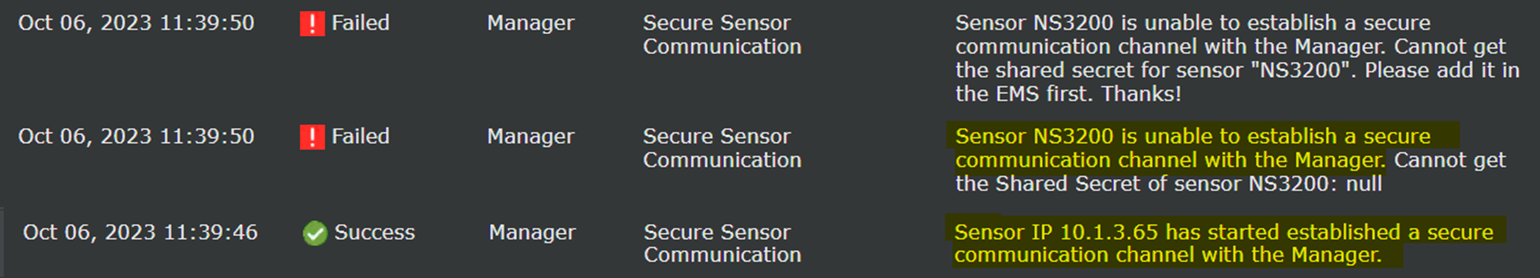 |
| FPT_SKP_EXT.1 | None | None | - |
| FPT_STM_EXT.1 | Discontinuous changes to time - either Administrator actuated or changed via an automated process | For discontinuous changes to time: The old and new values for the time. Origin of the attempt to change time for success and failure (e.g., IP address) |  |
| FPT_TST_EXT.1 | None | None | - |
| FPT_TUD_EXT.1 | Initiation of update; result of the update attempt (success or failure) | None | 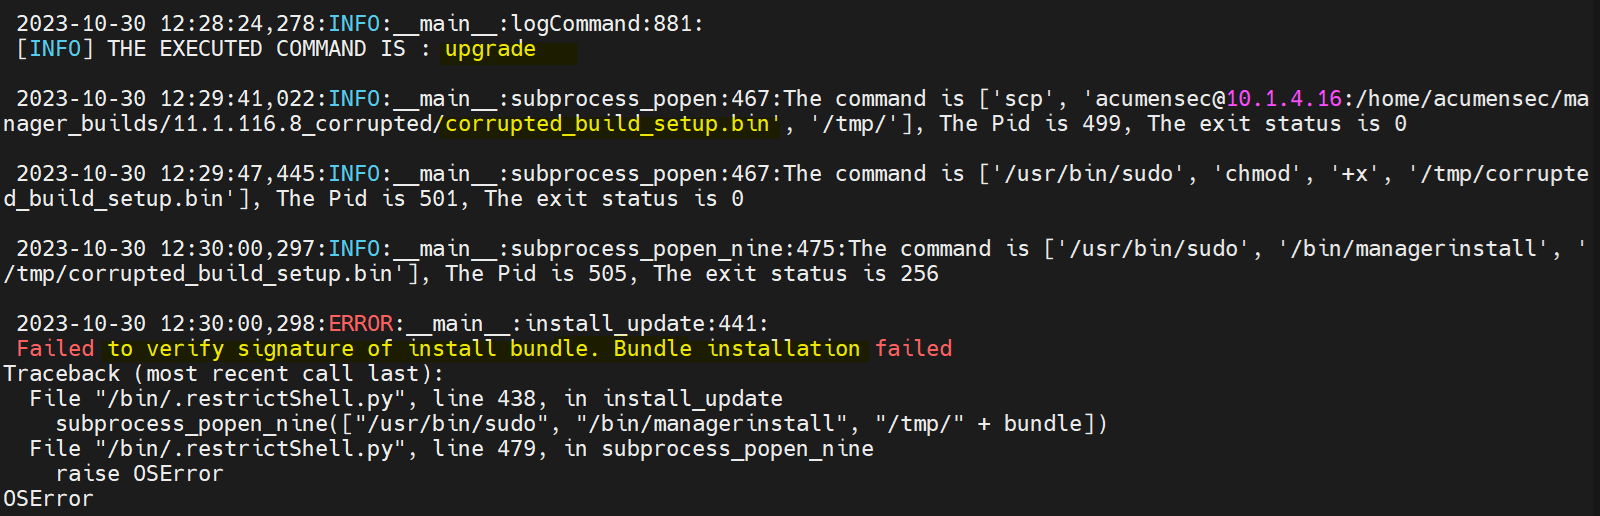 |
| FTA_SSL_EXT.1 | The termination of a local session by the session locking mechanism | None |  |
| FTA_SSL.3 | The termination of a remote session by the session locking mechanism | None | SSH: 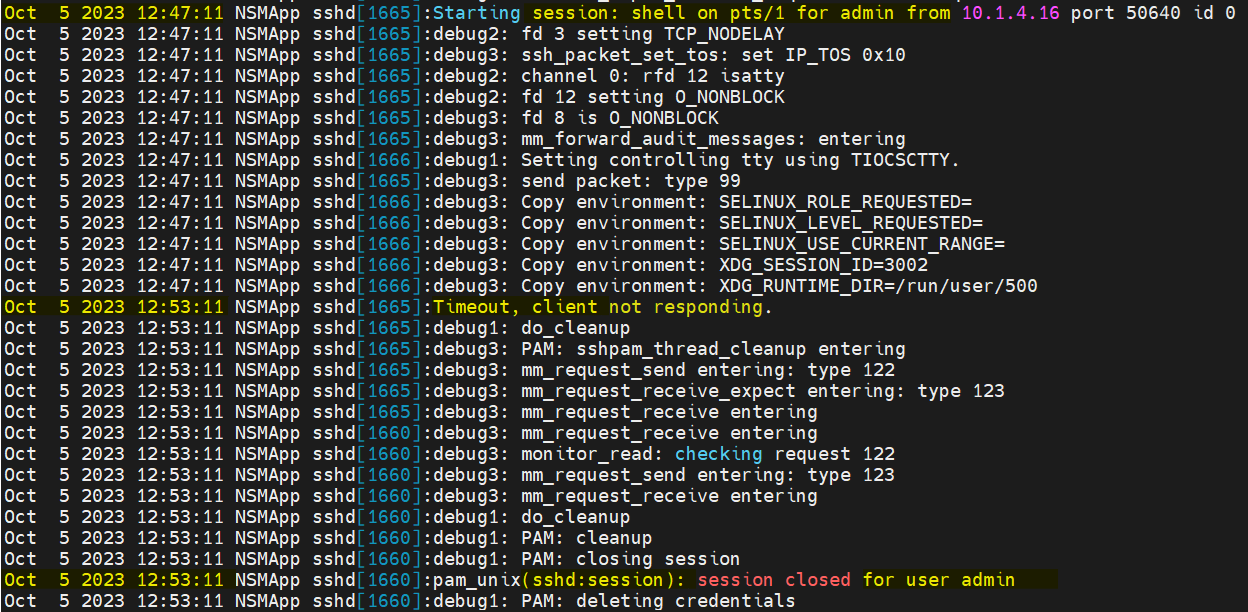 Web GUI: 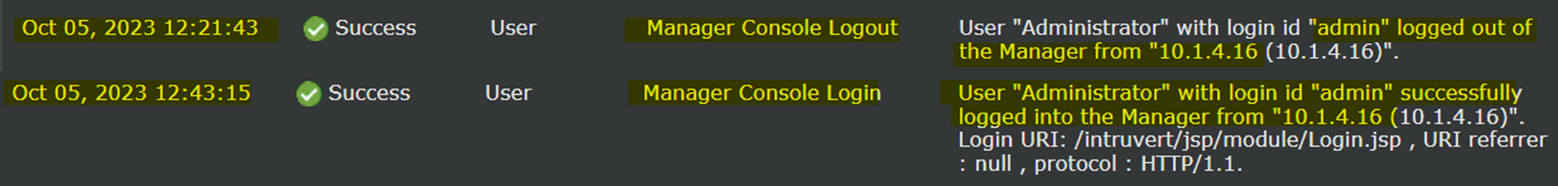 |
| FTA_SSL.4 | The termination of an interactive session | None | SSH:  WebGUI:  Console:  |
| FTA_TAB.1 | None | None | - |
| FTP_ITC.1 | - Initiation of the trusted channel - Termination of the trusted channel - Failure of the trusted channel functions | Identification of the initiator and target of failed trusted channels establishment attempt | Initiation of the trusted channel:  Termination of the trusted channel: 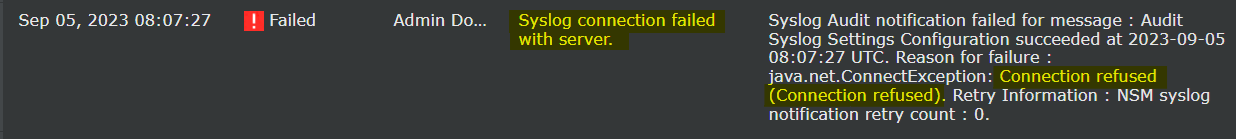 Failure of the trusted channel functions:  |
| FTP_TRP.1/Admin | - Initiation of the trusted channel. - Termination of the trusted channel. - Failure of the trusted channel functions. | Identification of the claimed user identity. | **Initiation of trusted channel** SSH: 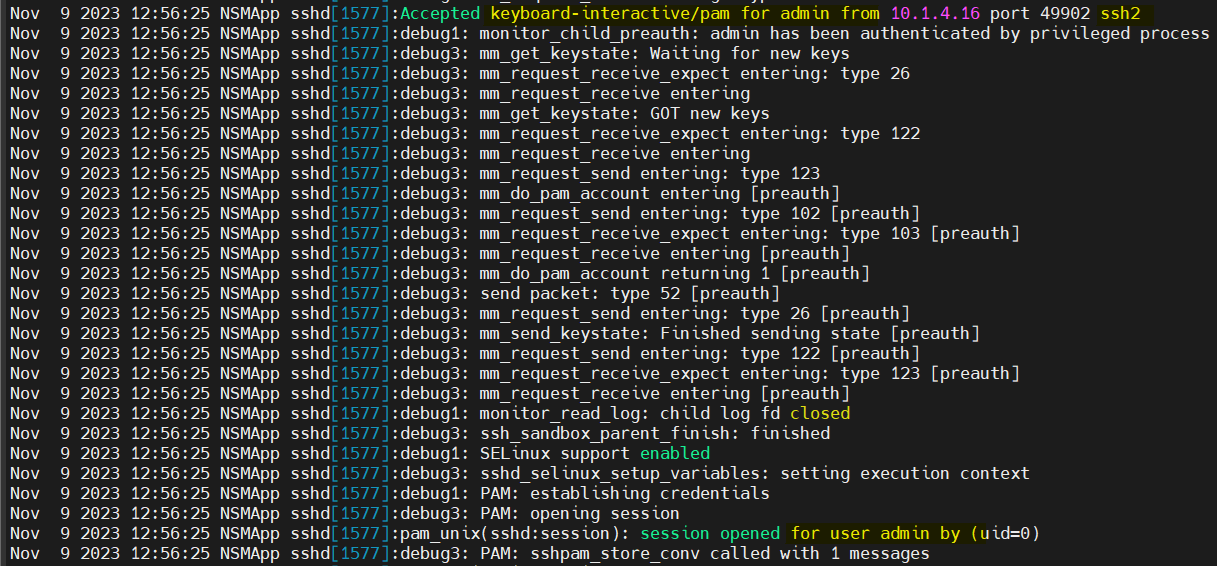 Web GUI:  **Termination of the trusted channel:** SSH:  Web GUI:  **Failure of trusted channel functions:** SSH:  Web GUI:  |
| FAU_STG_EXT.4 | None | None | - |
| FCS_HTTPS_EXT.1 | Failure to establish a HTTPS Session | Reason for failure | 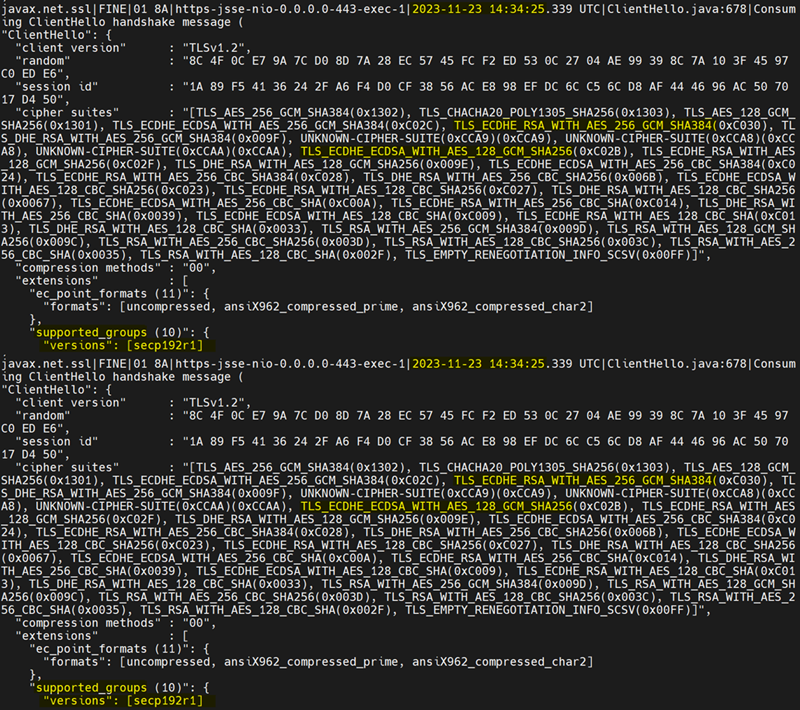 |
| FCS_SSHS_EXT.1 | Failure to establish an SSH session | Reason for failure | 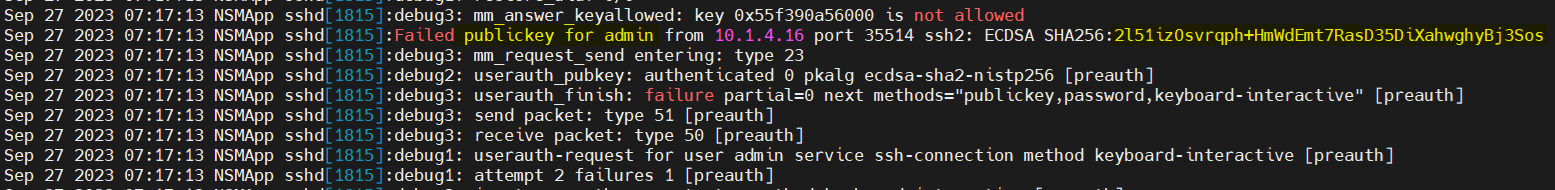 |
**Manager Management Functions**
| Management Functions | Test cases |
| --- | --- |
| Ability to administer the TOE locally and remotely | Console:  SSH:  WebGUI:  |
| Ability to configure the access banner |  |
| Ability to configure the session inactivity time before session termination or locking |  |
| Ability to update the TOE, and to verify the updates using digital signature capability prior to installing those updates | Positive update: 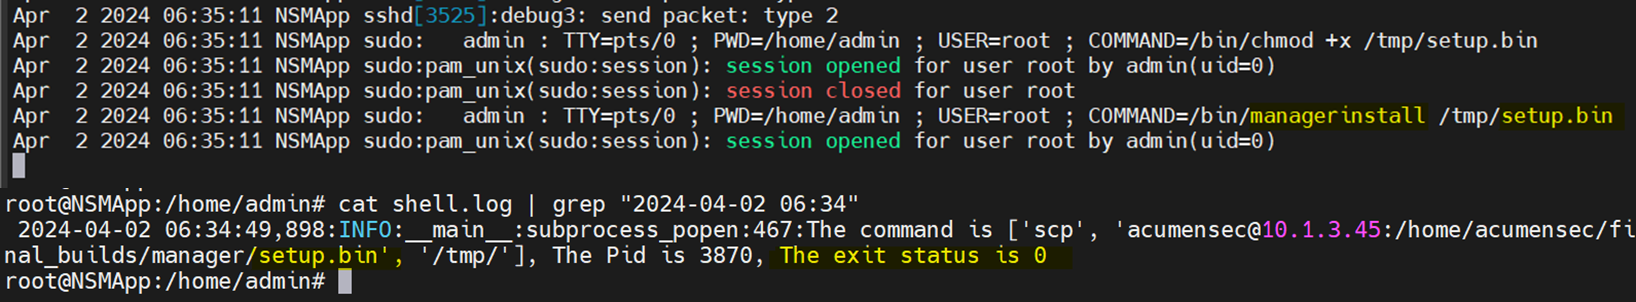 Negative update:  |
| Ability to configure the authentication failure parameters for FIA_AFL.1 | 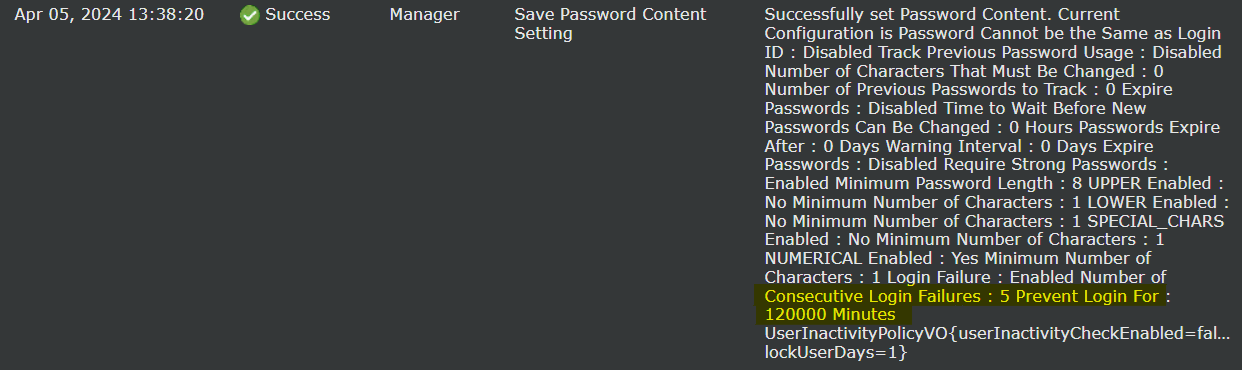 |
| Ability to configure audit behaviour (e.g. changes to storage locations for audit; changes to behaviour when local audit storage space is full); | 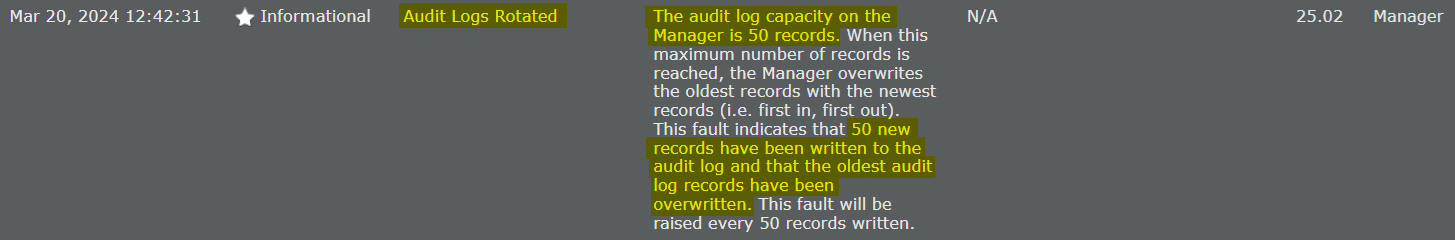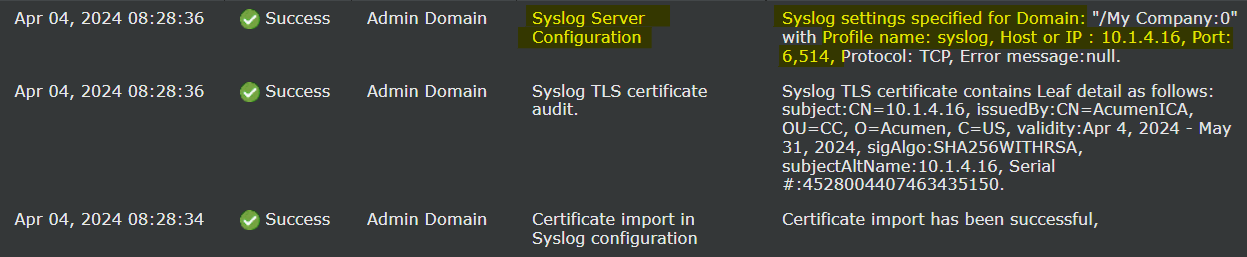 |
| Ability to modify the behaviour of the transmission of audit data to an external IT entity |  |
| Ability to configure the cryptographic functionality |  |
| Ability to import X.509v3 certificates to the TOE's trust store |  |
| Ability to set the time which is used for timestamps |  |
| Ability to re-enable an Administrator account |  |
| Ability to manage the trusted public keys database | 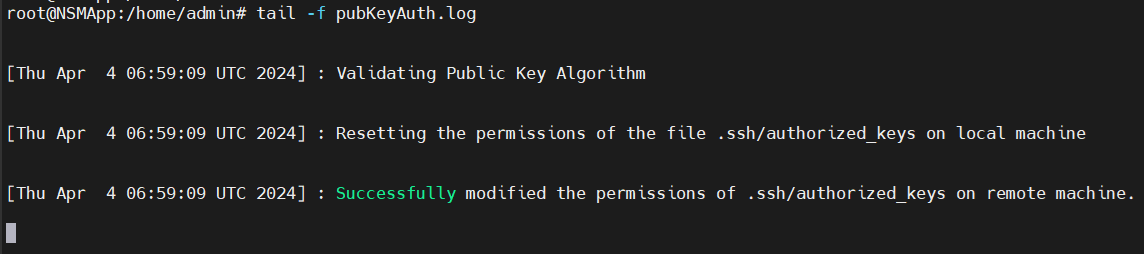 |
| Ability to configure the interaction between TOE components | 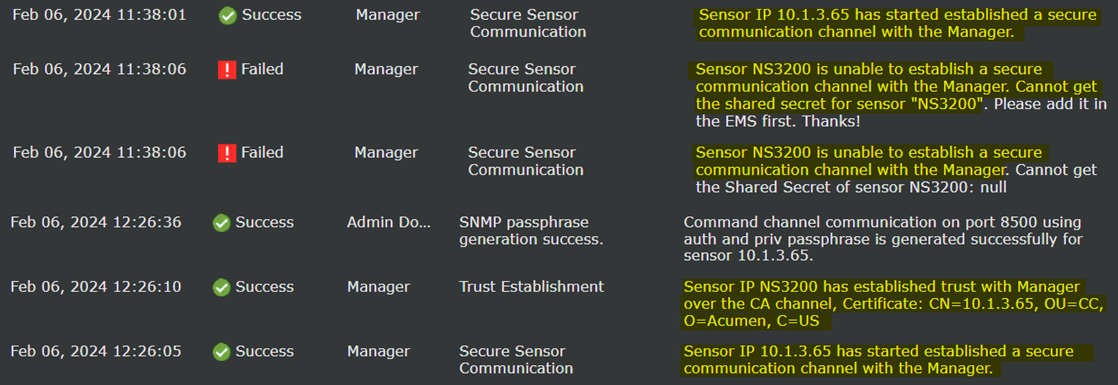 |
**Sensor FAU_GEN.1 Audit Records**
| Requirement | Auditable Events | Additional Audit Record Contents | Audit Logs |
| --- | --- | --- | --- |
| FAU_GEN.1 | - Start-up and shut-down of the audit functions - Auditable events for the not specified level of audit; and Administrative login and logout (name of user account shall be logged if individual user accounts are required for Administrators). - Changes to TSF data related to configuration changes (in addition to the information that a change occurred it shall be logged what has been changed) - Generating/import of, changing, or deleting of cryptographic keys (in addition to the action itself a unique key name or key reference shall be logged) - Resetting passwords (name of related user account shall be logged) | None | - Start-up and shut-down of the audit functions  - Auditable events for the not specified level of audit; and Administrative login and logout (name of user account shall be logged if individual user accounts are required for Administrators). 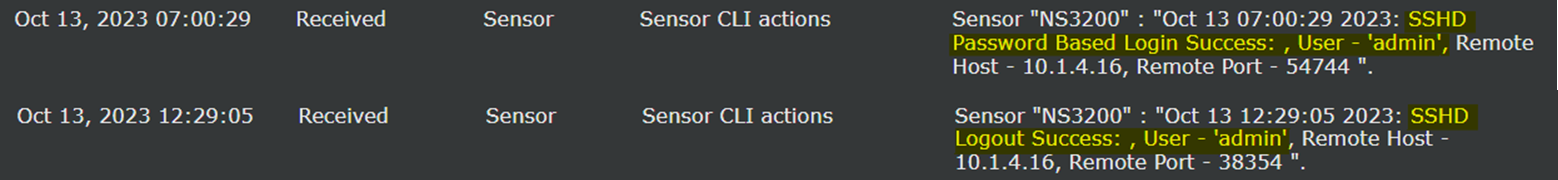 - Changes to TSF data related to configuration changes (in addition to the information that a change occurred it shall be logged what has been changed)  - Generating/import of, changing, or deleting of cryptographic keys (in addition to the action itself a unique key name or key reference shall be logged)  - Resetting passwords (name of related user account shall be logged)  |
| FAU_GEN.1/IPS | None | None | - |
| FAU_GEN_EXT.1 | None | None | - |
| FAU_GEN.2 | None | None | - |
| FAU_STG_EXT.5 | None | None | - |
| FCS_CKM.1 | None | None | - |
| FCS_CKM.2 | None | None | - |
| FCS_CKM.4 | None | None | - |
| FCS_COP.1/DataEncryption | None | None | - |
| FCS_COP.1/SigGen | None | None | - |
| FCS_COP.1/Hash | None | None | - |
| FCS_COP.1/KeyedHash | None | None | - |
| FCS_RBG_EXT.1 | None | None | - |
| FCS_SSHC_EXT.1 | Failure to establish an SSH session | Reason for failure | 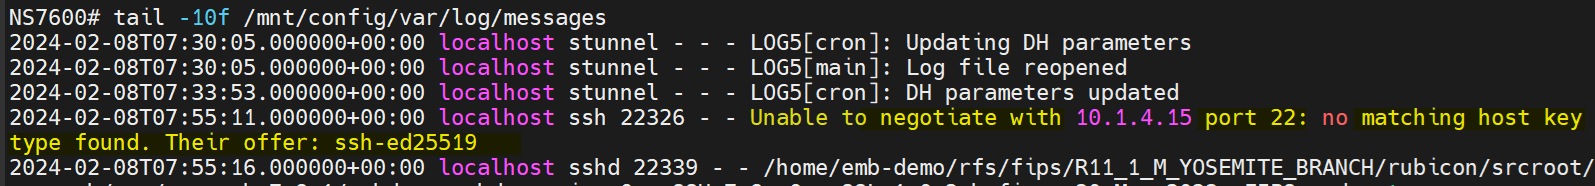 |
| FCS_SSHS_EXT.1 | Failure to establish an SSH session | Reason for failure | 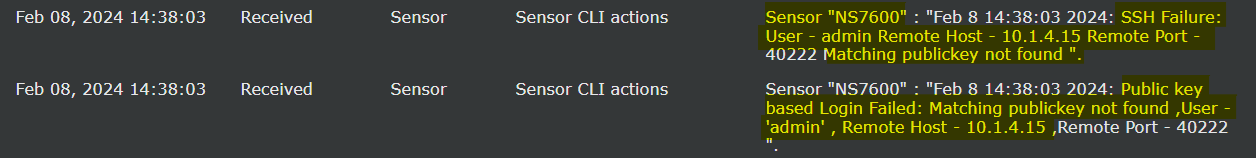 |
| FCS_TLSC_EXT.2 | Failure to establish a TLS Session | Reason for failure | 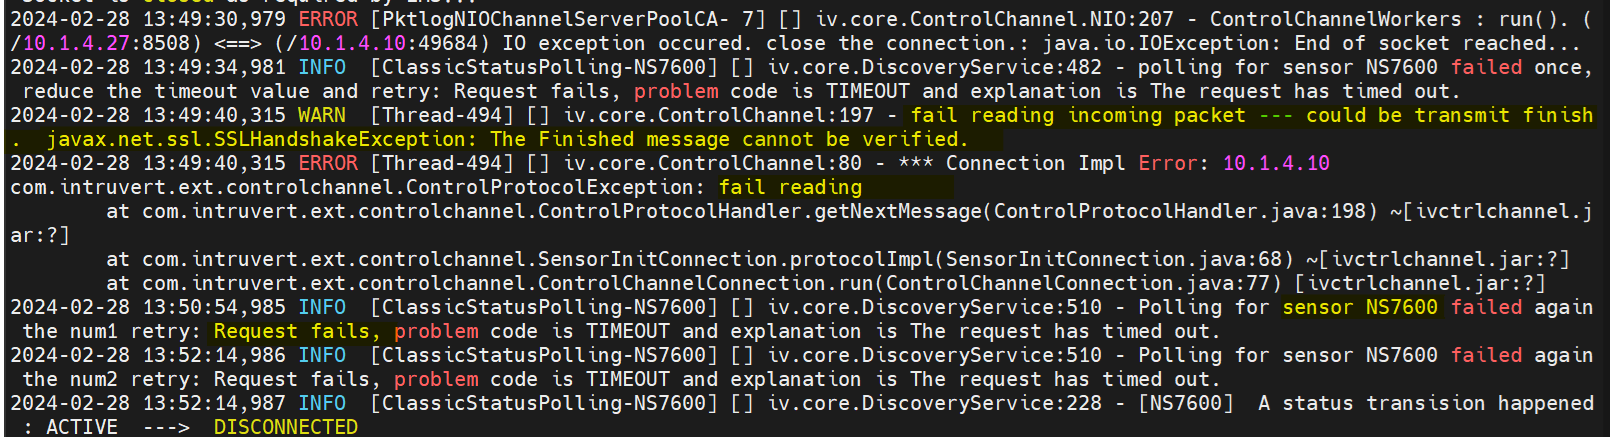 |
| FCO_CPC_EXT.1 | - Enabling communications between a pair of components - Disabling communications between a pair of components | Identities of the endpoints pairs enabled or disabled | Enabling communications: 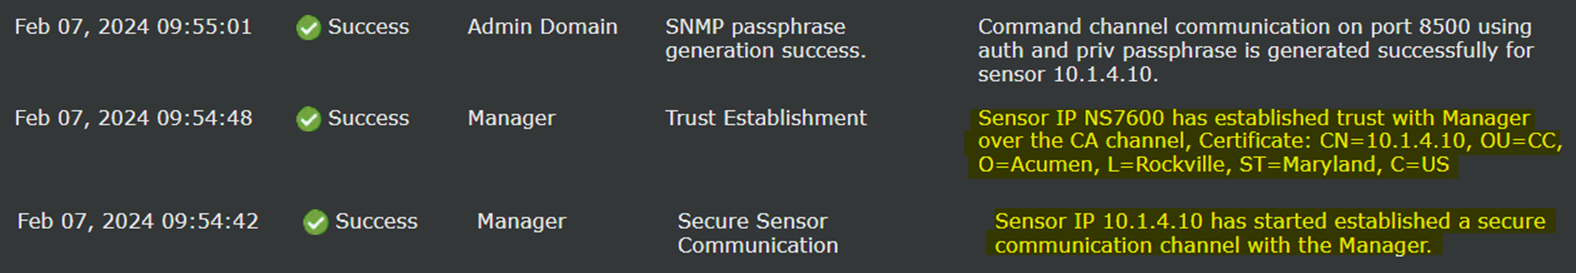 Disabling communications: 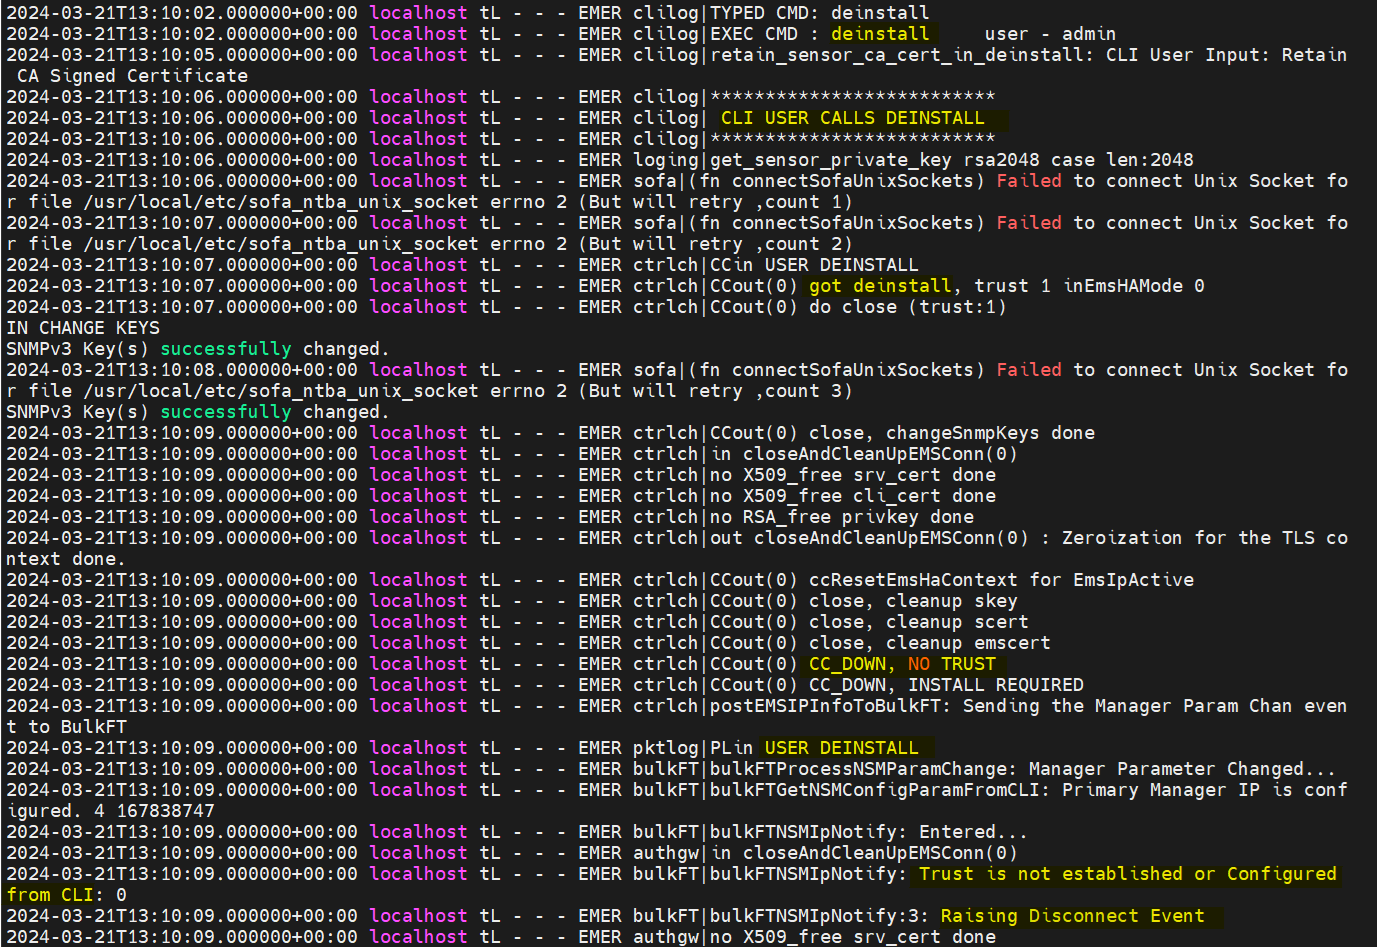 |
| FIA_AFL.1 | Unsuccessful login attempts limit is met or exceeded. | Origin of the attempt (e.g., IP address). | 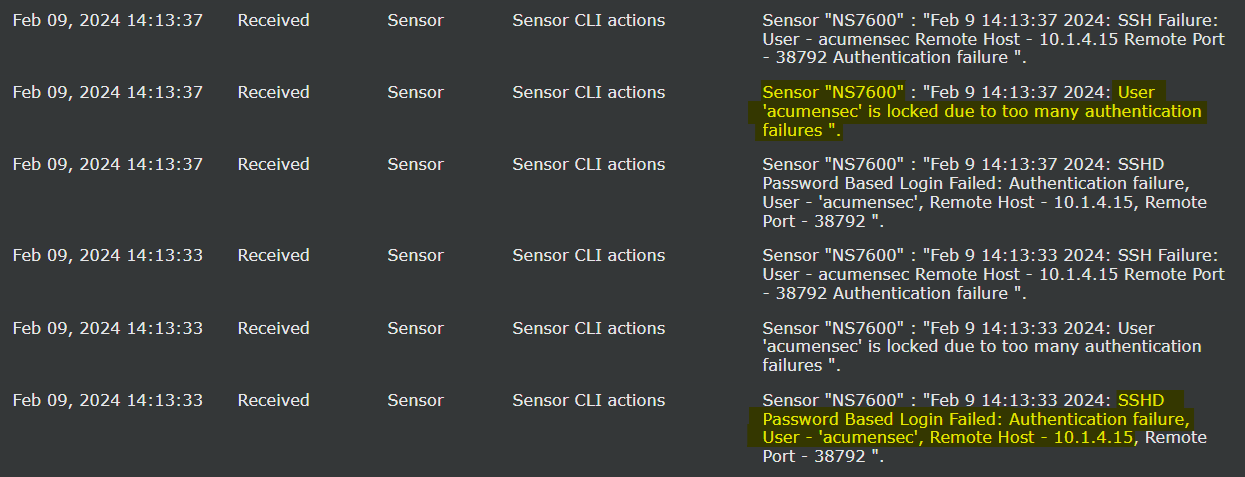 |
| FIA_PMG_EXT.1 | None | None | - |
| FIA_UIA_EXT.1 | All use of the identification and authentication mechanism | Origin of the attempt (e.g., IP address) | Console:  SSH:  |
| FIA_UAU_EXT.2 | All use of the identification and authentication mechanism | Origin of the attempt (e.g., IP address) | Console:  SSH:  |
| FIA_UAU.7 | None | None | - |
| FIA_X509_EXT.1/ITT | Unsuccessful attempt to validate a certificate | Reason for failure |  |
| FIA_X509_EXT.3 | None | None | - |
| FMT_MOF.1/ManualUpdate | Any attempt to initiate a manual update | None | 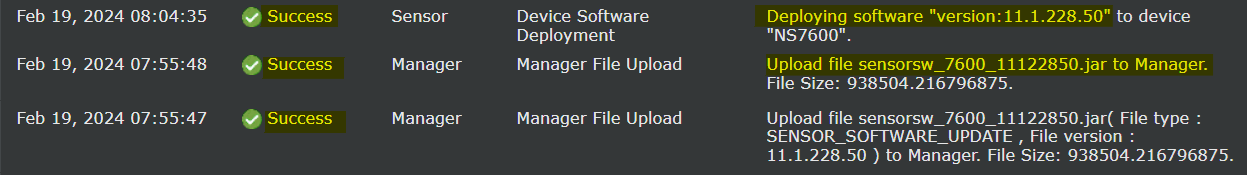 |
| FMT_MTD.1/CoreData | None | None | - |
| FMT_SMF.1 | All management activities of TSF data. | None | Refer to the below table Sensor Management Functions |
| FMT_SMR.2 | None | None | - |
| FPT_APW_EXT.1 | None | None | - |
| FPT_ITT.1 | - Initiation of the trusted channel - Termination of the trusted channel - Failure of the trusted channel functions | Identification of the initiator and target of failed trusted channels establishment attempt | Initiation of trusted channel:  Termination of trusted channel:  Failure of trusted channel functions: 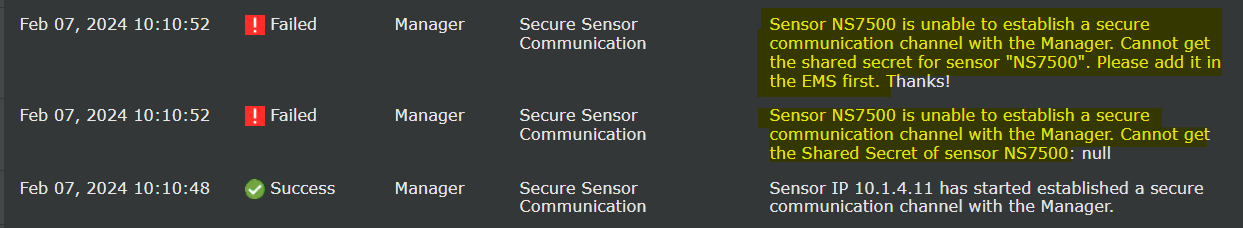 |
| FPT_SKP_EXT.1 | None | None | - |
| FPT_STM_EXT.1 | Discontinuous changes to time - either Administrator actuated or changed via an automated process | For discontinuous changes to time: The old and new values for the time. Origin of the attempt to change time for success and failure (e.g., IP address) |  |
| FPT_TST_EXT.1 | None | None | - |
| FPT_TUD_EXT.1 | Initiation of update; result of the update attempt (success or failure) | None | 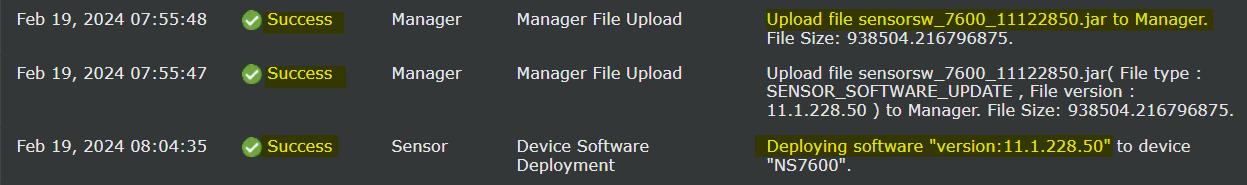 |
| FTA_SSL_EXT.1 | The termination of a local session by the session locking mechanism | None |  |
| FTA_SSL.3 | The termination of a remote session by the session locking mechanism | None | 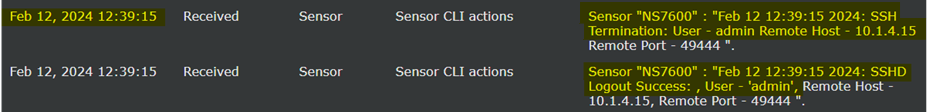 |
| FTA_SSL.4 | The termination of an interactive session | None | SSH:  Console:  |
| FTA_TAB.1 | None | None | - |
| FTP_TRP.1/Admin | - Initiation of the trusted channel - Termination of the trusted channel - Failure of the trusted channel functions | Identification of the claimed user identity | Initiation of the trusted channel: 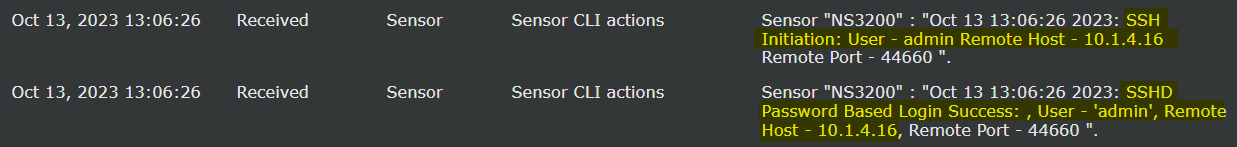 Termination of the trusted channel: 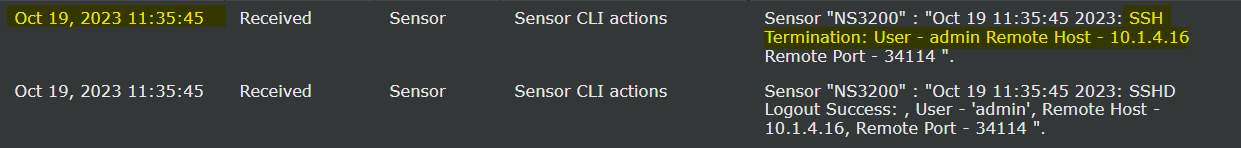 Failure of the trusted channel functions:  |
| FMT_SMF.1/IPS | Modification of an IPS policy element | Identifier or name of the modified IPS policy element (e.g. which signature, baseline, or known-good/known-bad list was modified) | 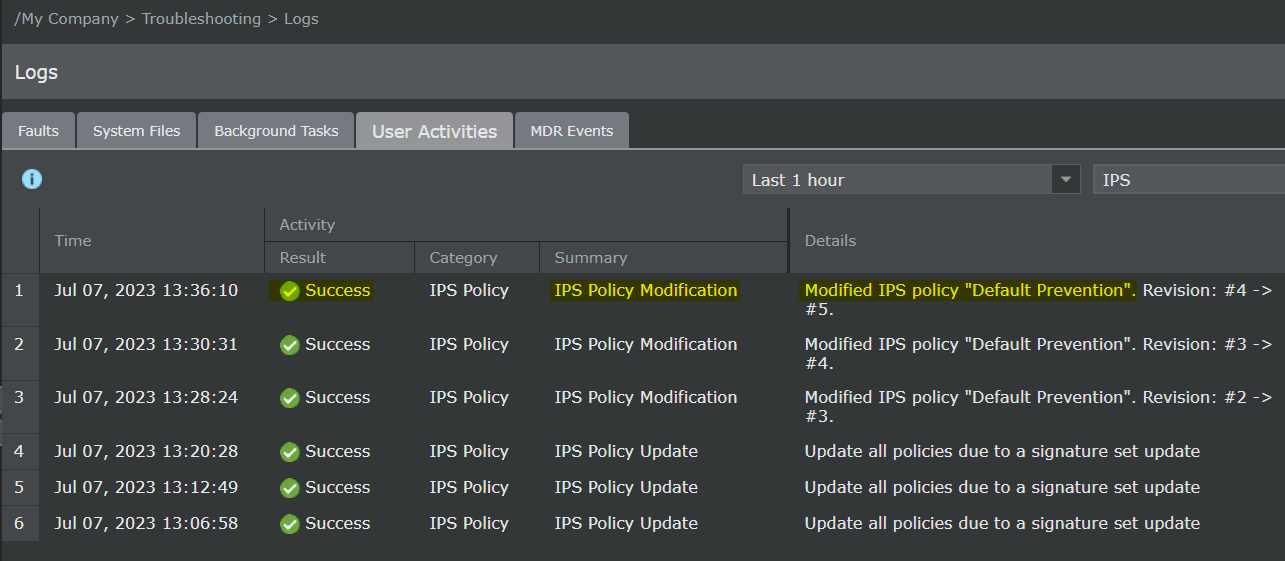 |
| IPS_ABD_EXT.1 | Inspected traffic matches an anomaly-based IPS policy | - Source and destination IP addresses - The content of the header fields that were determined to match the policy - TOE interface that received the packet - Aspect of the anomaly-based IPS policy rule that triggered the event (e.g. throughput, time of day, frequency, etc.) - Network-based action by the TOE (e.g. allowed, blocked, sent reset to source IP, sent blocking notification to firewall) | 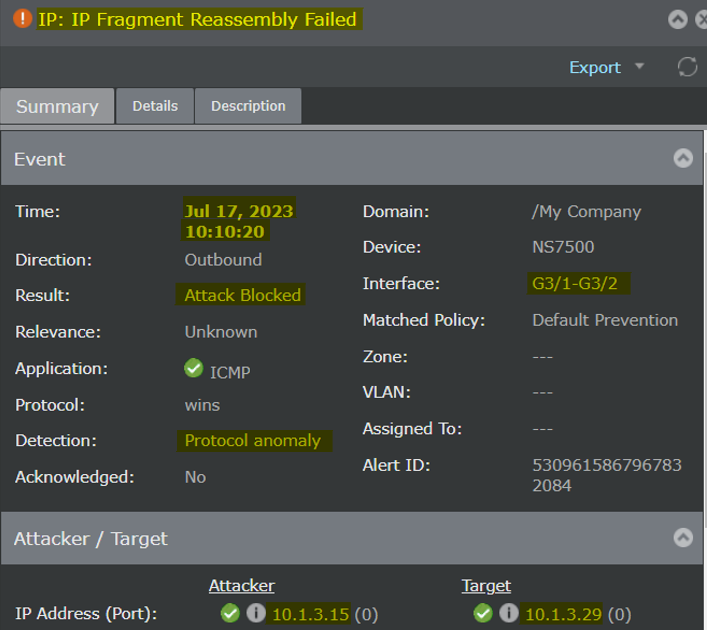 |
| IPS_IPB_EXT.1 | Inspected traffic matches a list of known-good or known-bad addresses applied to an IPS policy | - Source and destination IP addresses (and, if applicable, indication of whether the source and/or destination address matched the list) - TOE interface that received the packet. - Network-based action by the TOE (e.g. allowed, blocked, sent reset) | 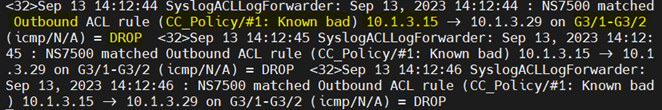 |
| IPS_SBD_EXT.1 | Inspected traffic matches a signature-based IPS rule with logging enabled | - Name or identifier of the matched signature. - Source and destination IP addresses - The content of the header fields that were determined to match the signature - TOE interface that received the packet - Network-based action by the TOE (e.g. allowed, blocked, sent reset) | 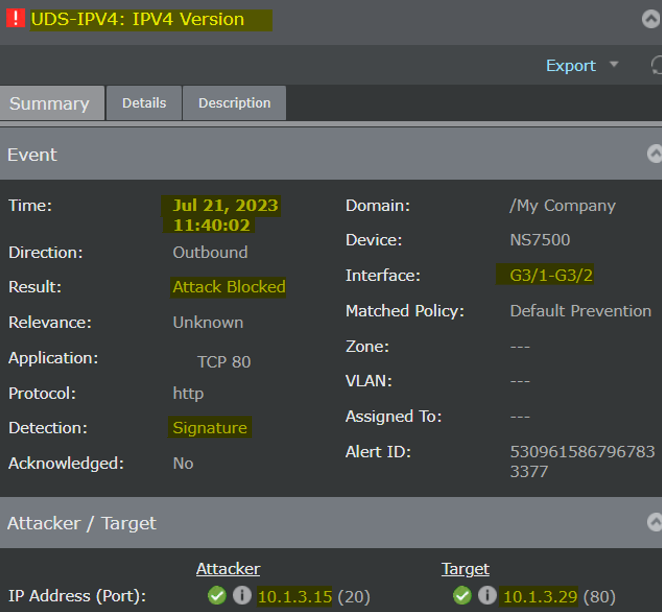 |
**Sensor Management Functions**
| Management Functions | Test cases |
| --- | --- |
| Ability to administer the TOE locally and remotely | SSH:  Console:  |
| Ability to configure the access banner |  |
| Ability to configure the session inactivity time before session termination or locking |  |
| Ability to update the TOE, and to verify the updates using digital signature capability prior to installing those updates | Positive update: 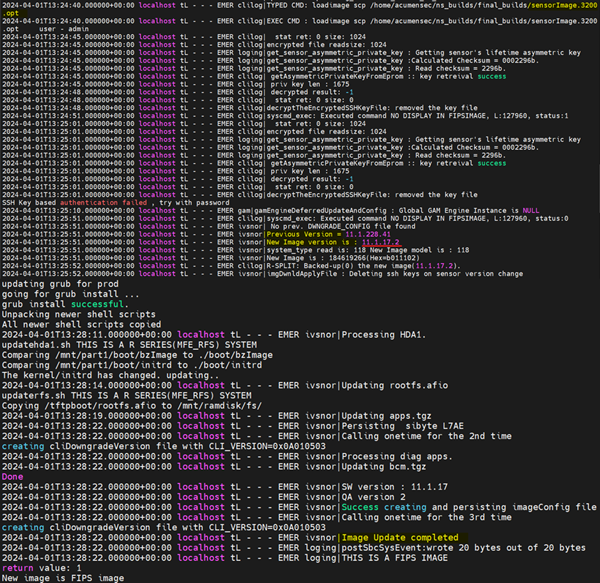 Negative update:  |
| Ability to configure the authentication failure parameters for FIA_AFL.1 |  |
| Ability to configure audit behaviour (e.g. changes to storage locations for audit; changes to behaviour when local audit storage space is full); |  |
| Ability to modify the behaviour of the transmission of audit data to an external IT entity |  |
| Ability to configure the cryptographic functionality |  |
| Ability to import X.509v3 certificates to the TOE's trust store |  |
| Ability to set the time which is used for timestamps |  |
| Ability to re-enable an Administrator account |  |
| Ability to manage the trusted public keys database |  |
| Ability to configure the interaction between TOE components | 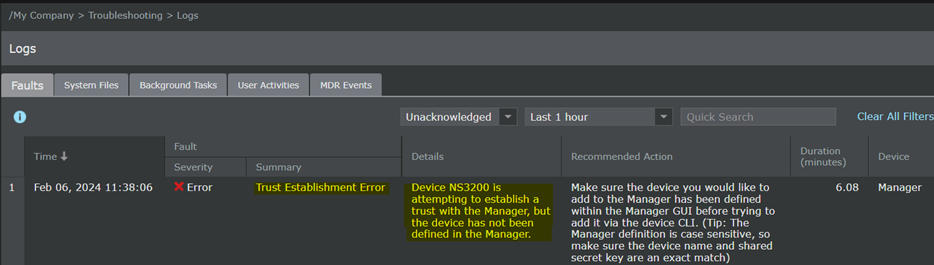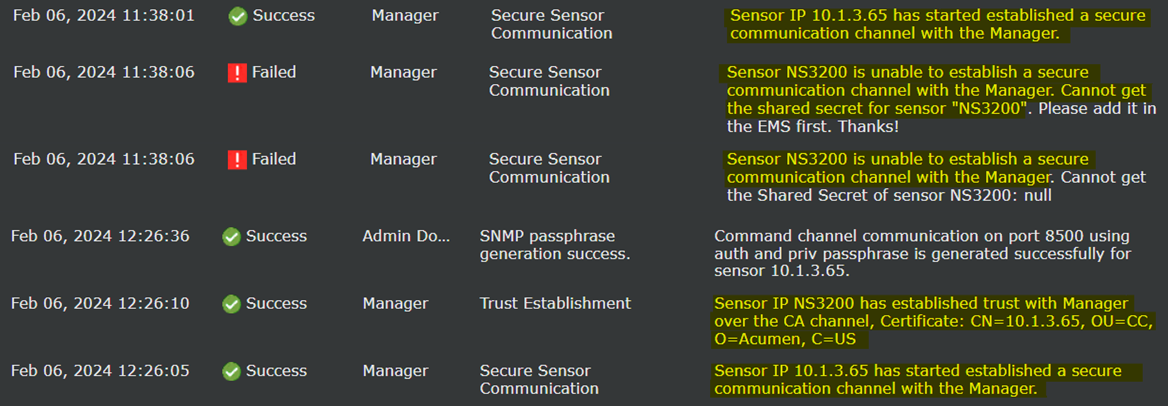 |