EIA resides on the endpoint where it collects details about the executables that initiate traffic. When integration with EIA is enabled, EIA sends the executable information to the NTBA Appliance, which uses it to enhance its analysis, such as determining which endpoints are infected or are at risk of infection.
The communication between the EIA and the NTBA Appliance is through the Datagram Transport Layer Security (DTLS) protocol with the EIA as the client and the NTBA Appliance as the server. The artifacts for a file are sent to NTBA using the Transport Layer Security (TLS) channel.
EIA and NTBA can integrate and communicate in either static or dynamic mode. If the DTLS channel doesn't exist when the packet is sent to EIA, then in:
Static mode - Based on the pre-configured NTBA and EIA details, a DTLS channel is created. EIA sends the metadata to mapped NTBA.
Dynamic mode - If an NTBA is not pre-configured for EIA, EIA automatically discovers the NTBA device and sends executable information. When endpoint traffic is going through a Sensor that sends flows to NTBA, and if NTBA does not have executable information for that endpoint, NTBA sends a discovery probe to that endpoint. EIA discovers the NTBA and starts to communicate with NTBA. This reduces the administrator's burden to figure out how Sensors, NTBA and endpoints are deployed in the network.
Both the client and the server must have the certificates signed by the common Certification Authority (CA). The common CA can be ePO - On-prem server.
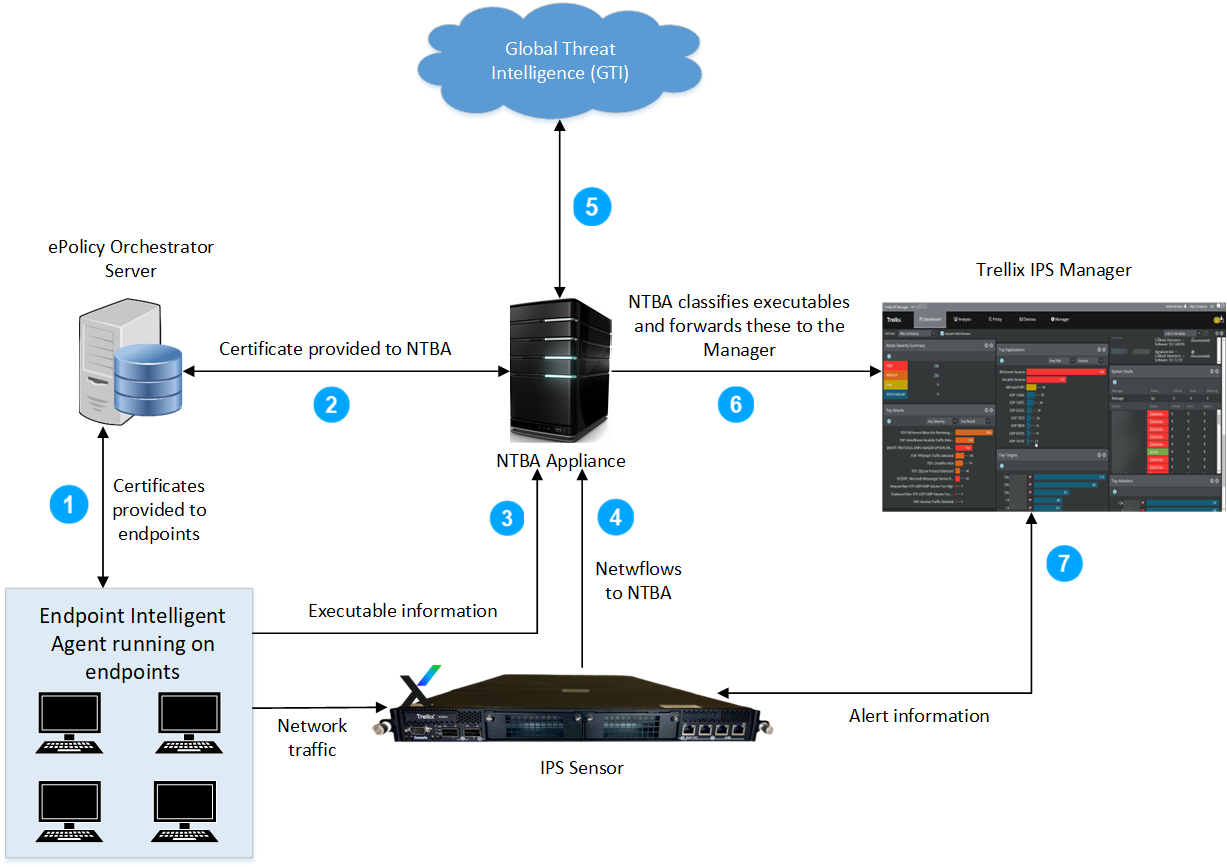
Trellix ePO - On-prem Server: The ePO - On-prem server installs and configures the Trellix Agent and EIA settings on the managed hosts. The server is used to exchange the certificates that will be used to authenticate and secure EIA communication with the NTBA Appliance.
EIA: These are endpoints that have the EIA installed on them. They provide the executable information about all executables to the NTBA Appliance. Based on dynamic analysis, if data files like doc and pdf are malicious, EIA provides file information like malware name and artifacts to NTBA.
NTBA Appliance: The EIA connects to the NTBA Appliance and sends the executable information to the NTBA Appliance. The IPS Sensor/router, if configured, sends NetFlows to the NTBA Appliance. The NTBA Appliance also responds to the Manager queries for monitors/dashboards data and also for endpoint intelligence information for existing NTBA and IPS alerts.
IPS Sensors/Routers: The NetFlow data that come from the IPS Sensor is correlated with the executable information coming from the EIA. For the NTBA Appliance to receive NetFlows, you must configure the IPS Sensor/router as an exporter (optional).
Trellix Global Threat Intelligence: EIA gets the GTI information via the NTBA Appliance and computes the malware confidence for an executable along with its own malware indicators.
Manager: The Manager maintains the allowed and blocked hashes that can be leveraged by all devices configured on the Manager for reporting and blocking purposes. The Manager pushes all the imported hashes to all the available NTBA Appliances and the IPS Sensors.