Attack Definitions are essentially a 'shortcut' to customizing a particular attack's response across all policies containing that attack. Responses configured at the Attack Definitions level are then available for that attack at the attack set profile and policy level.
We've discussed policy inheritance and response actions. To fully understand Attack Definitions, consider a concept that we will loosely call response inheritance.
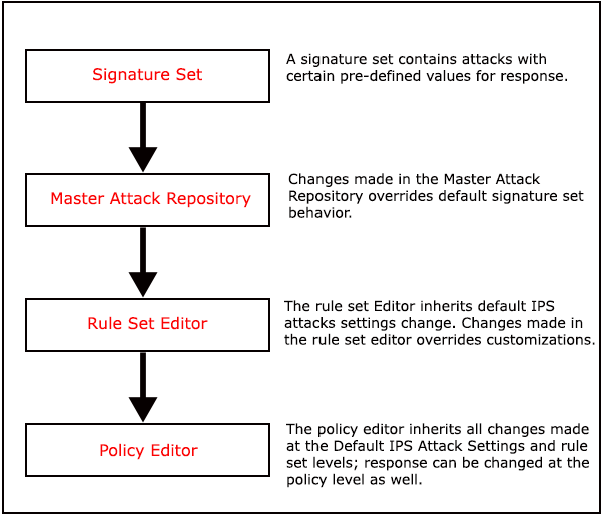
A new signature set straight from the Update Server contains some default actions associated with particular attacks. For example, certain attacks are configured to log packets, and others are configured not to log packets.
When you open an attack in the Attack Definitions editor, Attack Definitions displays the default attack values specified by the signature set. Attack Definitions thus "inherits" the response actions from the signature set. Customizing these values in the Attack Definitions overrides the signature set's values. Regardless of what the signature set suggested as the attack's response, the attack now has a custom response as specified in Attack Definitions.
Attack Definitions values are then available for customization at the attack set profile level. For example, at the attack set profile level, you inherit all the customization from the Attack Definitions level, but can set a response action of "blocking" for certain attacks. Now the attack can have the Attack Definitions customization plus the attack set profile customization.
Finally, you have the Policy level. All the customization made at the attack set profile level or at the Attack Definitions level are inherited at the Policy level.
As shown in the following figure, each level inherits response attribute values from previous level. At each level you can either retain the inherited value for an attack or customize it by explicitly setting or removing a value.
The policy editor now displays labels showing at what level an attack was customized:
D – Default Trellix IPS-supplied
D – Master Attack Repository
R – Attack set profile Editor (only blocking action)
P – IPS Policy Editor
For example, suppose you want to create 3 policies that detect the attack "FTP: Attack Example," which happens to be a Recommended For Blocking (RFSB) attack.
Your requirements are as follows:
Policy1: block FTP: Attack Example and log packets
Policy2: do not block FTP: Attack Example; log packets.
Policy3: block FTP: Attack Example; do not log packets
For all three policies, you want to be notified by email if FTP: Attack Example is discovered.
How to accomplish this?
At the Master Attack Repository level for FTP: Attack Example, configure packet logging and email notification.
At the attack set profile level, enable blocking for RFSB attacks.
At the PS Policies level, create your three policies. When you choose FTP: Attack Example for Policy2, disable blocking. For Policy3, disable packet logging.
Note
Master Attack Repository customization can be imported/exported using the Policy Import/Export feature.