Detection of bot Command and Control server (C&C server) activity along with the callback traffic is a key feature of the advanced botnet detection(advanced callback detection). Trellix IPS monitors networks for bot callback activities and protects the network by updating the reputation of the newly identified C&C servers in the Update Server.
The C&C server that communicates with the infected endpoint directs instructions to the malware, which then sends back information and gets instructions in the form of callback traffic. Blocking the callback activity prevents communication between the C&C servers and the malware. The following detection and blocking mechanisms for callback activity are provided by Trellix IPS:
Multiple signatures are provided in the Default Prevention policy for detecting the callback activity.
Heuristic detection capabilities that correlate individual bot (callback) behaviors across flows, detecting complex patterns of behavior.
Trellix provides bot (callback) intelligence that includes a bot Command and Control database consisting of known Command and Control URLs, server domain names, and IP addresses. The Manager pulls this information from the cloud in the form of callback detectors, and downloads to the Sensors a series of indicators of compromise to detect callback activities. The Manager also periodically queries the cloud servers for DAT file updates to the callback detectors.
How callback detectors work?
The callback detectors are generated by Trellix. The callback detectors contain information regarding the IP addresses, domains, and URLs of the malicious bot Command and Control servers. Each of these is categorized based on at least one or more relevant callback IDs (botnet IDs). The callback detectors also contain the relevant ports and protocols that are monitored by Trellix IPS.
For enhanced callback detection (botnet detection), download the latest callback detectors or schedule automatic download and deployment of the callback detectors. The Manager downloads the callback detectors and pushes them to the Sensor. The bot C&C server communicates in the form of callback activities that are detected by the Sensor using the information in the callback detectors. The Sensor inspects all traffic against the malicious IP addresses and port numbers, domains and URLs in the callback detectors and triggers alerts based on them. The Sensor sends an alert to the Manager indicating the callback ID detected along with the Layer 7 information (if Layer 7 data collection is configured). The Manager uses the callback-ID information in the alert to associate the information present in the callback detector. This information can be drilled down and viewed in the Dashboard and Attack Log of the Manager.
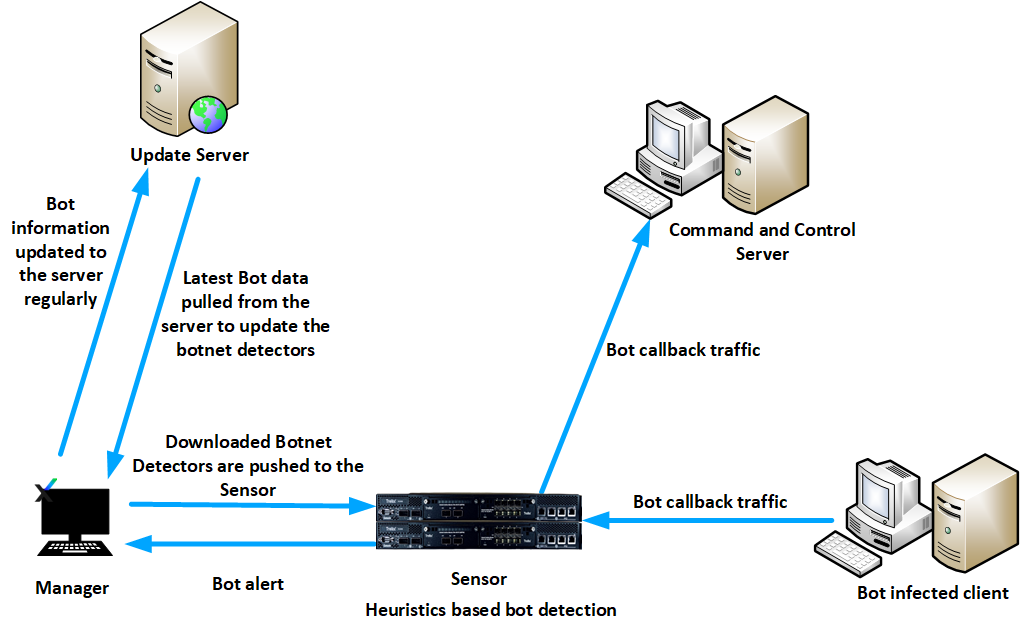
Trellix IPS allows you to analyze bots using the Top Callback Activity dashboard. The dashboard allows you to drill down into each piece of detected bot callback activity. The Callback Activity page provides you with more details of the detected bot activity.
The Manager provides both automatic and manual import of the callback detectors.