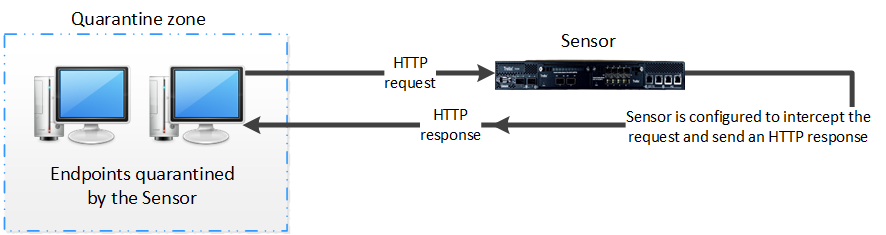
When a user attempts to browse to a location outside the Quarantine Zone, the Sensor can be configured to intercept the HTTP request and respond with a browser message explaining the reason for quarantine and its duration. Consider the illustration presented.
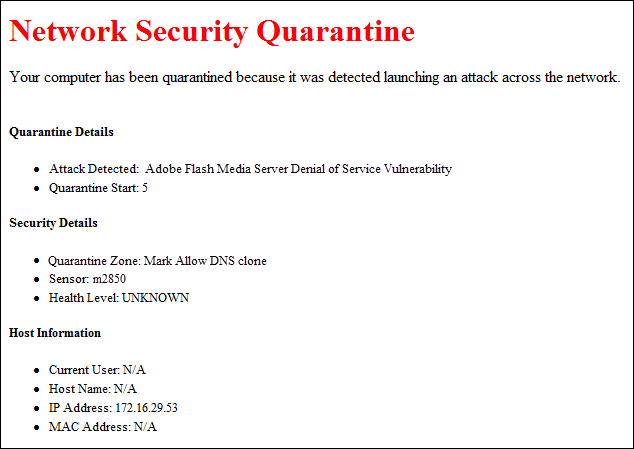
Marco's endpoint was quarantined by the Sensor when the Sensor detected the endpoint launching an attack. Now, when he attempts to browse to a business critical finance portal which lies outside the designated Quarantine Zone, he receives a notification from the browser stating that his endpoint has been quarantined. What actually happened here was the administrator of Marco's network had configured the Sensor to:
Quarantine an endpoint if it attempted to launch an attack.
Respond with a browser message which stated the reason for quarantine if the quarantined endpoint user attempted to access a URL outside the Quarantine Zone.
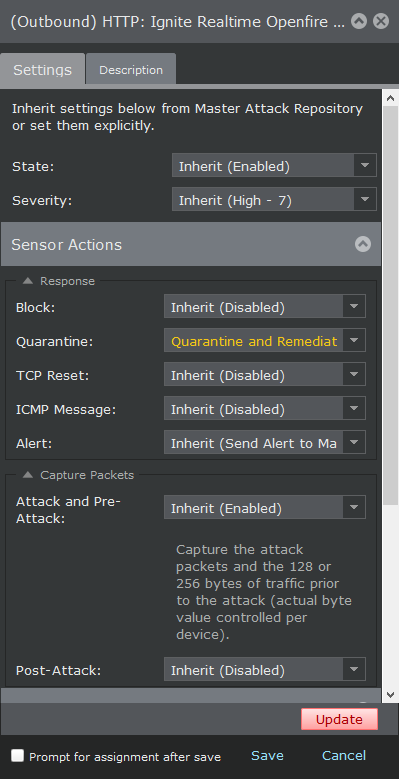
Marco's administrator had firstly enabled quarantine for all the hosts which are generating a specific attack by quarantining the attacker IP. The next thing the administrator did to ensure every quarantined endpoint that generated this attack receives an HTTP response was to select the Quarantine and Remediate Attacker option in Quarantine drop-down in the Attack Definitions page for the policy.
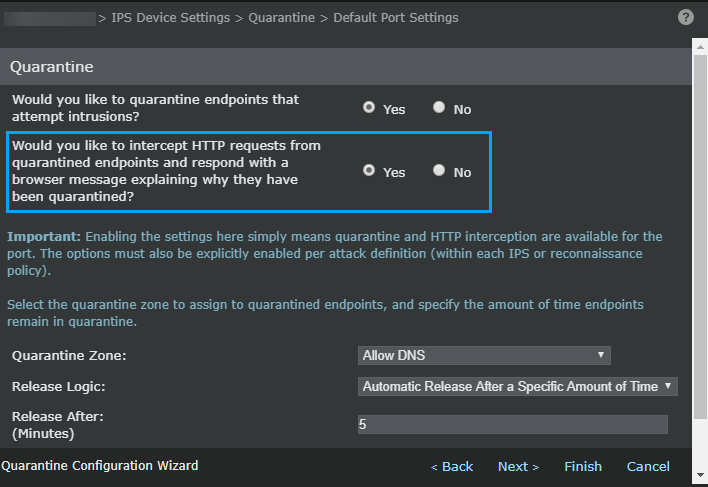
The administrator had then configured the Sensor in the Default Port Settings page in the Manager. In order to quarantine any violating endpoints, the administrator enables Would you like to quarantine endpoints that attempt intrusions?. And once an endpoint has been quarantined, in order to respond with a browser message, the administrator enables Would you like to intercept HTTP requests from quarantined endpoints and respond with a browser message explaining why they have been quarantined?.
Similar configurations of this feature can be done from the following locations in the Manager: