Trellix IPS supports capturing data packets on ingress traffic in your network. When captured, these data packets can be used to perform forensics analysis that help in identifying network security threats. Analysis of the captured data packets can help you monitor whether the data communication and network usage of your production environment complies with the outlined policies of your organization. The captured data packets can also be used for troubleshooting Sensor issues. Data packets can be captured in the port mode or file mode.
In the port mode, you can configure a port of your Sensor to capture data packets. The captured packets are forwarded to an external device (for example, a Sniffer) via a monitoring port configured in span mode.
When a port is designated for capturing packets, it cannot be used for IPS inspection. Note that the packet copy between the Sensor and the external device must happen over a direct link between these two devices, that is, without a switch in between.
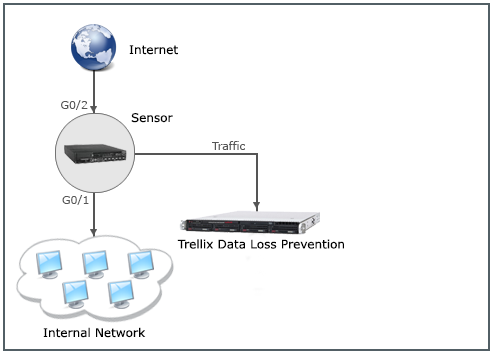
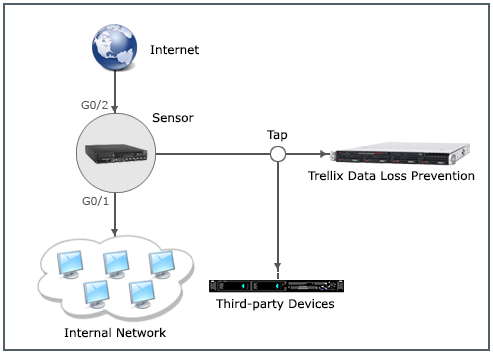
The packet capture in Trellix IPS can also be used to forward selected traffic to Trellix Data Loss Prevention and/or third-party devices.
In the file mode, the captured files are sent to the Manager or an SCP server. The maximum file size can be configured to the maximum value of Sensor-defined limits. The SCP server should be running and reachable from the Sensor. The Sensor can store only one captured file. If you have not uploaded the file and start the capture session again, the file will be overwritten. Once the packet capturing session is complete the Sensor uploads the file to the Manager. If the Sensor reboots while packet capturing is in progress, then you need to upload the file again.
Note
Packet capturing from the Manager is supported on NS-Series and Virtual IPS Sensors. In case of a failover setup, each Sensor captures data packets separately.
The packet capture configurations are done using packet capture rules which are applied to a Sensor. You can define packet capture rule templates, which allow you to apply the same capture rules across multiple devices. With templates, you define capture rules at the device level and then insert them into the configuration of as many Sensors as required.
Packet capture might not occur when:
The Sensor is in layer 2.
Scanning Exceptions is enabled on the Sensor.
When tunneling is disabled, the Sensor can capture tunneled traffic only when the Capture Rule for Protocol is set to All. Any other rule will not capture tunneled traffic.
Note
From the Manager, capturing of jumbo packet frames is not supported in port mode. In the file mode, jumbo packet frames are truncated to a maximum size 1526 bytes or the configured snap length.
When the application protocol filter rules are configured and the Sensor receives fragmented traffic matching these filter rules, the Sensor captures only the first fragmented packet of the flow and not the subsequent ones. This is because the port information is present in the first fragment alone.
Trellix recommends that you ensure that the capture traffic volume is less than the capacity of the configured capture port of the Sensor. Otherwise, this can affect the Sensor performance.