Central Manager is a centralized system managing multiple Managers. The Central Manager architecture consists of a Central Manager, which is interconnected to various Managers.
Central Manager manages configurations and pushes them globally to Managers. Configurations are pushed to the Sensors indirectly through Managers.
Suppose you are responsible for managing global security operations at a large multi-national corporation and you wish to delegate the management of specific security functions (including IPS) to the company's regional facilities. Your goal therefore, is to establish a master IPS security policy at the headquarters that can be pushed down to each region.
In this scenario, you can use the Central Manager at the headquarters and deploy a dedicated Manager for each region. When you use the Central Manager, your regional Managers can add their own region-specific rules, but cannot modify any configuration established by the Central Manager. Each Manager handles the daily operations and event management of the Sensors. The following diagram shows the Central Manager setup.
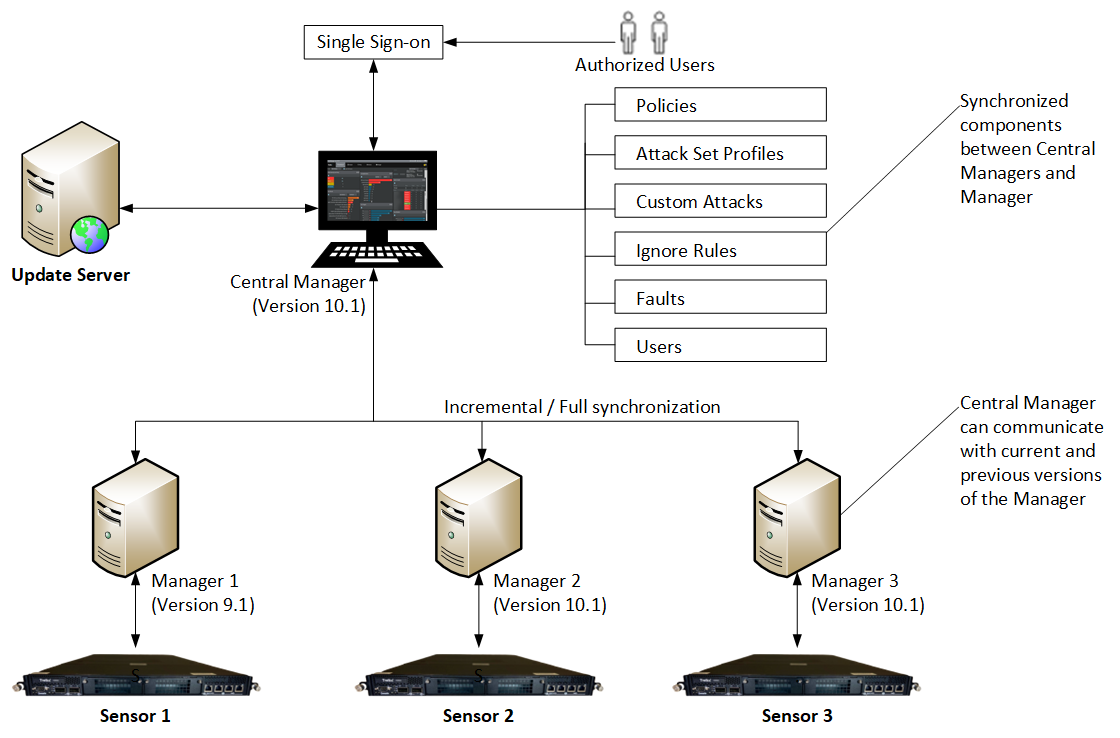
The Central Manager's single sign-on mechanism manages the authentication of global users across Managers. The objective is to allow global users to access all Managers using a single sign-on. Once a global user is authenticated with the Central Manager, the user can access a Manager without having to re-enter the login credentials for the Manager.
The Central Manager supports heterogeneous Managers. It means that the Central Manager can communicate with the current version of Manager as well as the previous versions of the Manager.
Note
Central Manager cannot directly handle any Manager resources. A Central Manager user has to log onto the Manager to do the same.
You cannot add Sensors to the Central Manger.
You cannot create admin domains in the Central Manager.