The first step to using a CIDR interface is to change the interface type from Dedicated to CIDR.
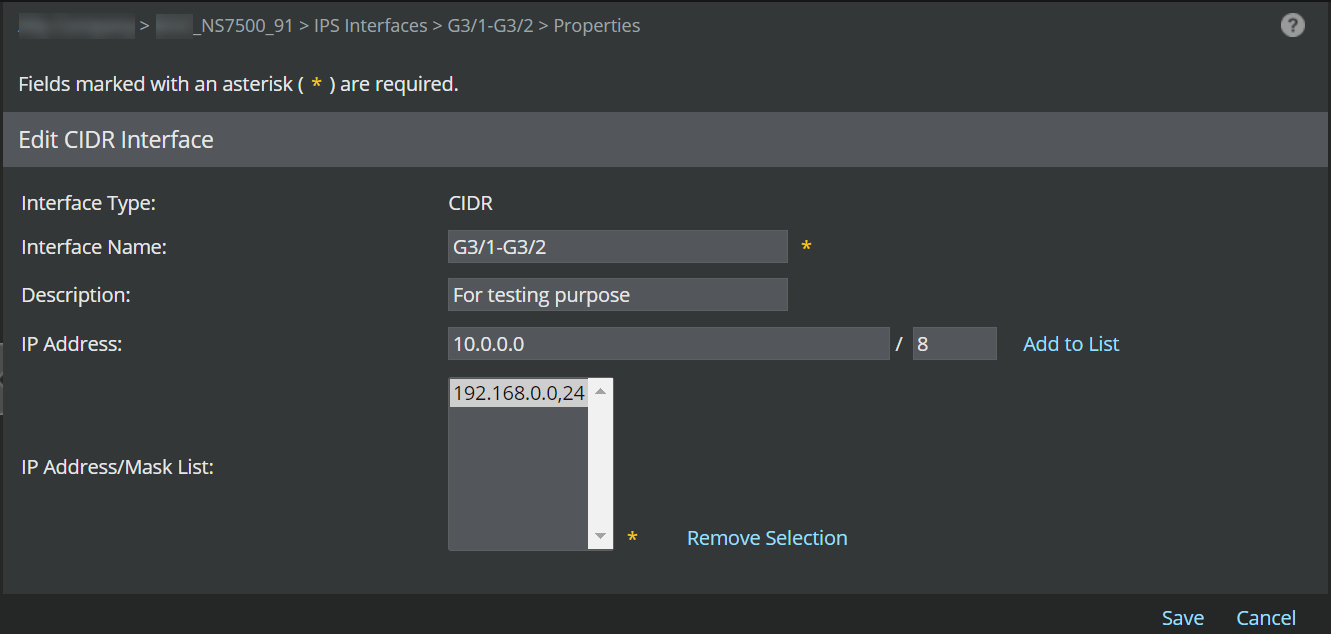
The next step is to edit the interface and associate CIDR ranges with it. You'll want to define here all the internal CIDR ranges whose traffic you anticipate traversing this interface.
The user interface expects CIDR ranges as a combination of IP network (or address) and mask length (in bits). In the figure below, the 192.168.0.0/24 network has already been added to the list and the 10.0.0.0/8 network is about to be added.
The figure below shows the results of the last step:
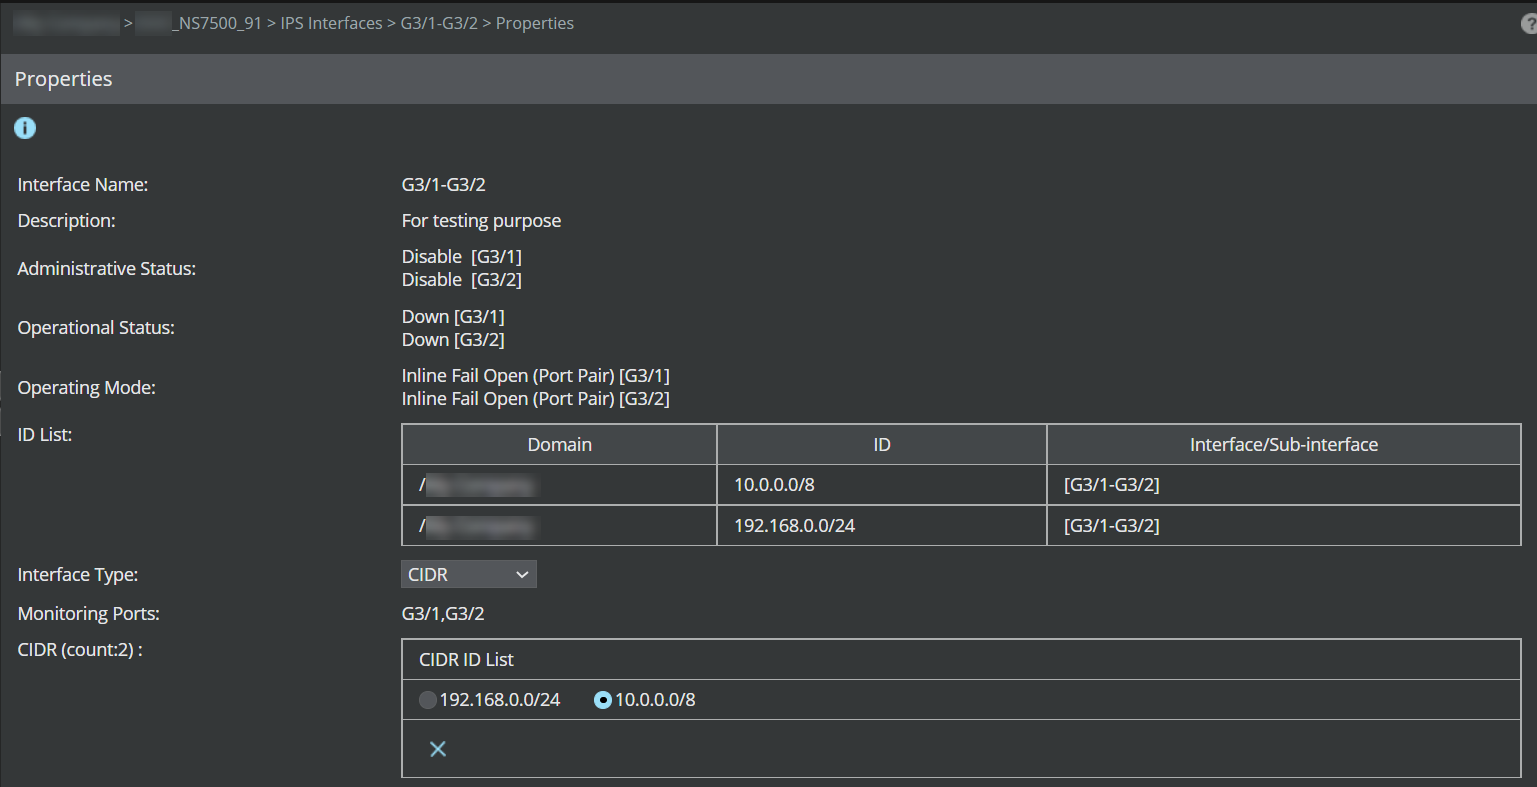
If we look at the Devices → <Admin Domain Name> → Devices → <Device Name> → IPS Interfaces → <Interface_Name> → Properties, the interfaces and their corresponding policies, the CIDR interface will appear no different than the Dedicated interface it replaced.
However, if we look back at the details of interface G3/1-G3/2, we can confirm at a glance that it is now associated with CIDR ranges 192.168.0.0/24 or 10.0.0.0/8.
If traffic flows through interface G3/1-G3/2, with no source address on the 192.168.0.0/24 or 10.0.0.0/8 networks, the Default Prevention policy will no longer be applied. Instead, the traffic applied will be that of the parent (physical interface) and not the Sensor policies.