Lightweight Directory Access Protocol (LDAP) is a set of protocols for accessing information directories. LDAP runs on top of TCP/IP, which is necessary for any type of Internet access. LDAP is used to look up encryption certificates, pointers to printers and other services on a network, and provide a single sign-on across many services.
LDAP is appropriate for any kind of directory-like information, where fast lookups and less-frequent updates are the standard.
Using Manager, you can configure a LDAP server at the Manager level. You can configure a maximum of 4 LDAP servers onto Manager. If the first LDAP server is not available for communication due to a network failure, Manager will try to communicate with the second or the third server. If authentication fails at any available servers, the Manager will not communicate with the other available servers.
The LDAP action enables you to use LDAP to authenticate existing users on their LDAP server.
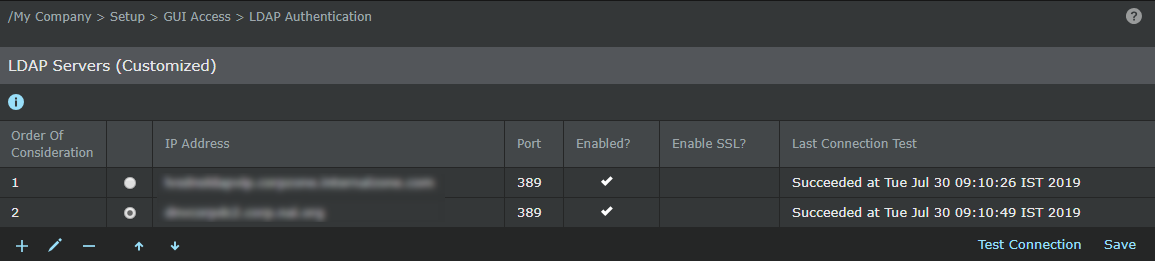
You can configure the LDAP server in the Manager/Central Manager from Manager → <Admin Domain Name> → Setup → GUI Access → LDAP Authentication.
Note
If LDAP servers are configured with Central Manager, and the LDAP servers exist in private networks and Managers exist in public network, the LDAP configuration needs to be customized at the Manager in a way that it reaches the LDAP server through the translated public IP address.