Remote Authentication Dial In User Service (RADIUS) is an AAA (authentication, authorization and accounting) protocol for applications such as network access.
While connecting to the internet using a modem, you are required to enter a username and password. The information is passed through a Network Access Device (NAD) device, and then to a RADIUS server over the RADIUS protocol. The RADIUS server checks if the information is correct using authentication schemes like PAP, CHAP, and EAP-MD5. If accepted, the server will authorize the access.
Using Manager, you can configure a RADIUS server at the Manager level. You can configure a maximum of 4 RADIUS servers onto Manager. If the first RADIUS server is not available for communication, due to a network failure, Manager will try to communicate with the second or the third server. If authentication fails at any available servers, then Manager will not communicate with the other available servers.
The RADIUS action enables you to use RADIUS to authenticate existing users on their RADIUS server. Trellix IPS supports the PAP, CHAP, and EAP-MD5 schemes of RADIUS authentication.
Note
When EAP-MD5 scheme is selected, the Manager internally authenticates requests that use MS-CHAPv2.
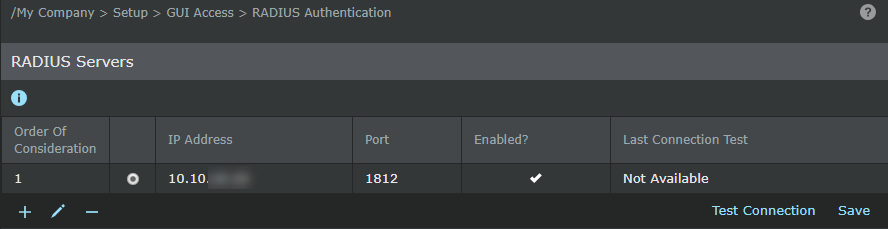
You can configure the RADIUS authentication in the Manager from Manager → <Admin Domain Name> → Setup → GUI Access → RADIUS Authentication.
Note
For the Central Manager, you can configure RADIUS authentication from Manager → Setup → GUI Access → RADIUS Authentication.