Advanced Traffic Inspection is disabled by default and inspects traffic per VIDS. You can enable it in the Policy Manager page of an interface or subinterface.
Click the Policy tab.
From the Domain drop-down list, select the domain you want to inspect traffic for.
Navigate to Intrusion Prevention → Policy Manager.
On the Interface tab, double-click the interface to enable the advanced traffic inspection.
The <Device Name/Interface> panel opens.
In the Inspection Options section, select the policy from the Policy drop down list.
To create a new policy, click the
 icon or double-click on the policy to edit an already assigned policy.
If you are creating a new policy proceed to step 6. If you are editing an existing policy proceed to step 7.
The Properties page opens. Enter the Name and Description. Select the Visibility and click Next.
The Inspection Options page opens.
Configure Advanced Traffic Inspection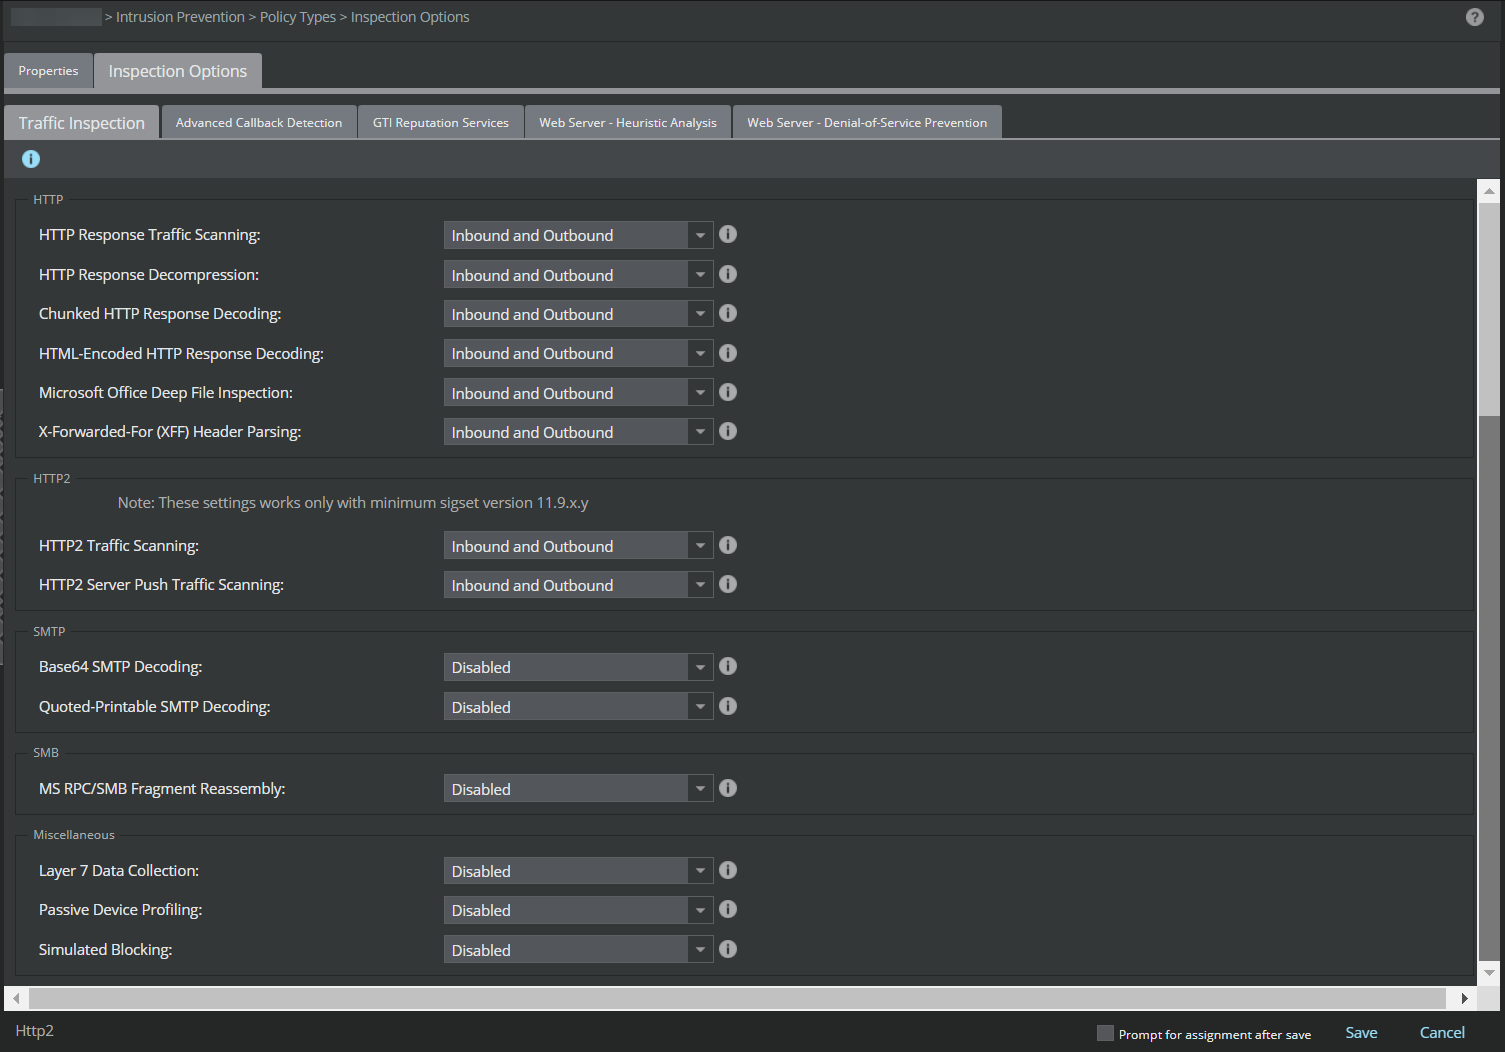
In the Traffic Inspection tab, under HTTP, enable HTTP Response Traffic Scanning in the required direction to enable Chunked HTTP Response Decoding, HTML-Encoded HTTP Response Decoding, HTTP2 Traffic Scanning and HTTP2 Server Push Traffic Scanning.
Under SMTP, enable Base64 SMTP Decoding and Quoted-Printable SMTP Decoding in the required direction.
Under SMB, enable MS RPC/SMB Fragment Reassembly in the required direction.
Note
The options that explicitly mention HTTP response traffic require HTTP Response Scanning to be enabled in that same direction. These options are disabled if the HTTP response traffic is disabled.
Option
Definition
Chunked HTTP Response Decoding
Chunked transfer encoding is a data transfer mechanism of HTTP. The web server breaks the HTTP response content into chunks. Chunked transfer encoding uses the HTTP response header in place of the content-length header, which the protocol would otherwise require.
Chunked transfer encoding supports sending dynamically generated content to clients without having to buffer it. Such payload chunks can evade network inspection devices.
HTML-Encoded HTTP Response Decoding
HTTP response traffic can be sent using HTML encoding, and attackers can use this encoding mechanism to evade detection of malicious payload. Enable this for the Sensor to decode such traffic for inspection. Some of the encoding techniques used are:
Deflate — This compression technique is used mainly to compress data in PDF file formats. PDF documents support using “deflate” encoding in parts of the document.
HTML encoding — The HTML response data is encoded using the "&#" encoding technique. The encoding can be in decimal or hexadecimal format.
Base64 — Base64 encoding is used to encode binary data that is to be stored and transferred over media that are designed to deal with textual data. This encoding technique ensures that the data remains intact without modification during transport.
Base64 SMTP Decoding
Select to inspect Base64 encoded traffic over SMTP.
Quoted-Printable SMTP Decoding
The SMTP protocol specification uses MIME content transfer encoding to transport binary data. Since SMTP protocol can handle only 7-bit ASCII data, each 3-byte group of binary data is converted to 6-bit number and replaced with an ASCII character.
Quoted-printable and Base64 are the two basic MIME content transfer encodings. Quoted-printable encoding uses printable ASCII characters, such as alphanumeric and the equals sign (=), to transmit 8-bit data over a 7-bit data path.
Quoted-printable encoding technique maps arbitrary bytes into sequences of ASCII characters.
MS RPC/SMB Fragment Reassembly
SMB is a network file sharing protocol. MS-RPC provides a framework for interprocess communication mechanism to exchange data between two processes residing on the same machine or on two remote machines accessible over a network. MS-RPC's transport layer could be TCP, UDP, HTTP, or SMB. SMB protocol supports segmentation of its data. Also, MS-RPC protocol supports fragmentation of its payload. Since MS-RPC can be carried within SMB protocol data, either fragmentation or segmentation or a combination of both can be used to evade any network packet inspection device.
Save
Saves your configuration in the Manager database
Click Save in the Inspection Options page.
To save the configuration changes, click Save in the <Device Name/Interface> panel.
Perform a configuration update for the Sensor.