Prerequisite: Make sure the Sensors for which you want to configure alert suppression are active and reachable to the Manager.
You can set a suppression limit for multiple occurrences of a singular attack for a specific source-destination IP address pair that is detected within a limited time frame, as well as set up packet logging for the attacks — this is known as Exploit throttling. Exploit throttling limits the number of duplicate alerts that are sent to Manager from a Sensor. Throttling is very effective against repetitive Exploit attacks where a source IP address is spoofed and generates a high number of alerts. In addition, the Sensor saves the alerts and packet logs in first-in first-out (FIFO) buffers in the event it loses communication with Manager, as well as when a Sensor generates alerts faster than it can send to Manager. The Attack Log, in its details, displays this type of alert as Exploit with an Attack Count of 2 or higher.
Note
Alert suppression is unavailable for anomaly-based buffer overflow and shellcode attacks.
In Trellix IPS, an exploit throttle alert is the grouping of multiple instances of the same attack (by Alert ID) from a single source to a single destination detected by the same VIPS (interface or subinterface — if an interface has been segmented into subinterfaces, the interface is no longer the VIPS; the subinterface is). Thus, the equation is: AlertID + VIPS + Source IP + Destination IP + Count = Exploit throttle attack
The Generate unique suppression summary alerts for up to [ X ] attack, attacker and target combinations field determines the number of unique Exploit throttle instances to maintain at a given time. For example, if you enter the number 10, then 10 unique Exploit throttle instances can be tracked at a given time. Once 10 is reached, all other cases are kept in a single "wildcard" instance; thus, other unique combinations that occur outside of the 10 uniquely maintained instances are maintained as one instance, and source and destination IP addresses do not appear in the Exploit throttle summary since multiple addresses may be involved. This is due to Sensor memory limits. A throttle entry is removed after the time limit (The alert suppression window is [ X ] seconds) has expired.
The Generate standard alerts for the first [ X ] attack(s) seen during the alert suppression window identifies the minimum number of alerts that must be detected for a unique suppression instance to be classified as an exploit throttle attack. This number means you accept a specific number (x) of the same attack. Thus, if you detect x-1 by the expiration of the interval (The alert suppression window is [ X ] seconds field), alerts are sent for each separate occurrence and there is no exploit throttle. If there are x+1, the first x attacks are sent as individual alerts and the attacks exceeding this count are throttled into one alert that summarizes this persistent attack. By sending a few of the throttled alerts as individuals allows you to view details and packet log information for the first few instances of an attack.
The The alert suppression window is [ X ] seconds field is the time span in which you accumulate instances of the same attack. This value acts as a timer; when the timer expires, the current instance is cleared to make room for a new suppression instance.
The Correlate signatures for a single attack for [ X ] seconds field notes the amount of time that the Sensor will correlate the signatures used to detect a suppressed attack instance. Many attacks have multiple signatures; thus, the suppression is valid as long as any signature for a suppressed attack has detected a single attack instance. Correlation sends the signature with the lowest Benign Trigger Probability in the suppressed alert record.
Complete the following tasks to enable alert throttling.
Click the Devices tab.
Select the domain from the Domain drop-down list.
In the left pane, click the Devices tab.
Select the device from the Device drop-down list.
Select Setup → Advanced → Alerting Options.
IPS Alerting page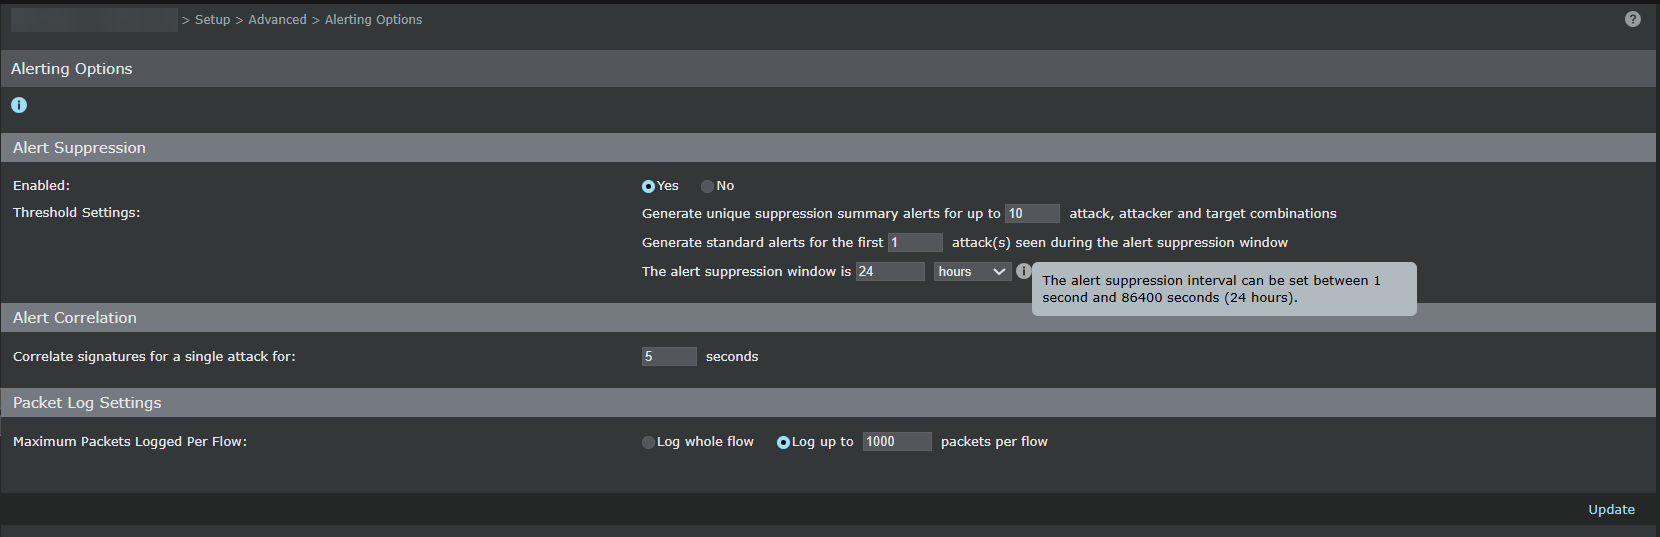
Select Yes for Enabled under Alert Suppression to turn on alert suppression.
Note
Select No and click Update at any time to disable alert suppression.
Type a value within Generate unique suppression summary alerts for up to [ X ] attack, attacker and target combinations.
This is the number of unique instances that will maintain counts during the time limit. All other suppression groupings are recorded in a single wildcard instance. The default is 10 instances.
Type a value within the Generate standard alerts for the first [ X ] attack(s) seen during the alert suppression window.
This number signifies the number of individual alerts for a unique suppression instance that you want to be sent before collecting all of the alerts into one throttle instance. The default is 1 alert. By sending individual alerts before the throttle preserves the ability to generate packet logs for each alert rather than one log for the entire throttle.
Type a value within The alert suppression window is [ X ] seconds. You can configure this value in seconds, minutes, or hours.
Note
Until the 11.1 Update 10 release, the default value was 120 seconds. Starting with the 11.1 Update 10 release, the default value is 24 hours. This enhancement is not supported for NS7100, NS7200, NS7300, NS9100, NS9200, and NS9300 Sensors.
The upgrade to 11.1 Update 10 automatically sets the alert suppression interval to its new maximum of 24 hours, regardless of any previous configuration. This setting remains customizable.
Type a value within Correlate signatures for a single attack for field under Alert Correlation.
The default is 5 seconds. The Generate unique suppression summary alerts for up to [ X ] attack, attacker and target combinations is active for this time limit.
Select a Maximum Packets Logged Per Flow under Packet Log Settings.
Either of the two choices will also contain the 128 bytes previous to the attack. You can do one of the following:
Log Whole Flow — Logs entire flow from start to finish of transmission.
Log up tonpackets per flow — Type the number of packets (from 1000 to 64000) to log within a flow. The logged packets begin with the attack packets. Default is 1000 packets.
Note
Even if you select Log Whole Flow, the Sensor may not be able to continue logging if it fails.
Click Update.
The alerts for exceeding this threshold are called throttle alerts. You will see this in the Alert Details panel of Attack Log.
Deploy configuration changes to the Sensor.