You can filter the rule for capturing packets and apply it as a packet capture profile.
For a standalone Sensor, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Troubleshooting → Packet Capturing → Capture Now.
For Sensors in a stack, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Member Sensors → <Stackname-node id> → Troubleshooting → Packet Capturing → Capture Now.
For member Sensors in a cluster, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Member Sensors → <MemberSensorname-node id> → Troubleshooting → Packet Capturing → Capture Now.
Under Capture Rules, the following list of capture rules is displayed.
Option
Definitions
Monitoring port
The monitoring ports on which the rule is applied: The options are:
All and <Interface depending on the Sensors>.
Note
Some options may not be displayed, depending on the configured Sensor model.
Traffic
The traffic for which the capture rule is to be filtered. The options are: ALL, ARP and IP.
Protocol
Type of protocols to be filtered. The options are:
TCP, UDP, ICMP, and Protocol Number.
IP Version
Type of IP Setting (IPv4)
Fragments Only?
Captures only the fragmented traffic. By default this option is disabled.
Source IP
Source IP address of the packet
Source Mask
Source IP mask
Source Port
Source port number of the packet. This option will be enabled only if you select the protocol type as TCP or UDP.
Destination IP
Destination IP address of the packet
Destination Mask
Destination IP mask
Destination Port
Destination port number of the packet. This option will be enabled only if you select the protocol type as TCP or UDP
Vlan ID
VLAN ID of the packet to be captured. This option will be disabled if you select the protocol type as ALL or ARP.
Note
Only the outer VLAN ID will be inspected in case of double VLAN tagged traffic
Protocol Number
The protocol number. This can be specified only if the option Protocol Number is selected under Protocol.
When a packet capture session is in progress, you cannot configure/push a new packet capture profile. To apply a new profile, the packet capture session needs to be stopped.
You can add/remove the rows by clicking - or + signs on the right-hand side of the Capture Rules field.
The Capture Rule Template can be defined at the admin level to be applied across multiple Sensors or at a Sensor level.
To create a packet capture rule template at an admin-domain level, select Policy → <Admin Domain Name> → Intrusion Prevention → Objects → Packet Capture Rule Templates → New.
To create a packet capture rule template at a standalone Sensor level, select Devices → <Admin Domain Name> → Devices → <Device Name> → Troubleshooting → Packet Capturing → Capture Now → Insert Capture Rule Template → New.
To create a packet capture rule template at a Sensor in a stack, select Devices → <Admin Domain Name> → Devices → <Device Name> → Member Sensors → <Stackname-node id> → Troubleshooting → Packet Capturing → Capture Now → Insert Capture Rule Template → New.
The Add a Capture Rule Template page opens.
Add a Capture Rule Template window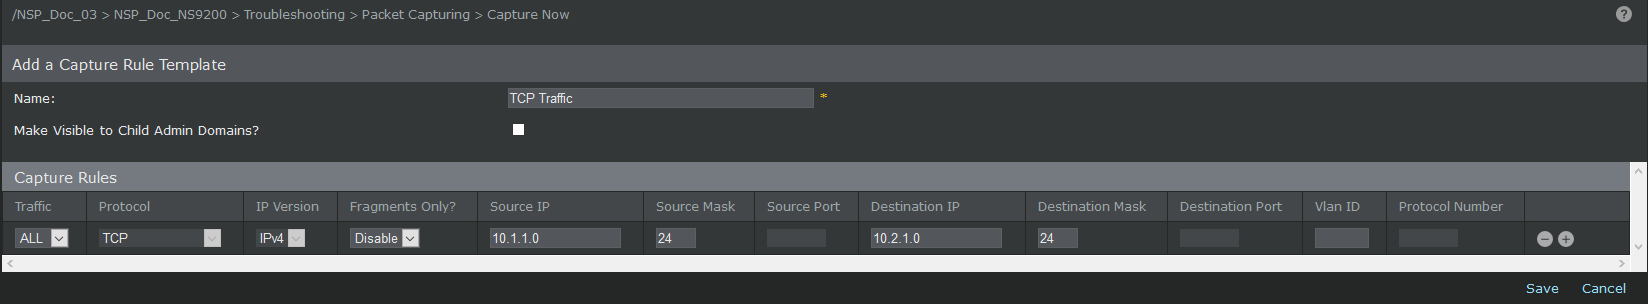
Type the Name of the capture rule.
Select the Make Visible to Child Admin Domains? option to make the rule visible to the child admin domain.
Click Save to save the capture rule.
The capture rules can be modified. Once a rule is modified, click Save.
To delete a capture rule, click
 against the rule. Click Save.
Note
A modification of the template rule does not affect the rule of the Sensor on which it has been applied.