You can create auto-acknowledgment rules based on the name, source endpoint, and target endpoint of attacks. You can also define the time period for which the rule could be applicable. The Manager auto-acknowledges those alerts, which match the active rules. The list of auto-acknowledgement rules can be exported.
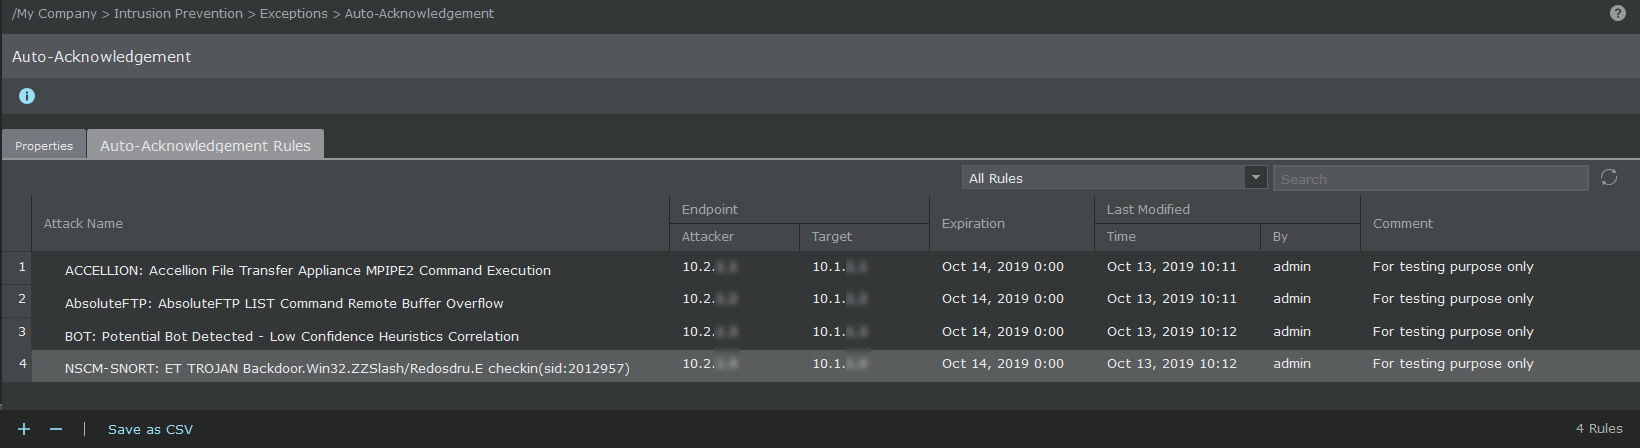
Use the drop-down on top to filter rules based on the expiration dates. All Rules is selected by default. All expired rules are prefixed with the warning symbol which helps differentiate between the active rules and the expired rules. You can use the Search field to search for a specific rule. You can also sort the column in ascending or descending order. To hide any column, hover over a column, click the drop-down arrow, and select the columns you want to hide.
Navigate to Policy → Intrusion Prevention → Exceptions → Auto-Acknowledgement → Auto-acknowledgement Rules.
Perform one of the following actions to manage the auto-acknowledgement rules:
To create a rule, click the
 icon
To edit a rule, select the rule you want to edit.
The Rule Details panel opens on the right side.
Enter/modify the details for the following fields:
Option
Definition
Attack Name
Enter the name of the attack or select the attack from the list displayed.
Note
As you type the name of the attack, a list of attacks are displayed.
Attacker Endpoint
Enter the IP address of the endpoint from where the attack is generated.
Target Endpoint
Enter the IP address of the endpoint to which the attack is targeted.
Expiration
Select the expiration date and time for the rule.
Modified
Shows the last modified user, date, and time at which the rule was modified.
Comment
Optionally enter additional comments.
Note
Either the attack name or any one endpoint has to be mentioned while creating a new rule.
Click Save to save the rule.
Click the
 icon to close the Rule Details panel.
To delete an acknowledgement rule, select the rule you want to delete and click the
 icon.
Note
You can select multiple rules and delete.
To export the auto-acknowledgement rules, click Save as CSV. The list of auto-acknowledgement rules available are exported as a .csv file.
You can also create an auto-acknowledgement rule from the Attack Log page. For more information, see Attack Log.