By default, the Heuristic Web Application Server Protection feature is disabled. For it to work, you must specify your options, which are Website Paths to Protect and Blocked Text. Then, you must enable the feature for an interface or subinterface. You can specify your options at the admin-domain level and inherit it at the interface and subinterface levels. If required, you can specify different options for an interface or subinterface.
Notes:
At a child admin domain, interface, and subinterface levels, you cannot modify the configuration that you inherited from an admin domain. So, you must modify the configuration at the parent admin domain. However, modifying the parent domain affects all the child admin domains, interfaces, and subinterfaces that inherit these settings.
When you create an interface, Heuristic Web Application Server Protection feature is disabled by default. It is also disabled when you create a subinterface regardless of whether it is enabled at the corresponding interface.
In case of subinterfaces, you can only inherit from the admin domain to which they belong.
In the Manager, click the Policy and select the required domain.
Select Intrusion Prevention → Policy Manager.
On the Interfaces tab, double-click the interface to which you would like to configure the heuristic web application.
The <Device Name/Interface> panel opens.
In the Inspection Options section, click the
 icon to create a new policy, or double click the policy to edit the assigned policy.
Proceed to step 5 if a new policy has to be created, or if you wish you edit an existing policy proceed to step 7.
The Properties page opens. Following are the options on the Properties tab:
Option
Definition
Name
Name of the policy
Note
The name field should not be left blank and no special character should be entered while typing the name.
Description
Description for the policy for other users to identify its purpose
Owner
Displays the admin domain to which the policy belongs
Visibility
When selected, makes the policy available to the corresponding child admin domains. However, the policy cannot be edited or deleted from the child admin domains.
From the drop-down list, select the option for the visibility level of the rule object.
Available options are Owner and Child Domains and Owner Domain Only.
Editable here
The status Yes indicates that the policy is owned by the current admin domain.
Statistics
Last Updated
Displays the time stamp when the policy was last modified
Last Updated By
Displays the user who last modified the policy
Assignments
Indicates the number of ports to which the policy is assigned
Click Next.
The Inspection Options page opens.
Select the Web Server - Heuristic Analysis tab.
Specify the required settings in the corresponding fields.
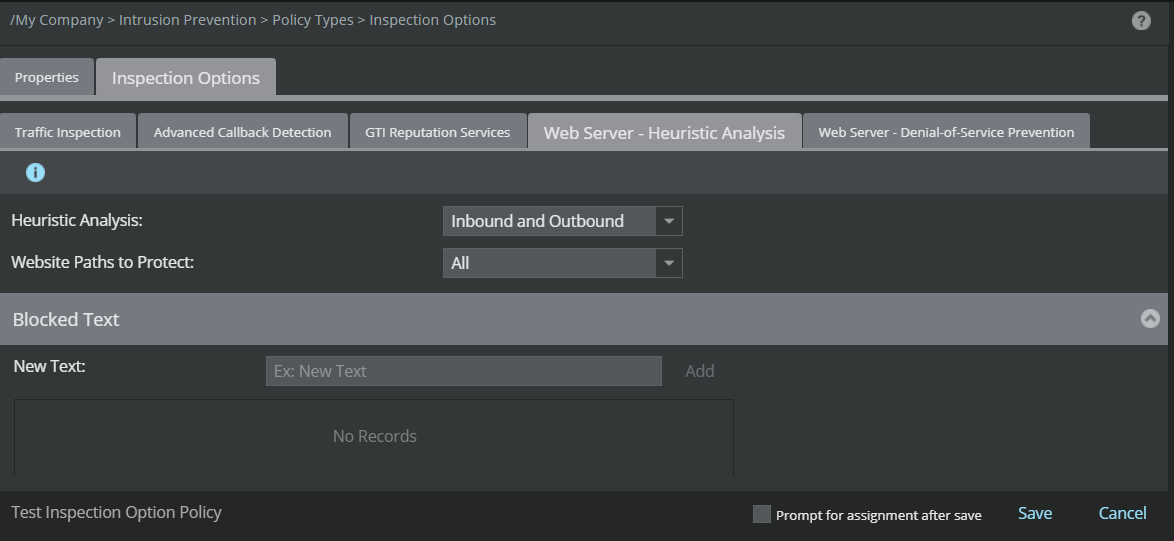
Option
Definition
Heuristic Analysis
Select the direction to which you would like to assign the policy from the drop-down list. Rest of the configuration depends on this selection.
If you have selected Inbound/Outbound/Inbound and Outbound, specify the options for Website Paths to Protect as described below.
All: Select to inherit only the blocked text. The Sensor applies the built-in heuristic rules and the inherited blocked tokens on all the HTTP requests seen at this interface or subinterface.
Specific: Select to inherit the website paths and the blocked text.
Note
You cannot inherit just the website paths from the admin domain.
For the Sensor to consider any HTTP request for Heuristic Web Application Protection, select All for Website Paths to Protect.
To specify website paths, select Specific for Website Paths to Protect and then enter the path in New Website Path and click Add. For example, if you specify /private-banking/ as a path, then the Sensor considers only those requests that contain /private-banking/ for Heuristic Web Application Protection. You can specify up to 512 such paths per Sensor. If you do not specify a path, the Sensor checks all the HTTP requests.
Note
To delete an existing path, hover over it and click the "x" icon.
To specify blocked text, enter the text in New Text and click Add. The added text are listed in the box below. Their type is always custom. Note the following:
These texts must be between 3 and 255 characters in length.
You can specify up to 256 texts per Sensor.
If the Sensor detects any of these texts in a query to the protected website paths, it treats it as an attack. If you define these texts, the Sensor checks the queries for both these texts as well as the built-in, default heuristic rules. If not, it checks only for the default heuristic rules.
For the Sensor to raise an alert, a blocked text should appear after the path in a request URI. For example, if private-banking is a path and get_balance is a blocked text, then in the request URI, get_balance should occur after private-banking for the Sensor to detect the blocked text.
To delete an existing blocked texts, hover over it and click the "x" icon.
Save
Click to save the configuration.
Click Save in the <Device Name/Interface> panel to save the changes.
Complete a configuration update to the Sensor for the configuration to take effect.
The Sensor protects your web application servers according to your configuration.
When the Sensor detects an attack through the default heuristic detection mechanism, it raises an alert for HTTP: SQL Injection Attack Detected (Trellix IPS attack ID: 0x4029d300). This is treated as an exploit attack. The Alert Details panel of Attack Log displays any reserved SQL keywords that the Sensor detected in the query. These are displayed in the SQL Injection Details section of the Alert Details panel.
When the Sensor detects a custom blocked text, it raises an alert for HTTP: Stored Procedure Name Detected by SQL Injection Heuristic Engine (Trellix IPS attack ID: 0x00011200). This is treated as a policy violation. The SQL Injection Details section displays the custom blocked text that the Sensor found in the corresponding HTTP requests.