You can use Trellix IPS to parse IPv4 and IPv6 traffic for attacks. You can customize the IPv4 and IPv6 parameter checks for a Sensor using the IP Settings page. IP parameters are effective only when the configured Sensor is deployed in inline mode.
Note
Trellix IPS does not prevent DoS attacks involving IPv6 traffic.
NS-series Sensors can parse IPv6 packets.
Click the Devices tab.
Select the domain from the Domain drop-down list.
On the left pane, click the Devices tab.
Select the device from the Device drop-down list.
Select Setup → Advanced → IP Settings.
To edit a parameter, specify a new value and click Update for that parameter.
Note
You must reboot the Sensor for the changes to take effect.
To restore the default values, scroll down to the bottom of the page and click Restore.
Caution
To prevent system errors, Trellix recommends that only users with detailed knowledge of IP configure these settings.
Trellix IPS can handle tunneled traffic.
The communication between your Manager server, client, and Sensors can only be in IPv4.
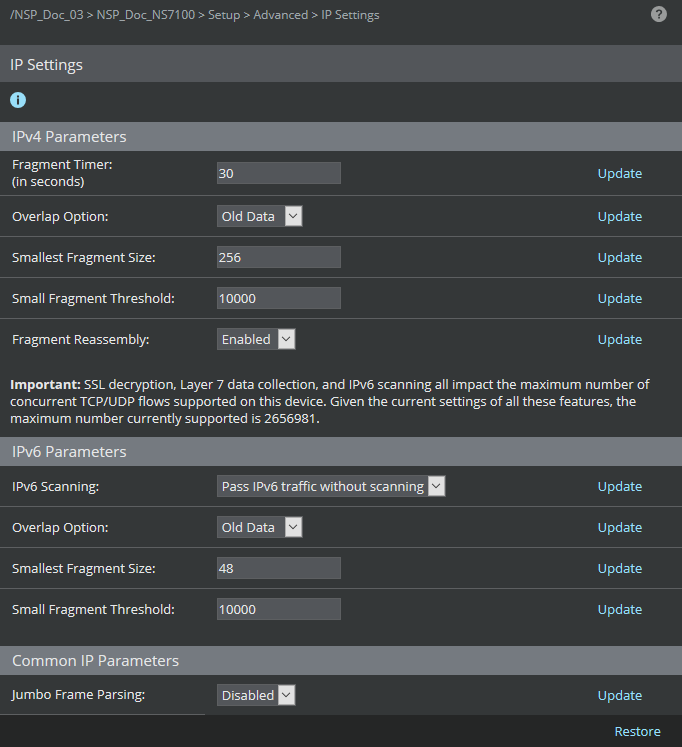
Option
Definition
IPv4 Parameters
Fragment Timer (in seconds)
Time to wait for all fragments of an IPv4 or IPv6 flow to be received or the transmission is dropped.
The default value is 30 seconds.
Overlap Option
Fragmented IPv4 packets might overlap, thus you need to select which data to process first - the newer data or the older data. By default, new data is processed first.
Old Data — Common for Windows and Solaris systems
New Data
Smallest Fragment Size
Smallest allowable size for an IPv4 fragment to be seen as "normal." All IPv4 fragments under this size are counted toward the IPv4 Small Fragment Threshold.
The default size is 256. You can modify this to a value which is a multiple of 8 and is between 8 and 1480. You can enter a value between 8 and 1480 in multiples of 8.
Small Fragment Threshold
The number of IPv4 fragments under the IPv4 Smallest Fragment Size allowed in 60 seconds. If this threshold is exceeded, an alert is sent.
The default is 10000. You can modify this to a value between 100 and 100,000.
Fragment Reassembly
When enabled, fragmented IPv4 traffic is held and reassembled to allow inspection. Disabling this option may help if you are experiencing dropouts in traffic, since partial fragments may timeout and be dropped while held. By default, fragment reassembly is enabled.
IPv6 Parameters
For IPv6 traffic, system events are generated for the following:
Reserved address where source or destination address is all zeros or 15 zeros then 1.
Final fragment with zero offset where next header = 44, fragment offset =0, and fragment header M = 0.
You can view system events. For more information, see Trellix Intrusion Prevention System Product Guide.
IPv6 Scanning
Specify how the Sensor should process IPv6 traffic.
Drop all IPv6 traffic (inline only) — The Sensor drops IPv6 traffic in the inline mode.
Pass IPv6 traffic without scanning — The Sensor passes IPv6 packets but does not scan them for attacks.
Scan IPv6 traffic for attacks — The Sensor scans IPv6 traffic for attacks.
If you select Scan IPv6 traffic for attacks or if you had selected this earlier and you are selecting a different option now, then you need to reboot the Sensor for the change to take effect.
By default, IPv6 packets are not parsed but allowed to pass.
You can check the IPv6 status of a Sensor using the
statuscommand from Sensor CLI.
Overlap Option
Fragmented IPv6 packets may overlap, thus you need to select which data to process first: the newer data or the older data.
Old Data — Common for Windows and Solaris systems
New Data
Drop — The Sensor drops any overlapping fragments.
By default, older data is processed first.
Smallest Fragment Size
Smallest allowable size for an IPv6 fragment to be seen as "normal." All IPv6 fragments under this size are counted toward the IPv6 Small Fragment Threshold.
The default size is 48. You can modify this to a value which is a multiple of 8 and is between 40 and 1280.
Small Fragment Threshold
The number of IPv6 fragments under the IPv6 Smallest Fragment Size allowed in 60 seconds. If this threshold is exceeded, an alert is sent.
The default is 10,000. You can modify this to a value between 100 and 100,000.
Common IP Parameters
Jumbo Frame Parsing
When enabled, Trellix IPS allows jumbo frame parsing of up to 9,216 bytes of IP payload for the following Sensor models:
NS9600, NS9500, NS9300, NS9200, NS9100, NS7600, NS7500, NS7350, NS7250, NS7150,NS7300, NS7200, NS7100, NS5200, NS5100, and NS3600
IPS-VM600, IPS-VM5000, IPS-VM5000-SSL, and IPS-VM600-SSL on ESXi and KVM.
IPS-VM600-VSS-SSL on AWS, Azure and GCP.
By default, jumbo frame parsing is disabled.
After enabling this setting, update the configurations on the Sensor, and reboot the Sensor for the changes to be effective.
Note
Jumbo frame parsing is not supported on NS3500, NS3200, and NS3100 Sensors.