Use this file to discover all available pages before exploring further.
The new docs.trellix.com features a modernized UI and AI-powered conversational search. Content is currently available in English, with additional languages launching in early November 2026. We hope you enjoy the updated experience.
Trellix IPS allows you to configure an SNMP server to which system audit information is sent from the Manager. You can configure more than one SNMP servers where you want to send audit messages. You can configure the SNMP servers for each admin domain separately. The SNMP server configured for a root admin domain can be different from the SNMP server configured for its child domains. When the
Children and the
Current checkboxes are selected while configuring an SNMP server for the root admin domain, the SNMP server configured for the child domain will forward notifications to both the parent and child domain SNMP servers. When the
Children checkbox is not selected in the root admin domain, then the child domain will use only the SNMP server configured for that domain to forward notifications. The
Manager displays the SNMP servers that have been configured. The fields in this page are described within the configuration steps that follow.
For SNMP forwarding, the root domain and parent domains have the option to include audit information from all corresponding child domains.
To configure an SNMP server from your Manager, do the following:
Select
Enable SNMP Notification (default is
No) and click
Save.
Click
.
The
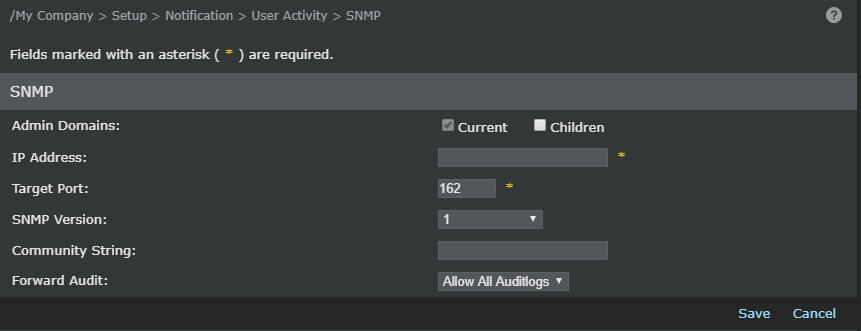
SNMP page is displayed.
Fill in the following fields:
Field
Description
Admin Domains
Enables VLAN based reconnaissance
IP Address
Disables VLAN based reconnaissance
Target Port
Target server's SNMP listening port. The standard port for SNMP, 162, is pre-filled in the field.
SNMP Version
Version of SNMP running on the target SNMP server. Version options are 1, 2c, Both 1 and 2c, and 3.
Community String
Type an SNMP community string to protect your
Trellix IPS data. SNMP community strings authenticate access to Management Information Base (MIB) objects and functions as embedded passwords.
Forward Audit
Choose the audit logs to be forwarded. The options are
Allow All Auditlogs,
Failed Only,
Successful Only, and
In Progress Only.
The following fields appear only when SNMP Version 3 is selected.
User Name
Type a username that will be used for authentication.
Authoritative Engine ID (Hex Values)
The Authoritative (security) Engine ID of the Manager used for sending SNMP version 3 REQUEST messages by Primary Manager
The hex value of the Authoritative Engine ID should have only even pairs (For example, you can have hex value of 4 pairs like 00-1B-3F-2C).
Note
MAC address can also be used as Authoritative Engine ID.
Authoritative Peer Engine ID (Hex Values):
Note
The
Authoritative Peer Engine ID field is available while configuring SNMP version 3 only after successful creation of an MDR pair.
The authoritative (security) engine ID used for SNMP version 3 REQUEST messages by Secondary Manager
Note
The Authoritative (security) engine ID for any Manager is unique. At any point of time, the
Authoritative Engine ID of the Manager is static irrespective of Manager status in case of an MDR pair. That is, when MDR switchover occurs, the authoritative engine ID of the Manager will not change with the status of the Manager. Hence, the alerts generated from the Primary and Secondary Manager will have their respective authoritative engine IDs.
Note
After successful deletion of an MDR pair, the Authoritative Engine IDs are retained by the respective Managers.
Authentication Level
This specifies the authentication level and has the following categories:
No Authorization, No Privileges — Uses a user name match for authentication
Authorization, No Privileges — Provides authentication based on the MD5 or SHA algorithms
Authorization and Privileges — Provides authentication based on the MD5 or SHA algorithms. It also provides encryption in addition to authentication based on the DES or AES standards.
The following fields appear only when
Authorization, No Privileges or
Authorization and Privileges is selected in Authentication Level.
Authentication Type
The authentication protocol (MD5 or SHA) used for authenticating SNMP version 3 messages
Authentication Password
The authentication pass phrase used for authenticating SNMP version 3 messages
Encryption Type
The privacy protocol (DES or AES) used for encrypting SNMP version 3 messages
Privacy Password
The privacy pass phrase used for encrypting SNMP version 3 messages
Click
Save.
To edit or delete an SNMP server, select the appropriate server from the list of SNMP servers and use the desired option ( or
).
 .
The SNMP page is displayed.
 or
 ).