Prerequisites:
You have created an advanced or classic Firewall policy to which you want to add stateless access rules.
You have created the rule objects, especially the service or service group rule objects, required to create your stateless access rules.
Create stateless access rules to allow or block certain traffic without deeper inspection.
Select Intrusion Prevention → Policy Types → Firewall.
Double-click the Firewall policy in which you want to add the stateless rules.
In the Firewall window, click Access Rules.
Select the top-most rule and click
 .
Note
It is recommended to have the stateless rules above any of the other rules.
Optionally, double-click the Description field to describe the rule.
Select the appropriate values for Source Address, Source User, Destination Address, Effective Time, and Direction.
For Application, select the required Service and Service Group rule objects.
In the Response column, select Stateless Drop or Stateless Ignore.
Click Save.
Update the Sensor configuration for the rule to be enforced.
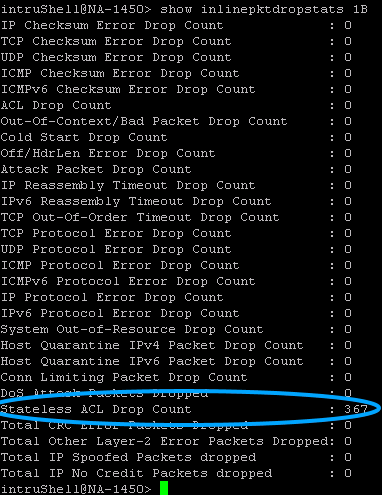
You cannot log the packets that matched a stateless access rule. However, you can view the number of packets dropped by using the
show inlinepktdropstats <monitoring port>command on the Sensor CLI. You cannot view the number of packets that were ignored according to stateless access rules.Count of packets dropped according to stateless access rules