SSL configuration includes enabling SSL decryption, enabling packet logging for SSL encrypted attacks, setting the number of SSL flows to monitor simultaneously, and setting the session cache time.
Important
If you enable or disable SSL decryption on a Sensor or modify the count of SSL flows, you must reboot the Sensor for the changes to take effect. You can opt for a hitless or full reboot.
For NS-series Sensors, you must do a full reboot as hitless reboot is not supported when SSL decryption is enabled.
In case of a virtual Sensor, if you enable or disable SSL decryption or modify the count of SSL flows, the Sensor will auto reboot.
In public cloud, if a virtual Sensor is added to a Cluster which has inbound SSL enabled, the SSL decryption configuration and the SSL key is automatically pushed to the new Sensor. The Sensor will auto reboot after the configuration push is complete.
Select Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → SSL Decryption.
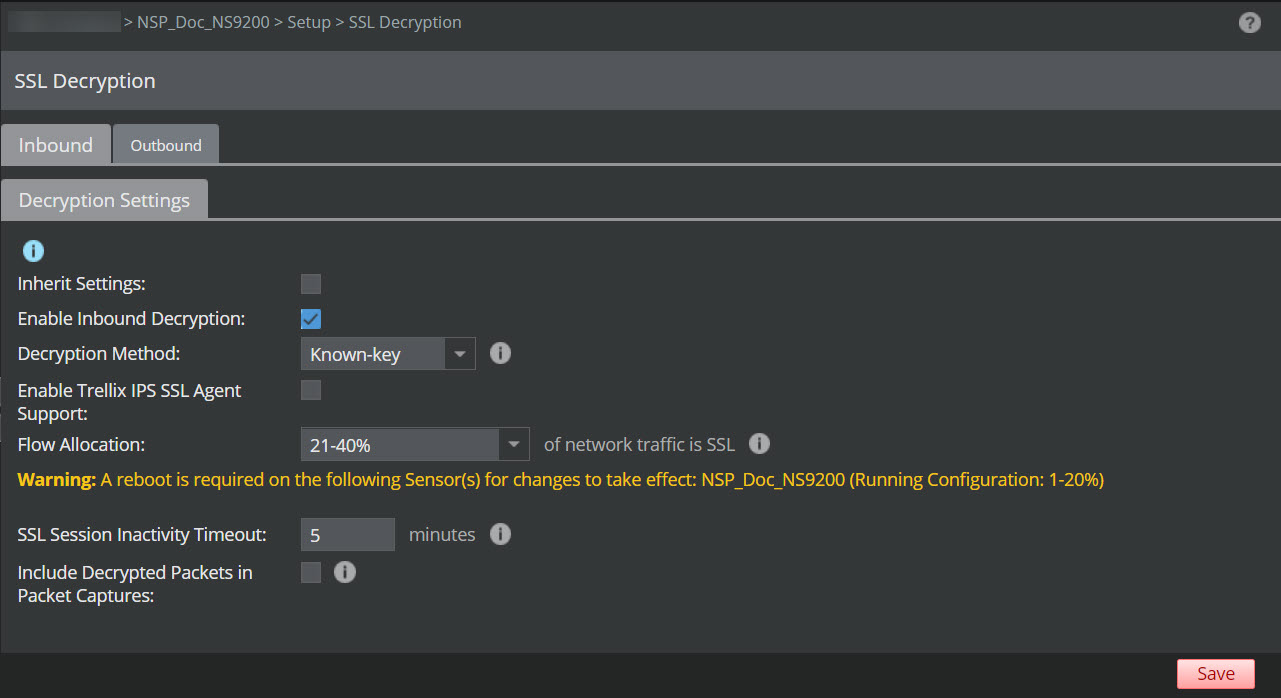
On the Inbound tab, select Decryption Settings tab.
Deselect Inherit Settings to override the settings of the parent domain.
Select the Enable Inbound Decryption checkbox.
From the Decryption Method drop down, select Known-key.
To enable decryption using the shared key method for Diffie-Helman, click the Enable Trellix SSL Agent Support checkbox.
For Agent based method, enter the Maximum Concurrent Agent Connections to limit the number of connections to avoid overloading the Sensor.
The maximum number of concurrent connections supported are 1024 and minimum is 1.
Select the percentage for SSL flows from the Flow Allocation drop down.
This value represents the percentage of SSL flows that you expect to see on your network so that the Sensor can pre-allocate a corresponding number of SSL flows. This configuration helps the Sensor to balance its resources between the total number of concurrent flows and number of SSL flows it is capable of handling. 21-40 % is allocated as the default value.
The options for Flow Allocation are:
1-20%
21-40%
41-60%
61-80%
81-100%
For more information on total SSL flows supported for different Sensor models, go to Sensor limits for SSL flows.
Enter the time duration in minutes for SSL Session Inactivity Timeout. The default value is 5 minutes. The maximum value you can configure is 120 minutes.
This time relates to session resumption in SSL. The value represents the duration for which a session is kept alive after the last connection closes. This value must be equal to or slightly longer than the session cache time on the corresponding server.
Note
A Sensor could be processing traffic destined to many servers. Due to this, the number of sessions the Sensor can maintain may be considerably lower than the number the servers that can be maintained. When the Sensor runs out of SSL sessions, SSL flows will not be processed and an alert is raised in Attack Log.
Optionally, select Include Decrypted Packets in Packet Capture.
If this setting is configured, the Sensor captures encrypted and decrypted packets if an attack is detected. Otherwise only encrypted packets are captured.
For the Agent based method, add the web server IP addresses with the agent installed in the Permitted Web Servers section. Only the web servers added can connect to the Sensor.
To add an IP address of the web server, enter the IP address in New IPv4/IPv6 CIDR block and then click Add.
The maximum number of permitted web servers for IPv4 and IPv6 are 64 together.
Tip
The IPv6 IP address is different from IPv6 CIDR address. For example, in the CIDR address 209.173.53.167/20 the /20 indicates that the first 20 bits are used for network ID and the remaining 12 (there are 32 bits in the IP address) are used for host ID. You can also use tools to calculate and verify the IPv6 CIDR address range.
Click Save.
Any change to the direction of SSL Decryption will require you to reboot the Sensor.
Select Manager → <Admin Domain Name> → Troubleshooting → Logs.
View the critical messages on the Faults tab for the corresponding Sensor to see if a Sensor reboot is required.
If yes, then do a hitless or full reboot of the Sensor.
Note
For NS-series Sensors, hitless reboot is not supported when SSL decryption is enabled.