Important
From the 11.1 Update 11 release:
You can configure the NS9600 Sensor as a high-capacity Suricata Sensor. This Sensor supports high-performance environments and scales to 40,000 Suricata rules while inspecting up to 100 Gbps of network traffic.
Standard IPS features do not apply to NS9600 Sensors configured as Suricata Sensors.
Prerequisites:
Trust must be established between the Manager and Sensor. For more information, see Add the NS9600 Sensor as a Suricata Sensor to the Manager.
You must configure the NS9600 Sensor as a Suricata Sensor. For more information, see Configure Sensor information.
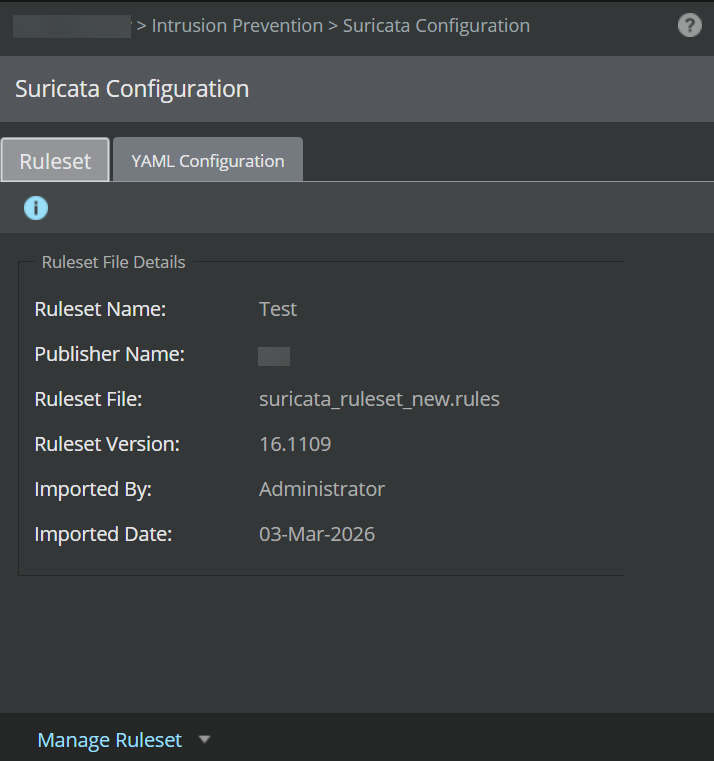
When you are configuring the policies, you must define Sensor behavior using Ruleset and YAML Configuration files. To define Suricata policies, go to Policy → <Admin Domain Name> → Intrusion Prevention → Suricata Configuration. The Suricata Configuration page is displayed.
Suricata Configuration