Use the menu options in this section to configure user mapping groups for authorization.
To configure user mapping groups:
Log in to the NDR as npadmin using the NDR IP address or FQDN. For example:
$ ssh npadmin@10.1.0.1or
$ ssh npadmin@exampleFQDNEnter privileged mode:
npadmin@ia> enableEnter the npadmin password. The password can be 5 to 24 characters long.
[sudo] password for npadmin: <password>Enter configuration mode:
npadmin@ia# configure systemEnter configuration CAC mode.
npadmin@ia(config)# authorizationIn the CAC/PIV configuration menu, select
2to configure Active Directory. The Active Directory configuration menu appears.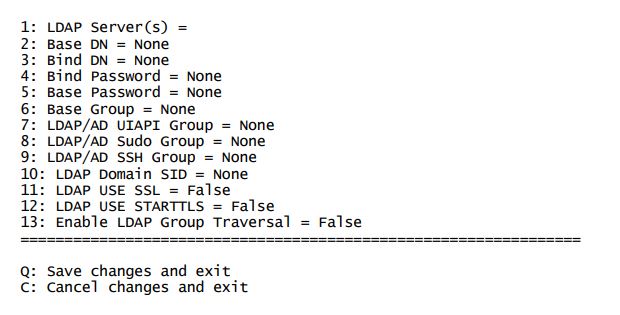
Select
7to add the user attributes for the X.509 certificates to the uiapi group mapping field for authorization (for example,[CN=engpxuiapi,OU=AdminGroups,OU=Engineering,DC=testad,DC=eng,DC=fireeye,DC=co m]). PressEnter.Select
Qto save your changes and exit the menu