Each of the top N security tables has one core attribute that helps you to start a filter. Select the required admin domain from the Domain drop-down list. The Threat Explorer page displays data applicable to that admin domain only. The Include child domain is selected by default. This can be deselected when data for the admin domain need not include data from the child domain. Click the core attribute to view the details of the selected attribute.
The core attributes of the top N security tables are explained in the following table.
Top N Table Name | Core Attribute |
|---|---|
Top Attacks | Attack Name |
Top Attackers | Attacker IP Address |
Top Targets | Target IP Address |
Top Attack Applications | Application Name |
Top Executables | Executable Hash |
Top Malware | Malware File Hash |
Sort options
To sort the tables by specific attributes, select from the sort options at the top right corner of each top table. Use these options to select the attribute of your choice from the drop-down list.
Scenario
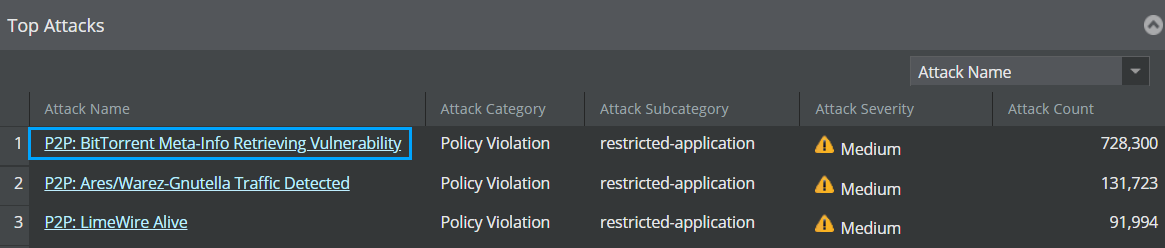
The core attributes are hyperlinked in the respective tables in the default view. For example, in the default view, the core attribute, Attack Name, of the Top Attacks is hyperlinked.
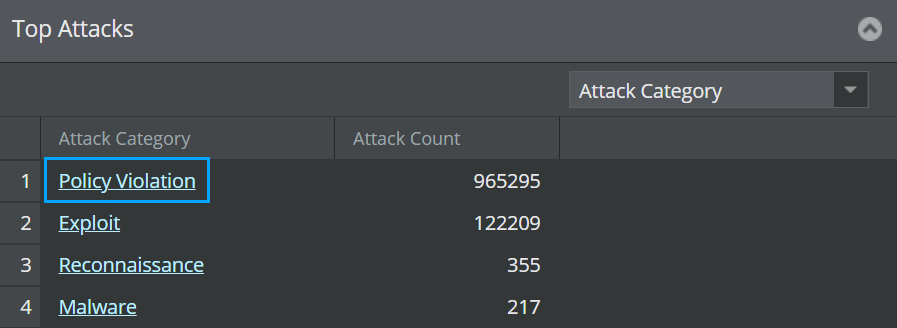
But, if you want to sort the tables by specific attributes, then the non-core attribute can also appear as a hyperlink. For example, if you want to sort the Top Attacks table by the Attack Category attribute, then the selected attribute, Attack Category, will be hyperlinked.
When you click a core attribute and start the filter:
The page is refreshed and a new table is added along with the existing top N tables, which shows the specific details of the selected core attribute.
The same top N security tables are displayed; but the data in each table is displayed according to the selected core attribute and admin domain.
Important
You can never view more than one attack, attacker, target, application, malware and admin domain combination at the same time.