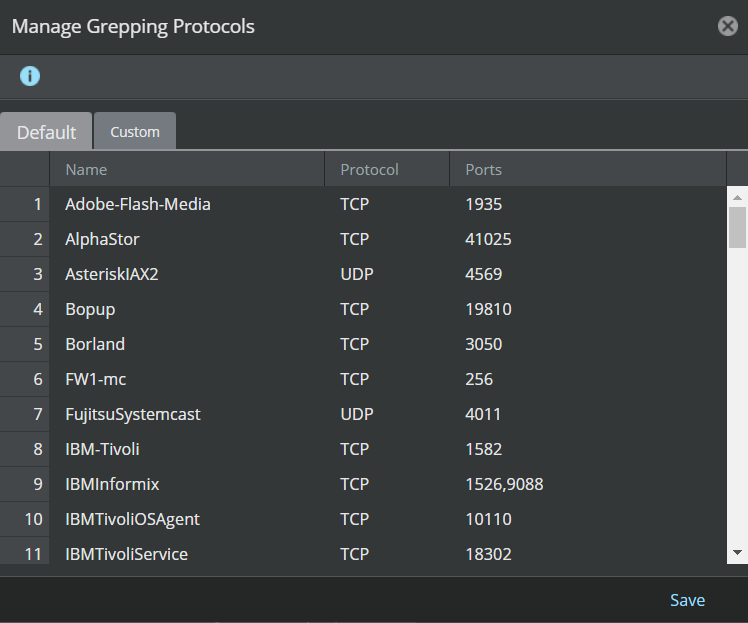
Not all traffic can be supported by previously defined protocol specifications. Thus, in some cases, you may need to define a different means of separating out certain protocol traffic. The Packet Grep Protocol feature (Packet Search > Manage Packet Search Protocol) enables you to create pattern matching searches in a particular protocol traffic that is not separately parsed.
Packet searching is commonly known as packet grepping. The term grep refers to the Unix command "g/re/p," which executes a global search for a regular expression, and prints the lines that contain pattern matches. In essence, a protocol packet grep is a search for a fixed pattern in either the request or response of an unsupported protocol flow.
Protocols, such as HTTP and FTP, have defined specifications and destination ports. For example, HTTP primarily uses port 80, but is also common on port 8080. A Sensor monitoring traffic identifies the HTTP traffic by the protocol's common traits, and checks the traffic against standardized (RFC) HTTP traffic specifications. If packets are determined to be suspicious through signature tests, an alert is sent from the Sensor to the Manager. In the event that a Sensor does not recognize the protocol of a monitored transmission through signature, anomaly, or packet search tests, the packets are sent to a general state machine and examined against user-configured pattern-matching checks. If a pattern is matched, an alert is raised.
For example, port 1387 on one of your Payroll servers is receiving undetermined protocol connection requests atop TCP. You have confidential information on this server, so protecting your data from suspicious searches or requests is crucial. You can create a packet search instance in requests via TCP to port 1387, then create a Trellix IPS Custom Attack that defines a regular expression pattern that alerts upon being matched.
Several packet search protocol instances are provided with Trellix IPS. These applications use protocols that are not defined by an RFC nor by a defined Trellix IPS protocol specification. Some of these instances, such as pcAnywhere and NetMeeting, represent legitimate applications that are allowed by network policy within/into some networks, but which may be used for malicious purposes.
Note
You cannot delete any of the Trellix IPS-defined packet grep protocols.