To protect VMs, each VM needs to be part of a protected VM group. The definition of the group contains the following:
Prerequisites:
VM membership by subnets they belong to.
Cluster that should inspect traffic from these VMs.
Security policy that applies to these VMs.
Note
If a VM is not part of a protected group, the VM will remain in unprotected state.
To create a Protected Group, perform the following steps:
Login to the Trellix IPS Manager instance.
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Manager.
Select vIPS Protected Groups tab.
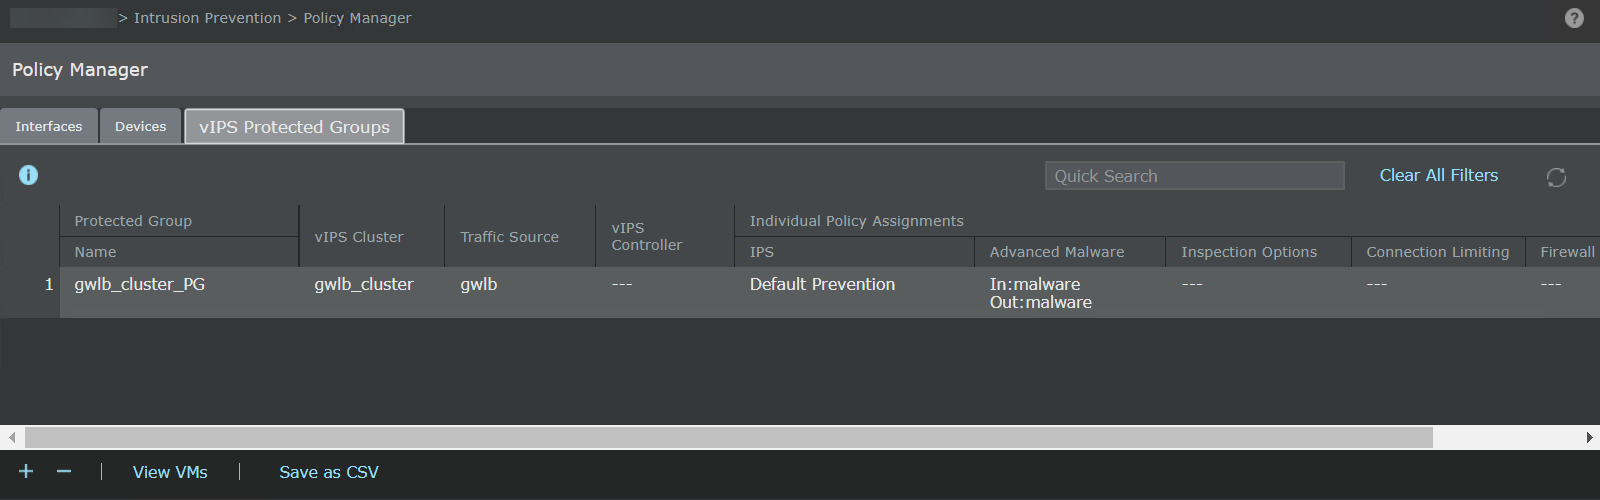
The description of columns on the vIPS Protected Group tab is given below:
Option descriptionsOption
Description
Protected Group
Name — Name of the Protected Group
Note
The minimum length for a name is 1 character. The name can contain up to 50 alphanumeric (upper or lower case letters) characters, including hyphens and underscores. The name must begin with a letter.
Description — Description of the Protected Group
Note
The minimum length for description is 1 character. The maximum allowed character length is 255 characters.
Inspection Mode — Displays the mode of inspection as IPS
vIPS Cluster
Cluster of instances for which the Protected Group applies
Traffic Source
Displays the traffic source as GWLB
vIPS Controller
This does not apply to GWLB
Individual Policy Assignments
IPS — Type of IPS policy applicable for the Protected Group
Advanced Malware — Malware policy applicable for the Protected Group
Inspection Options — Inspecting policy applicable for the Protected Group
Connection Limiting — Connection limiting policy applicable for the Protected Group
Firewall — Firewall policies applicable for the Protected Group

Refresh the status of all the Protected Groups.
Search
Enter the keyword to search the required Protected Group.

Create a new Protected Group.

Deletes a Protected Group
Save as CSV
Creates a .csv list of the list of Protected Groups
View VMs
To view the VMs managed by the Protected Group
To add a Protected Group, click
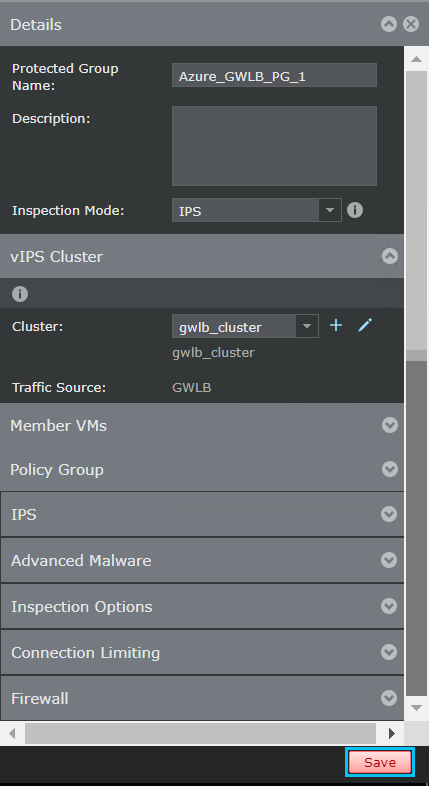
. Enter the details for the Protected Group in the Details window.Note
For each account you wish to secure, Trellix recommends you to create a separate protected group for different accounts. In the event of an attack, this will help in identifying the account that was attacked.
Option descriptionsOption
Description
Details
Details of the Protected Group
Protected Group Name — Name of the Protected Group
Note
The minimum length for a name is 1 character. The name can contain up to 50 alphanumeric (upper or lower case letters) characters, including hyphens and underscores. The name must begin with a letter.
Description — A brief description of the Protected Group
Note
The minimum length for description is 1 character. The maximum allowed character length is 255 characters.
Inspection Mode — Select the mode of inspection as IPS.
vIPS Cluster
Cluster - Specify the Cluster for the Protected Group.
Traffic Source - Displays the traffic source as GWLB
Member VMs
Specifies the VMs for the Protected Group
Click Add to add the subnet CIDRs that you want to include in this Protected Group.
vIPS Cluster
Cluster - Specify the Cluster for the Protected Group.
Traffic Source - Displays the traffic source as GWLB
Policy Group
Specify the Policy Group.
IPS
Specify the IPS policy for the Protected Group.
Advanced Malware
Specifies the Malware policy for the Protected Group
Inbound Policy — Select the Malware policy for inbound traffic.
Outbound Policy — Select the Malware policy for outbound traffic.
Inspection Options
Specify the Inspection policy for the Protected Group.
Connection Limiting
Specify the Connection Limiting policy for the Protected Group.
Firewall
Specify the Firewall policy for the Protected Group.
Interface Policy — The type of firewall policy
Effective Rules —
Click on Inbound to view the inbound rules for the selected interface policy.
Click on Outbound to view the outbound rules for the selected interface policy.
Note
To create a new policy or to edit an existing policy, see the Trellix Intrusion Prevention System Product Guide.
Click Save.
Upon successful saving, the Protected Group information is displayed on the vIPS Protected Groups tab.