This scenario is about creating a Custom Attack Definition that uses packet grep protocol match to detect if the DNP3 protocol contains a specific character sequence.
In order to write a proper Native Trellix IPS Format Custom Attack for this example, you must identify several key elements:
Application protocol: dnp3
Packets to parse: Request Packets Only
Text to match: \x00\x00\x00\x3a\x20\x45\x56\x00\x0a
Steps to create the attack definition for this example:
In the Custom Attack Editor, click
 .
The New Custom Attack interface opens.
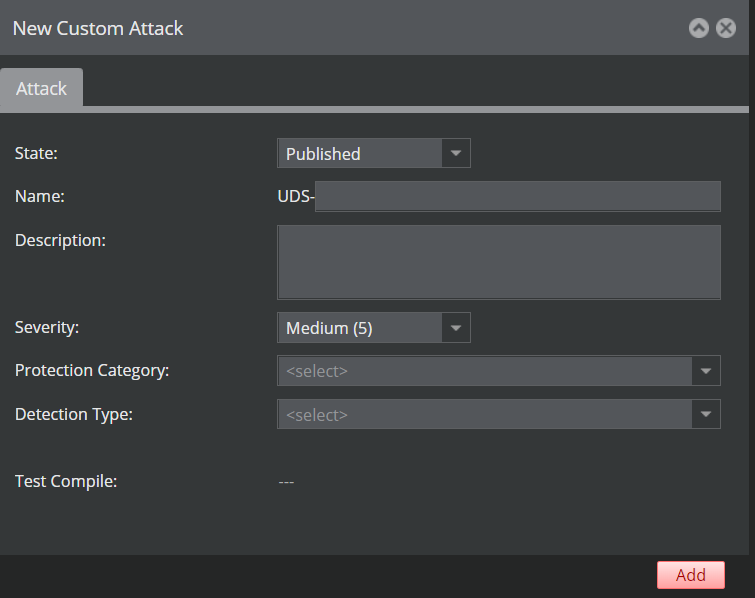
Select one of the options from the State drop-down menu.
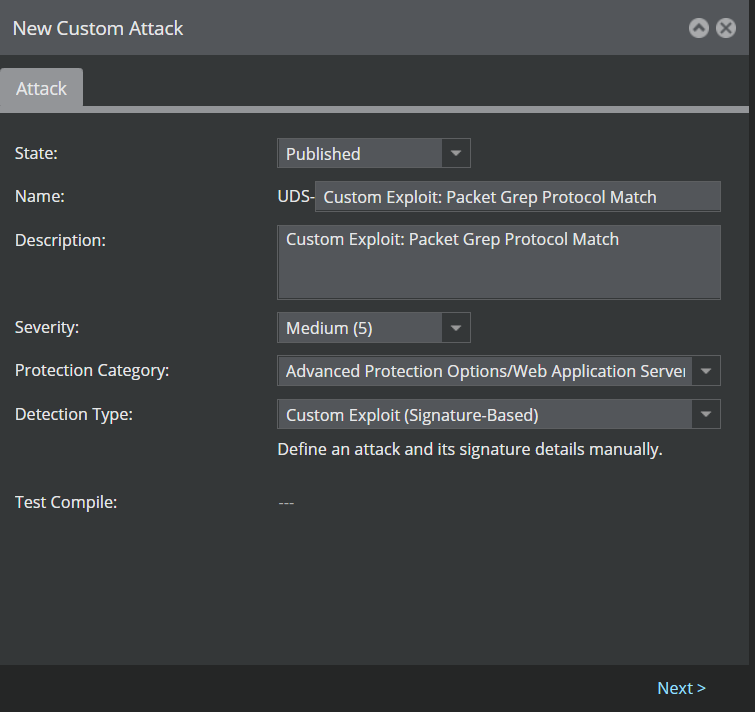
You can specify a name such as "Custom Exploit: Packet Grep Protocol Match" as the Name.
The letters "UDS" (user-defined signature) are appended to the front of the name upon completion; thus, this attack appears as "UDS-Custom Exploit: Packet Grep Protocol Match" in the Custom Attack Editor, as well as the attack database when you save in the Manager server.
Type a description for your attack. This area can be used for your notes or other specific information pertinent to your new attack.
You can select Medium (5) as the Severity because this example scenario does not necessarily involve malicious activity.
Select Advanced Protection Options/Web Application Server as the Protection Category.
Select Custom Exploit (Signature Based) from the Detection Type drop-down menu for the attack.
Click Next.
Select Client or Server as Attack Target.
Select Attack Packet Only as Blocking (As Applicable).
In the Matching Criteria section, select Protocol as the Criterion and select pktsearch as the protocol.
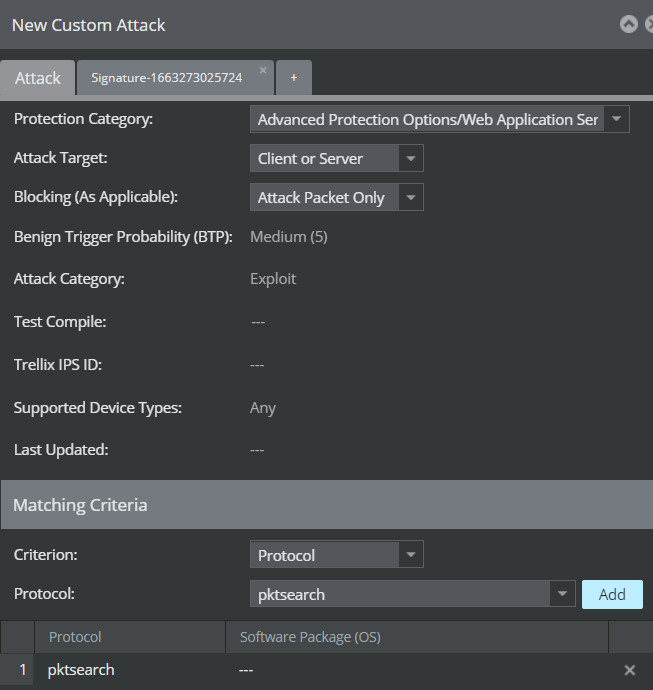
Attack details configuration is complete. Continue to create signature.