Sensors support both normal blocking and SmartBlocking. SmartBlocking is the blocking of attacks based on the Benign Trigger Probability (BTP) value of the attack signatures which trigger the attack. Trellix recommends certain attacks for SmartBlocking, and these are referred to as Recommended for SmartBlocking (RFSB) attacks. While creating an attack set profile, you can enable SmartBlocking for those exploit, recon, or policy violation attacks for which Trellix has recommended SmartBlocking.
You can also create rules to choose attacks to be explicitly blocked by the Sensor as per your network requirements while creating an attack set profile. The configuration options on the Attacks to Block tab enables you to select minimum severity, categories, and subcategories of attacks which should be explicitly blocked by the Sensors. It works on the subset of data that comes in the form of Include rule(s) set on the Attacks to Include/Exclude tab. In other words, rules created on the Attacks to Block tab determine the attack definitions that are automatically set to be blocked in the corresponding IPS policy. For more formation, refer to the section Defining and using user-customizable blocking strategy to make self-adaptable IPS policies.
In the Manager, click Policy and select the required Domain.
Select Intrusion Prevention → Objects → Attack Set Profiles.
The Attack Set Profiles page is displayed.
Attack Set Profiles page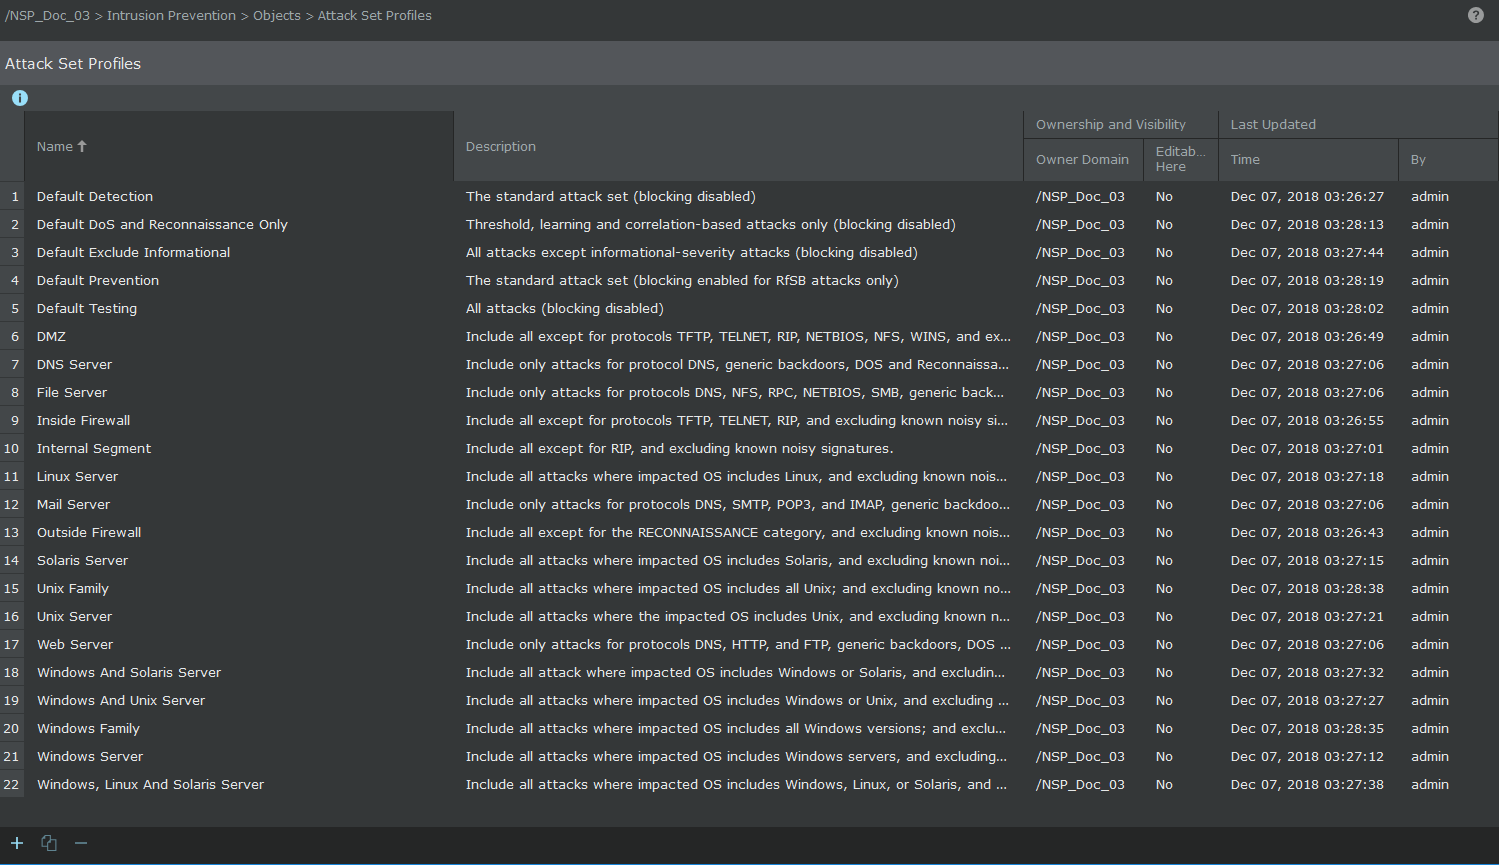
Click
 .
The new page with Properties tab is displayed.
Properties tab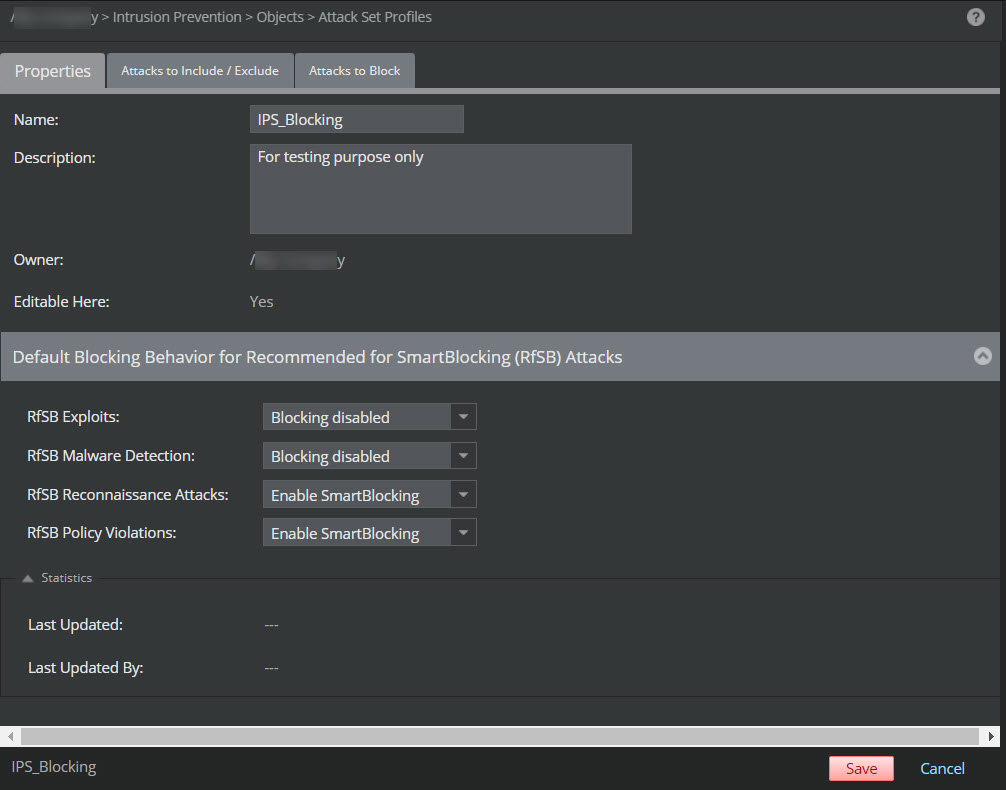
The following fields are displayed on the Properties tab:
Option
Definition
Name
Type the name of the attack set profile being created. The name should contain only letters, numbers, spaces, commas, hyphens and underscores.
Note
The name field should not be left blank and no special character should be entered while typing the name.
Description
Type the description of the attack set profile.
Owner
Displays the domain to which the IPS Policy belongs
Editable here
Indicates whether you can edit or delete the selected attack set profile from the current admin domain
Default Blocking Behavior for Recommended for SmartBlocking (RfSB) Attacks
To enable SmartBlocking, select the options from the drop-down list of the following categories:
RfSB Exploits
RfSB Malware Detections
RfSB Reconnaissance Attacks
RfSB Policy Violations
The available options for the above mentioned categories are Blocking disabled and Enable SmartBlocking.
Click Next to save the changes made on the Properties tab and go to the next tab. The Attacks to Include/Exclude tab is displayed.
Attacks to Include/Exclude tab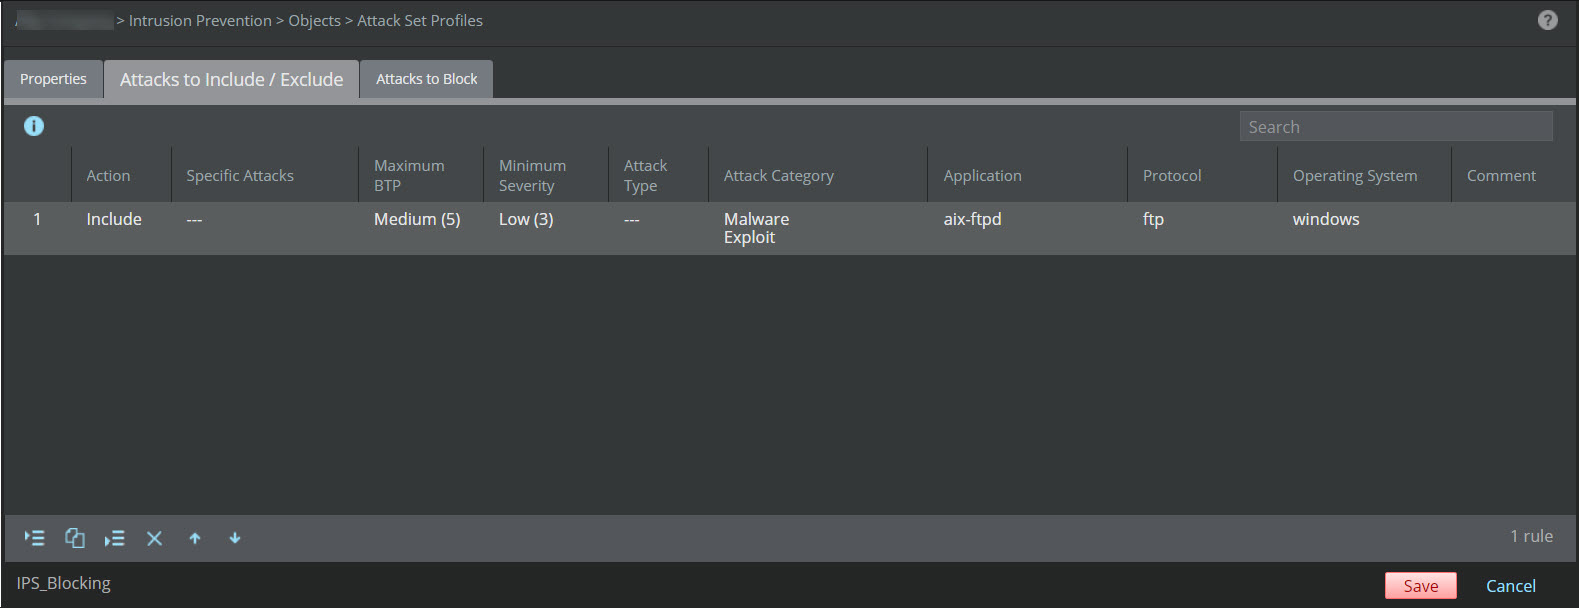
On the Attacks to Include/Exclude tab, click the appropriate button to insert a new rule.
You can insert a new rule by clicking either
 or
 icon. The Details panel is displayed.Details panel on Attacks to Include/Exclude tab
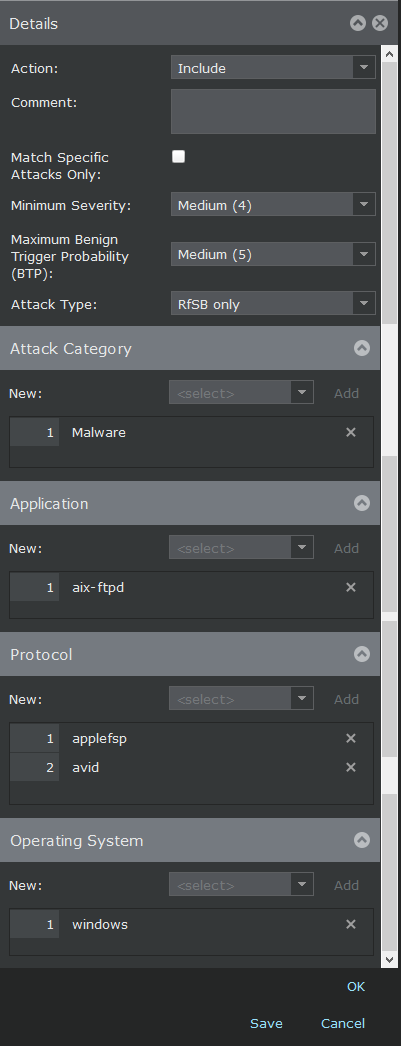
In the Details panel, select the appropriate options.
Option
Definition
Action
Select the action as Include or Exclude.
Comment
Enter additional comments, if any.
Match Specific Attacks Only
Select the checkbox if you want to mark the rule for a specific attack.
Minimum Severity
Select the minimum severity level from the drop-down list. The following are the available options:
None
Informational (0)
Low (1)
Low (2)
Low (3)
Medium (4)
Medium (5)
Medium (6)
High (7)
High (8)
High (9)
Maximum Benign Trigger Probability (BTP)
Specify the maximum probability of the search for this attack that will return a false positive. The following are the available options:
None (0)
Low (1)
Low (2)
Medium (3)
Medium (4)
Medium (5)
High (6)
High (7)
Attack Type
From the drop-down list, select the attack type as Any or RfSB only
Attack Category
Select the attack category from the drop-down-list.
The attack categories are:
Exploit
Malware
Policy Violation
Reconnaissance
Click the Add button to add the attack category to the list.
Click
 to remove the item from the list.
Application
Select the applications from the drop-down-list.
Click the Add button to add the applications to the list.
Click
to remove the application from the list.Protocol
Select the protocol from the drop-down-list.
Click the Add button to add the protocol to the list.
Click
to remove the protocol from the list.Operating System
Select the operating system from the drop-down-list.
Click the Add button to add the operating system to the list.
Click
to remove the operating system from the list.Specific Attacks
This section is displayed only if you select the Match Specific Attacks Only option.
Type and search for a specific attack by typing the first few letters of the attack in the text field. The list of attacks matching with the letters are displayed.
Select the required attack from the drop-down list.
Click on the Add button to add the attack to the list.
Click
to remove the attack from the list.Click OK to confirm the configuration changes.
Repeat the relevant steps to add more rules to the attack set profile being created. Click Next to save the changes made on the Attacks to Include/Exclude tab and go to the next tab.
The Attacks to Block tab is displayed.
Attacks to Block tab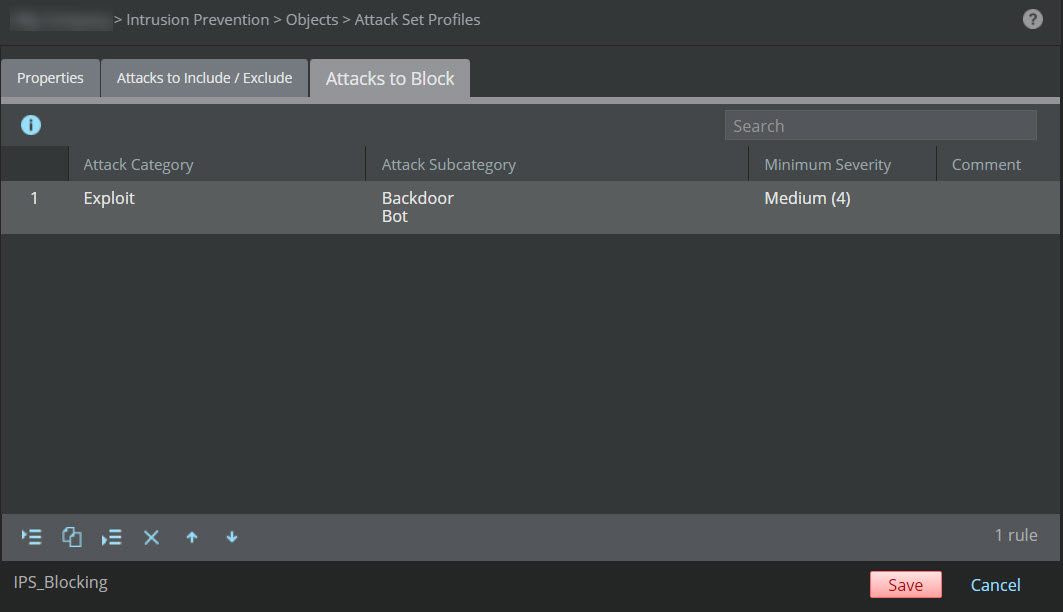
On the Attacks to Block tab, click the appropriate button to insert a new rule.
You can insert a new rule by clicking either
or icons. The Details panel is displayed.Details panel on Attacks to Block tab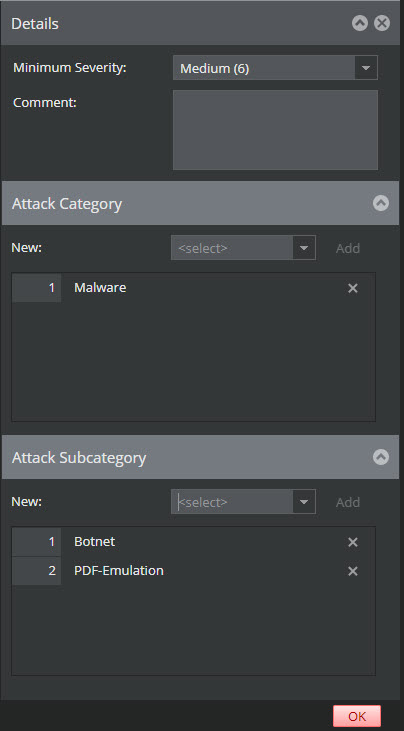
Note
You can create rule for blocking in custom attack set profiles only, as the default or preconfigured attack set profiles are read-only.
In the Details panel, select the appropriate options.
Option
Definition
Minimum Severity
Select the minimum severity level from the drop-down list. The following are the available options:
Medium (4)
Medium (5)
Medium (6)
High (7)
High (8)
High (9)
Note
The default value selected while creating a rule is High (9).
Important
Informational and Low severity attacks cannot be set for automatic blocking.
Comment
Enter additional comments, if any.
Attack Category
Select one or more attack categories as per your requirement from the drop-down-list. The attack categories available are the following:
Exploit
Malware
Policy Violation
Reconnaissance
Click the Add button to add the attack category to the list. Click
to remove the item from the list.Attack Subcategory
Select one or more attack subcategories for the attack category selected.
Click the Add button to add any subcategory to the list. Click
to remove the item from the list.Important
Attack subcategories are available only when you add an attack category.
You cannot select any attack subcategory if you have added two or more attack categories in a single rule. For example, if you want to block exploits and malware of severity 8 and backdoors and botnets of severity level 9, you need to create two separate rules - one with minimum severity level chosen as High (8), Attack Category selected as Exploit and Attack Subcategory selected as Backdoor, and another with minimum severity level chosen as High (8), Attack Category selected as Malware and Attack Subcategory selected as Botnet.
Click OK to confirm the configuration changes.
On the Attacks to Include/Exclude and Attacks to Block tabs, you can perform the following actions:
Option
Definition
Inserts a new rule above the currently selected rule
Inserts a new rule below the currently selected rule

Clones the currently selected rule

Deletes the currently selected rule

Moves the currently selected rule one row up

Moves the currently selected rule one row down
Note
Rules are cumulative on the Attacks to Include/Exclude and Attacks to Block tabs and the option to make changes in the rule order is solely to optimize viewing.
Click Save to save the Attack set profile configuration.
Your new attack set profile is listed in the Attack set Profiles page.