The Master Attack Repository (formerly Global Attack Response Editor or GARE) is an attack editor that works in concert with the policy and bulk editors. This editor, available only in the root admin domain, enables you to edit an attack definition's response once and have that modification applied across all policies that contain that attack definition, rather than having to find all policies that use a particular attack, and then modify the response on each of those policies one at a time. This includes the attack instances in the policies of a child domain. All attack response attributes can be customized (for example, Sensor response actions, logging, ignore rules, notifications).
Master Attack Repository displays the attacks that match the parameters in your selected attack set profile — all exploit attacks are categorized by protocol (that is, the application protocol they affect). From here, you can drill down to customize individual attack settings, such as ignore rules, Sensor responses, and notifications to be sent. This customization is optional, but Trellix recommends that you become familiar with them.
Using Master Attack Repository, you can modify exploit, DoS, and reconnaissance attack definitions. Do the following steps to view and configure the attack settings.
Task
-
On the
Attack Definitions tab, double-click on the row of the attack that you want to configure and update the settings. The attack details are displayed on the right panel displaying the settings under the
Settings tab.
Settings tab 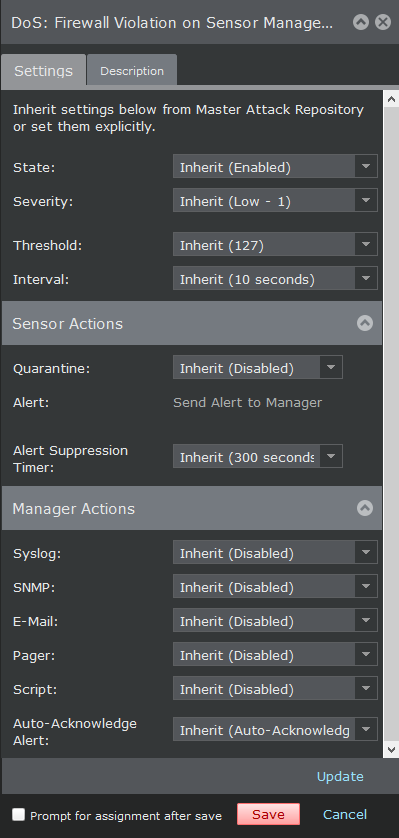
-
Configure the settings for the attack definitions
The following fields are displayed for attacks of categories such as exploit, policy violation, malware, and reconnaissance:
Option Definition State Select any following options: - Inherit
- Enabled
- Disabled
Severity Select the severity level of the attack: - Inherit
- Info - 0
- Low - 1
- Low - 2
- Low - 3
- Medium - 4
- Medium - 5
- Medium - 6
- High - 7
- High - 8
- High - 9
Threshold This field is displayed only configuring attacks of type DoS Threshold and Reconnaissance Correlation attacks. Select the severity level of the attack: - Inherit
-
Set explicitly
Note
If you select the option Set explicitly, specify the threshold value in the number field.
Interval This field is displayed only configuring attacks of type DoS Threshold and Reconnaissance Correlation attacks. Select the interval duration: - Inherit
-
Set explicitly
Note
If you select the option Set explicitly, specify the interval duration seconds in the number field.
Sensor actions Block Select any of the following blocking options: - Inherit
- Disabled
- Enable Blocking
- Enable Smart Blocking
Quarantine Select any of the following quarantine options: - Inherit
- Quarantine attacker
- Disabled
TCP Reset Select any of the following TCP reset options: - Inherit
- Reset src - resets to the source
- Reset dest - resets to the destination
- Reset src and dest - resets to the source and destination
ICMP Message Select any of the following ICMP message options: - Inherit
- Send host unreachable to source
- Disabled
Alert Select any of the following alert options: - Inherit
- Send alert to Manager
- Disabled
Alert Suppression Timer This field is displayed only configuring Sensor response for attacks of type Reconnaissance Correlation attacks. Select the severity level of the attack: - Inherit
-
Set explicitly
Note
If you select the option Set explicitly, specify the seconds in the number field.
Capture Packets Pre-Attack Packets Select any of the following pre-attack packet capture options: - Inherit
- Capture prior 128 bytes
- Disabled
Post-Attack Packets Select any of the following post-attack packet capture options: - Inherit
- Capture subsequent bytes
- Disabled
Flows to Capture This field is displayed only when you select Post-Attack Packets as Capture subsequent bytes. The following are the options available in this field:
- Inherit
-
Attack flow only
By selecting the option Attack flow only, a new drop-down list is displayed. Select any of the following options:
- Attack Packets only
- Next N packets - type the number of packets in the blank packets field.
- Next N time - select the time options from the given drop-down list. The options are:
- Seconds
- Minutes
- Hours
- Days
- Rest of flow
-
Flows from src and flows to src and dest
By selecting the option Flows from src and flows to src and dest, a new drop-down list is displayed. Select any of the following options:
- Next N packets - type the number of packets in the blank packets field.
- Next N time - select the time options from the given drop-down list. The options are:
- Seconds
- Minutes
- Hours
- Days
Bytes to Capture This field is displayed only when you select Post-Attack Packets as Capture subsequent bytes. The following are the options available in this field:
- Inherit
- All bytes in each packet
-
First N bytes in each packet
By selecting the option First N bytes in each packet , a new field to enter the number of bytes to capture is displayed. Type the number in the blank field.
Manager actions Syslog Select any of the following syslog options: - Inherit
- Send syslog message
- Disabled
SNMP Select any of the following SNMP options: - Inherit
- Send SNMP trap
- Disabled
Email Select any of the following email options: - Inherit
- Send e-mail message
- Disabled
Pager Select any of the following pager options: - Inherit
- Send page
- Disabled
Script Select any of the following script options: - Inherit
- Run script
- Disabled
Auto-acknowledge Select any of the following auto-acknowledgment options: - Inherit
- Auto-acknowledge alert
- Disabled
Update Click here to update the settings. Fields in the Capture Packets and Manager actions sections are displayed only when alerting (Alert field option) is enabled or inherited.
The fields in the Sensor actions section are not displayed for malware attack definitions that support advanced malware policies as these settings are configured in the malware policy. However, the Manager actions are configurable for such malware attacks.