The following table summarizes the rules for creating custom DoS policies in a network.
If you customize DoS: | Then... |
|---|---|
At the Interface level, for the entire interface or for a VLAN or CIDR ID (and a subinterface has not been created) | You cannot create subinterfaces for the interface. |
At the SubInterface level, for the entire subinterface or for a VLAN or CIDR ID within the subinterface | You cannot customize DoS at the interface level. |
For a VLAN interface with multiple VLAN tags, you can do one of the following:
Customize the inherited DoS policy and create multiple DoS policies for each of your VLAN tags. If you create DoS policies for your VLAN tags at the interface node, you cannot create subinterfaces for your VLAN tags.
Customize the inherited DoS policies and create multiple subinterfaces which can then have custom DoS policies. If you created subinterfaces for your VLAN tags, you cannot create custom DoS policies for any VLAN tags at the interface level.
For a CIDR interface with multiple CIDR-based addresses, you can do one of the following:
Customize the inherited DoS policies and create multiple DoS profiles for each of your CIDR addresses
Customize the inherited DoS policies and create multiple subinterfaces which can then have custom DoS policies. If you created subinterfaces for your VLAN tags, you cannot create custom DoS policies for any VLAN tags at the interface level.
In this example, suppose a Sensor is in SPAN mode, monitoring the traffic transmitting between the floors of a building. Sensor port G0/1 is the interface number.
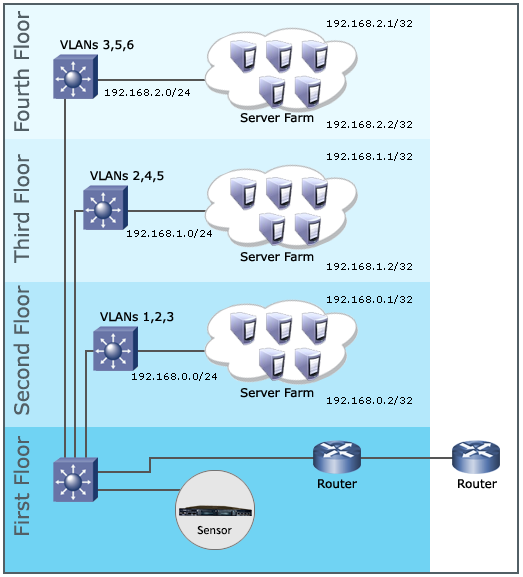
The above displays various custom DoS implementations. The traffic type scenarios that follow explain DoS policy customization options for each of the three interface types.