For outbound SSL traffic, when you access a secure server using SSL, the Sensor acts as a proxy between the client and the server. The Sensor intercepts the client request and forwards the request to the server as the client. The server receives the request and sends its certificate to the Sensor. The Sensor validates the server certificate using its list of trusted CA certificates. The Sensor uses the imported certificate to implement the re-signing functionality within the proxy. The re-signing certificate is used by the Sensor to re-sign the server certificate for validation by the client.
You can also create decryption exceptions to exclude certain outbound SSL traffic from decryption based on source or destination IP addresses, destination domain name, and URL category.
Notes:
You can configure Outbound SSL in inline mode only on NS9600 (standalone and stack), NS9500 (standalone), NS9200, NS9100, NS7600, NS7300, NS7200, NS7500, NS3600, IPS-VM600-SSL, IPS-VM600-VSS-SSL, and IPS-VM5000-SSL Sensors.
Decryption of VLAN tagged packets on Outbound SSL traffic in proxy-based method is supported in NS9600 (standalone and stack), NS9500 (standalone), NS7600, NS7500, NS3600, IPS-VM600-SSL, IPS-VM600-VSS-SSL, and IPS-VM5000-SSL Sensors.
Decryption of double VLAN tagged packets on Outbound SSL traffic in proxy-based method is supported in NS9600 (standalone and stack), NS9500 (standalone), NS7600, NS7500, NS3600, IPS-VM600-SSL, IPS-VM600-VSS-SSL, and IPS-VM5000-SSL Sensors.
You cannot configure Outbound SSL in SPAN or tap mode.
From 11.1.5.122, jumbo frame traffic with SSL encryption will be decrypted when SSL decryption is enabled.
You cannot configure proxy-based outbound SSL decryption on a stack of NS9500 Sensors.
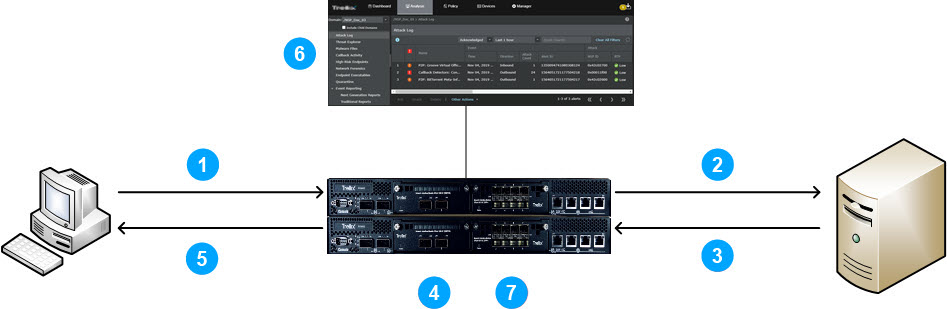
The client sends a secure request to the web server.
The Sensor intercepts the request and forwards it to the web server.
The web server responds to the request by sending its certificate to the Sensor.
Sensor validates (if configured) the certificate and drops the session if invalid.
Sensor uses its default resign certificate or custom resign certificate to establish the session with the client.
Sensor is able to decrypt and re-encrypt traffic in both direction using its private key.
The Sensor sends the response from the server to the client.
Sensor inspects the decrypted packets. If any malicious activity is found, the Sensor raises an alert in the Attack Log.
While decrypting Outbound SSL traffic, the Sensor may not be able to decrypt certain SSL flows due to certificate failures. The Sensor takes the configured action when such a failure occurs.
Port clustering for proxy-based SSL decryption in NS9500 standalone Sensor
Multiple monitoring port pairs in inline mode can be grouped together to create a port cluster. The same IPS policy will apply for traffic arriving on any of the inline pairs in the port cluster.
The following are the considerations for using port clusters with proxy based SSL decryption:
Port Cluster for proxy based SSL decryption is supported only for inline port pairs.
All paths in the network formed by the inline port pairs must be active paths (should not be blocked by any link layer protocols) on which packets can be forwarded.
Packets on the egress path (from the Sensor towards the client or server) may not follow the same path on which they arrived. For example, consider ports G1/1-G1/2, G1/3-G1/4 are grouped in a port cluster. A packet arriving on port G1/1 may exit from port G1/4.
SSL sessions will always be reported against the least index port of the port cluster even when the traffic is received on the other ports in the port cluster.
For example, if G1/1, G1/2, G2/1, and G2/2 are in a port cluster with proxy based SSL enabled, even if the client and server packets are received over the physical G2/1 and G2/2 links, the
show ssl stats outbound proxy sessionscommand displays that sessions are formed on G1/1 and G1/2. This behavior holds good even if ports G1/1 and G1/2 are not operational.