You configure callback activity options in an inspection option policy. You create inspection option policies at the domain level. Then, you can apply the inspection option policy to the required Sensor interfaces owned by that domain.
You can define the following callback activity features in an inspection option policy:
Define the CIDRs to be excluded from inspection for callback activity.
DNS-based detection of exempted domains according to domain name exceptions.
DNS-based detection of C&C server domains according to callback detectors.
DNS-based detection for FFSN and DGA.
HTTP-based detection of command and control servers according to callback detectors and multiple heuristic analysis for zero-day botnets.
When the Sensor begins its inspection for callback activity, it first verifies if the traffic is to be excluded from inspection for callback activity:
Regardless of the protocol, the Sensor checks if the source or destination of the traffic belongs to an excluded CIDR. If yes, the Sensor excludes that flow from inspection for callback activity.
If the protocol is DNS, the Sensor checks for domain name exceptions first and then C&C server domains.
If the protocol is DNS and the domain is not for a known C&C server, the Sensor inspects for FFSN and DGA.
If the protocol is HTTP, the Sensor checks if the HTTP request contains any IP addresses, domains, or URLs of C&C servers in callback detectors.
The Sensor checks for anomalies such as protocol anomalies and response errors in protocols and performs heuristic analysis to detect zero-day botnets.
In the Manager, select Policy → <Admin Domain Name> → Intrusion Prevention → Inspection Options.
The inspection option policies available for the admin domain are listed.
Complete the following to create an inspection option policy.
Click

Specify the details on the Properties tab and click Next.
Option
Definition
Name
Enter a relevant name for the inspection option policy.
Description
Enter the details for the policy.
Owner
Indicates the admin domain in which you are creating this policy.
Visibility
Owner and child domains — Select this option to make the policy available to the child admin domains of the current domain. You can apply this policy to the interfaces owned by the child domains, but cannot modify or delete the policy from the child domains.
Owner domain only — Select this option to restrict the policy to the current admin domain.
Editable Here
Indicates whether you can edit the policy in the current admin domain. If the policy is editable, it indicates that the current domain owns the policy.
Statistics
Last Updated — The date and time when the policy was last updated.
Last Updates By — Name of the user who last modified the policy
Assigments — Number of interfaces the policy is assigned to.
Prompt for assignment after save
Select if you want to be prompted to assign the policy to Sensor interfaces and sub-interfaces when you save the policy.
To use an existing inspection option policy, select an editable policy in the Inspection Options page and click

Select Inspection Options → Advanced Callback Detection.
Advanced Callback Detection tab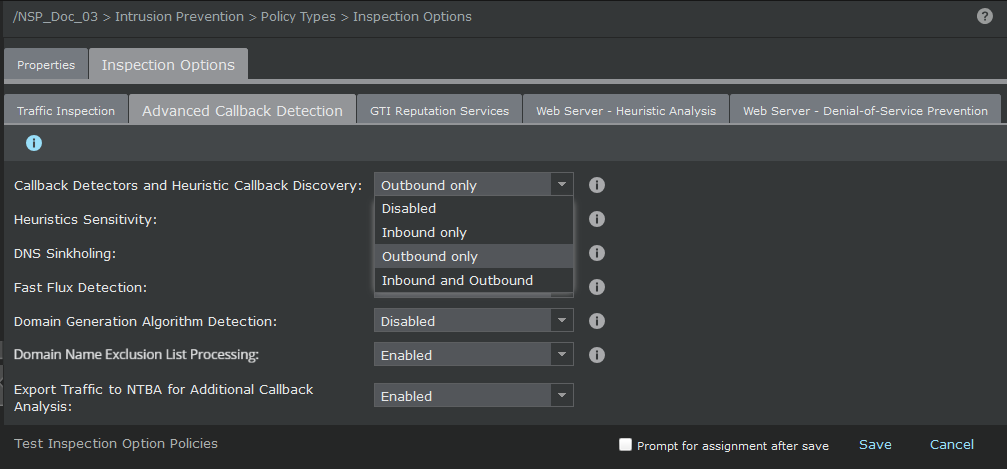
Complete the following steps to configure HTTP-based detection of command and control server information (IP addresses, domains, and URLs of command and control servers in the callback detectors) as well as multiple heuristic analysis for zero-day botnets.
Note
These heuristic analyses considers factors such as protocol anomalies and response errors in protocols. It does not include DNS-based heuristic analyses for FFSN and DGA detection.
From the Callback Detectors and Heuristic Callback Discovery drop-down list, select the required option. Additional options are displayed when you select an option other than Disabled.
Note
In case of HTTP traffic, you must enable HTTP response scanning in the same direction to protect your clients.
Disabled — Select to disable HTTP-based detection of IP addresses, domains, and URLs of C&C servers in the callback detectors as well as heuristic analyses for zero-day botnets. You can still enable DNS-based detection of FFSN, DGA, and exporting of traffic to NTBA for callback analysis.
Note
If you wish to disable Layer 7 Data Collection option in Traffic Inspection ensure that Callback Detectors and Heuristic Callback Discovery option is also disabled.
Inbound only — Select this option to inspect traffic in the inbound direction. For example, select this option to protect the servers in your inside network.
In case of HTTP traffic, the Sensor inspects the HTTP request traffic for callback activity. So, the Sensor inspects the HTTP traffic to the servers for callback activity. To also inspect the HTTP traffic to the clients for callback activity, you must enable HTTP response traffic scanning as well in the inbound direction in the same inspection option policy. The HTTP Response Traffic Scanning option is available on the Traffic Inspection tab.
Outbound only — Select this option to inspect traffic in the outbound direction. For example, select this option to protect the servers in your outside network or the clients in your inside network.
To inspect the HTTP traffic to the clients, you must also enable HTTP response traffic scanning in the outbound direction in the same inspection option policy.
Inbound and Outbound — Select this option to inspect traffic in either direction. This option might impact Sensor performance more than the options described above. In case of HTTP traffic to clients, you must also enable HTTP response traffic scanning in inbound and outbound.
Select Low, Medium, or High sensitivity level from the Heuristics Sensitivity drop-down.
The sensitivity level determines the level of confidence the heuristic engine must have for the analysis. For example, if you select low, the Sensor's heuristic engine must have a very high confidence that it is botnet traffic for it to raise the alert.
Low sensitivity level is selected by default.
This sensitivity setting does not apply to Fast Flux Detection and Domain Generation Algorithm Detection heuristic engines.
C&C detection (HTTP-based) and heuristic analysis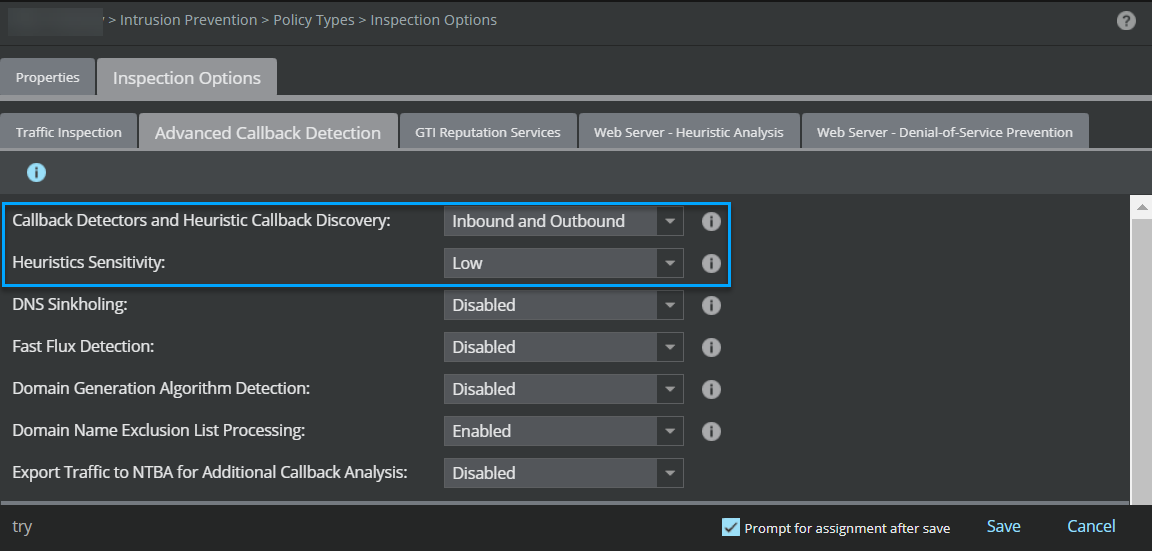
Complete the following steps to configure DNS-based detection of C&C server domains.
For this feature, the Sensor parses the DNS response traffic to detect C&C server domains according to the callback detectors.
Note
The DNS-based detection of C&C server domains is controlled by Callback Detectors and Heurtisitc Callback Discovery option as in the previous step.
From the Callback Detectors and Heurtisitc Callback Discovery drop-down list, select the required option. Additional options are displayed when you select an option other than Disabled.
Disabled — Select to disable DNS-based detection of C&C server domains. You can still enable DNS-based detection of FFSN, DGA, and exporting of traffic to NTBA for callback analysis.
Inbound only — Select this option if the name servers are in the inside network and the clients are in the outside network. The Sensor inspects the DNS response traffic in the outbound direction only.
Outbound only — Select this option if the name servers are in the outside network and the clients are in the inside network. The Sensor inspects the DNS response traffic in the inbound direction only.
Inbound and Outbound — Select this option if you want the Sensor to inspect DNS response packets regardless of the direction. This option has a greater impact on Sensor performance when compared to the other options described above.
Optionally, enable DNS Sinkholing.
For this feature, the Sensor parses the DNS response traffic. The Sensor checks if the domain name in the DNS response is C&C server in the callback detectors file. If so, the Sensor drops the DNS response and forwards a crafted DNS response with the TTL and IP address as per the DNS settings in the Protocol Settings page.
DNS-based C&C server domain detection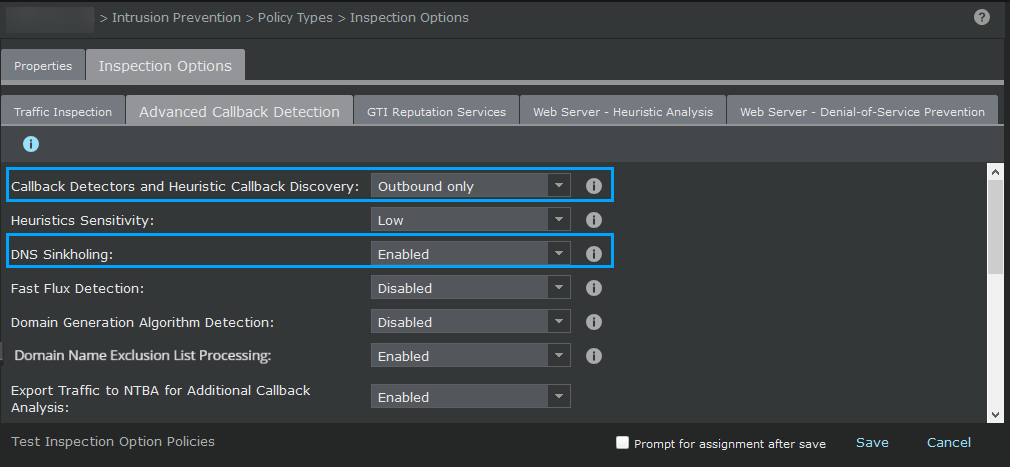
Enable Fast Flux Detection in the required direction.
The Sensor parses the DNS response traffic to detect FFSN involvement.
Disabled — Select to disable FFSN detection by the Sensor.
Inbound only — Select this option if the name servers are in the inside network and the clients are in the outside network. The Sensor inspects the DNS response traffic in the outbound direction only.
Outbound only — Select this option if the name servers are in the outside network and the clients are in the inside network. The Sensor inspects the DNS response traffic in the inbound direction only.
Inbound and Outbound — Select this option if you want the Sensor to inspect DNS response packets regardless of the direction. This option has a greater impact on Sensor performance when compared to the other options described above.
FFSN detection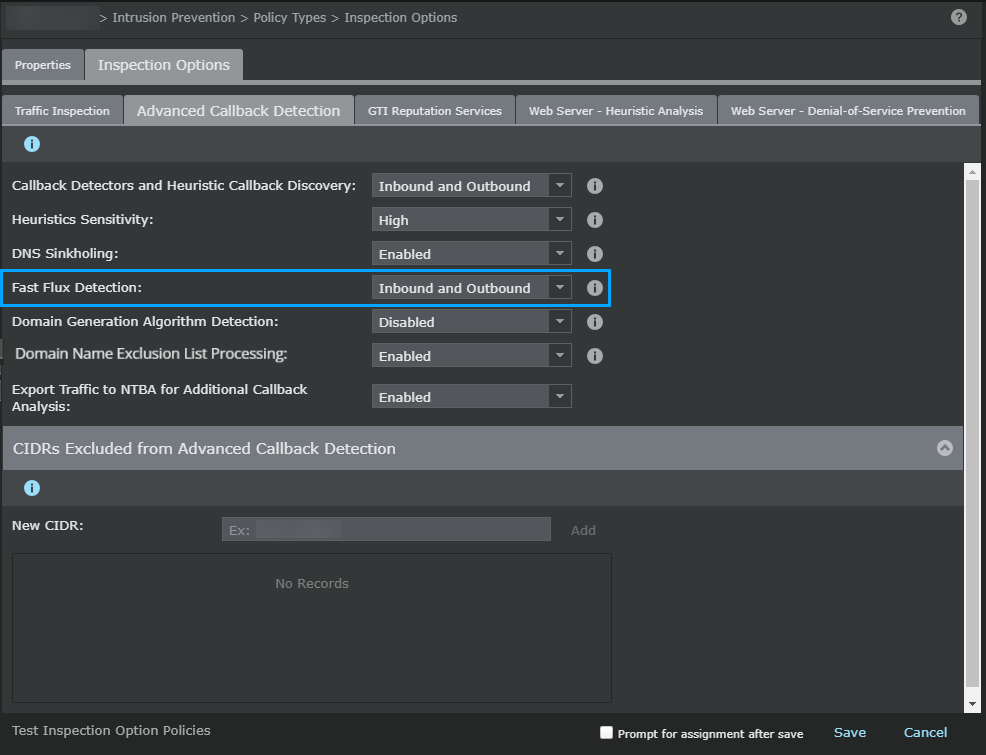
Enable Domain Generation Algorithm Detection in the required direction.
The Sensor parses the DNS response traffic to detect DGA involvement.
Disabled — Select to disable DGA detection by the Sensor.
Inbound only — Select this option if the name servers are in the inside network and the clients are in the outside network. The Sensor inspects the DNS response traffic in the outbound direction only.
Outbound only — Select this option if the name servers are in the outside network and the clients are in the inside network. The Sensor inspects the DNS response traffic in the inbound direction only.
Inbound and Outbound — Select this option if you want the Sensor to inspect DNS response packets regardless of the direction. This option has a greater impact on Sensor performance when compared to the other options described above.
Note
The Fast Flux Detection and Domain Generation Algorithm Detection heuristic engines operate in parallel for a given DNS response packet and are independent of each other. That is, the Sensor might raise an alert for FFSN and DGA for the same DNS traffic.
DGA detection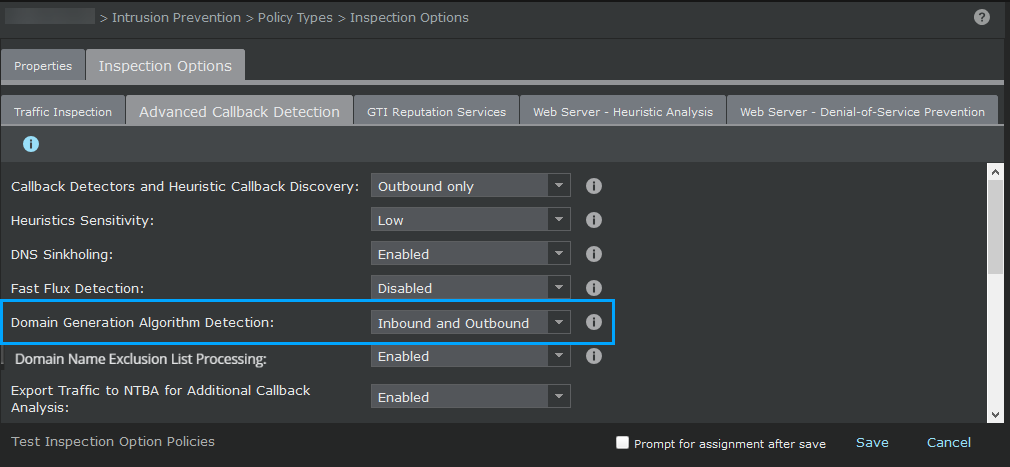
Enable Domain Name Exclusion List Processing .
Before analyzing DNS traffic, the Sensor checks if the domain name in the DNS response is exempted according to Domain Name Exceptions list. If so, the Sensor forwards the DNS response without any further DNS-based analysis for botnet.
The Domain Name Exclusion List Processing option applies to all DNS-based of callback activity-C&C server domains, FFSN detection, and DGA detection. So, for the domain name exceptions, the Sensor checks the DNS response in the same direction as Callback Detectors and Heurtistic Callback Discovery, Fast Flux Detection, and Domain Generation Algorithm Detection.
As a best practice, make sure you add your organization's public and internal domain names to the exceptions list. If Trellix is an example, you add
trellix.comto the exception list. Add the last two domain labels for such exceptions. That is, instead of www.trellix.com, addtrellix.com. This ensures that Sensor resources are not spent on analyzing traffic related to known domains.Except for purposes such as troubleshooting, always enable Domain Name Exclusion List Processing to preserve Sensor resources.
If required, enable Export Traffic to NTBA for Additional Callback Analysis to send the botnet events to NTBA for further analysis.
Heuristic detection correlates different bot activities and raises an alert when a specific condition is met. The sensitivity level determines the level of confidence the heuristic engine must have for the analysis. For example, when a low sensitivity level (default) is selected, the engine must have high confidence that it has detected a bot before raising an alert.
Note
Events can be sent to NTBA even when the local detection is disabled.
Callback Activity Detection configuration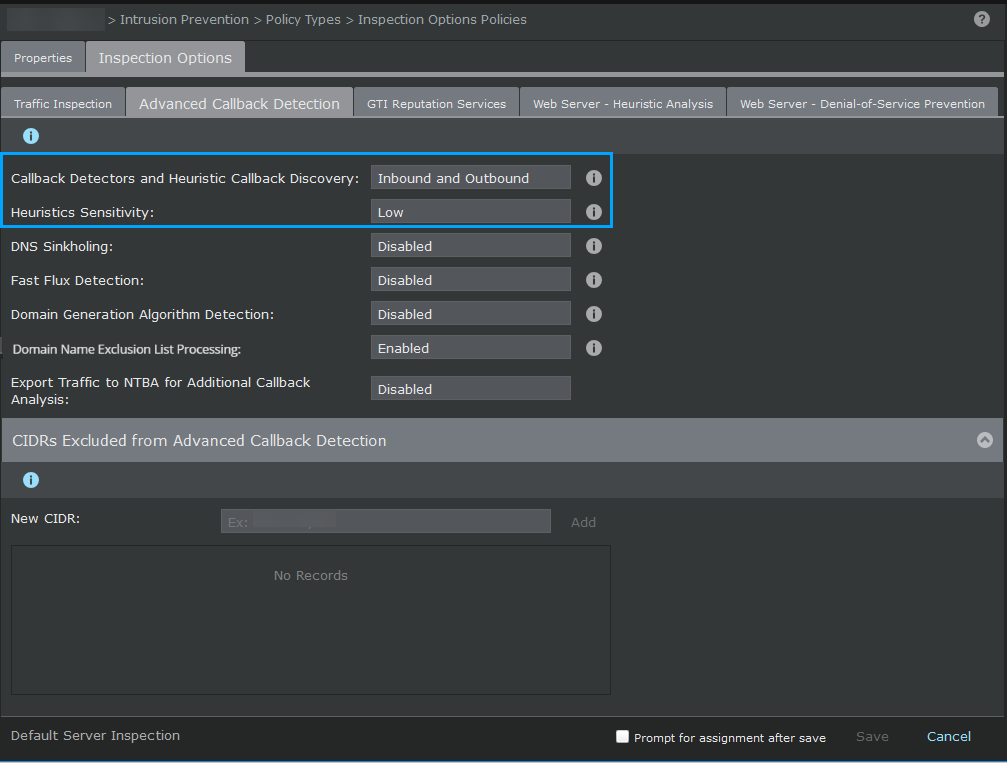
Define the IPv4 CIDRs to be excluded from callback detection.
To add a CIDR, enter a valid CIDR notation and click Add. For example, enter 10.1.1.0/24 to exclude the hosts from 10.1.1.1 through 10.1.1.254 from callback detection.
To remove a CIDR from the list, click on the adjacent X icon.
If the traffic is from or to a defined CIDR, the Sensor exempts that traffic from the following callback detection features.
DNS-based detection
HTTP-based detection for IP addresses of C&C server domain alone is exempted. The Sensor performs HTTP-based detection for IP address and URL, domain, domain and URL of C&C server domain.
Other advanced callback heuristics
Click Save.
If you select Prompt for assignment after save, you are prompted to assign the inspection option policy to the Sensor resources owned by the corresponding domain.