Should you deploy Sensors at the perimeter of your network, in front of the servers you want to protect, or at a convenient nexus where all traffic passes?
Deployment at the perimeter does not protect you from internal attacks, which are some of the most common source of attacks. Perimeter monitoring is also useless if a network has multiple ISP connections at multiple locations (such as one Internet connection in New York and one in San Jose) and if you expect to see asymmetric traffic routing (that is, incoming traffic comes through New York and outgoing traffic goes out through San Jose). The IPS simply will not see all the traffic to maintain state and detect attacks. Deployment in front of the servers that you want to protect both detects attacks from internal users and deals effectively with the geographically diverse asymmetric routing issue.
A better illustration of the advantage of Sensors' multiple segment monitoring is to consider the question of installing Sensors with respect to firewalls. It is very common to deploy Sensors around firewalls to inspect the traffic that is permitted by the firewall. A common question when installing Sensors around the firewall is: Do you put the Sensors on the inside (Private and DMZ) or put them outside (Public) the firewall? There are benefits to both scenarios, and the more complete solution includes both. For example, if you detect an attack on the outside of the firewall and you detect the same attack on the inside of the firewall, then you know your firewall has been breached. This is obviously a much higher severity event than if you were just to see the attack on the outside and not on the inside, which means that your firewall blocked the attack.
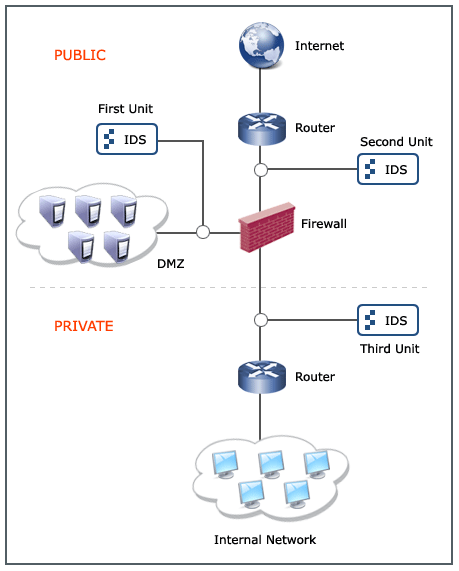
When using the existing, single monitoring port products available, you would have to deploy multiple Sensors to get the required coverage (as shown in Scenario 1 below). Furthermore, you would need to figure out how to connect them to the segments that you want to monitor, and only via a SPAN or hub port.
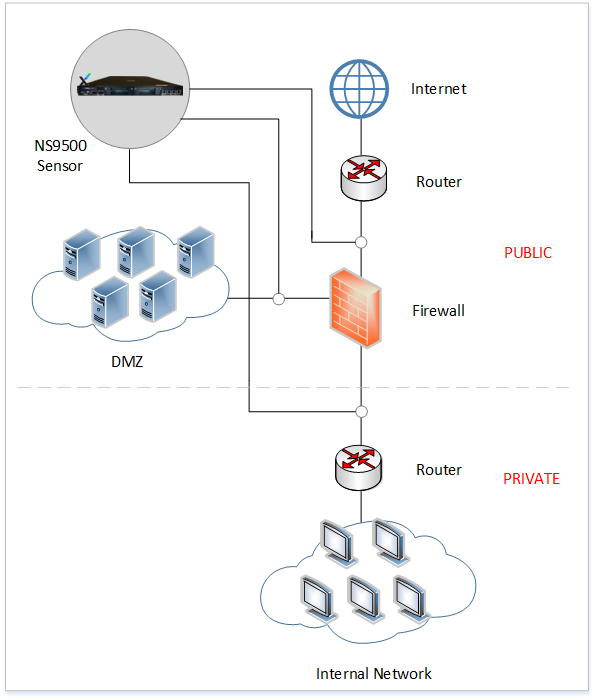
Consider the same scenario using the NS9500 Sensor (as shown in Scenario 2 below). You can simultaneously monitor all three segments with one Sensor, and, with the integrated taps, you can easily monitor the full-duplex uplinks between your routers and the firewall. You can also run the inside connections in in-line mode, which provides intrusion protection/prevention, while running the outside connection in tapped mode.