In-line mode is achieved when the Sensor is placed directly in the path of a network segment, becoming, essentially, a "bump in the wire," with packets flowing through the Sensor. In this mode, the Sensor can prevent network attacks by dropping malicious traffic in real time. Preventative actions can be at a highly granular level, including the automated dropping of DoS traffic intended for a specific Web server.
Note
Sensors are configured by default to run in in-line mode.
When running in in-line mode, network segments are connected to two matched ports of the Sensor (for example, ports G0/1 and G0/2), and packets are examined in real time as they pass through the Sensor.
The benefits of using Sensors in in-line mode are:
Protection/Prevention – Prevention is a feature unique to in-line mode. Basically, if you are running in any "sniffing" mode, there is no way for the IPS to prevent malicious packets from reaching their intended target. In a sniffing mode, the Sensor sees the attack at the same time it hits the target. You can apply some countermeasures, like TCP Resets, but these are post-detection actions. The only way to prevent the malicious packets from reaching the target is to mediate the traffic flow.
When running in-line, the Sensor can drop malicious packets and not pass them through the network. This acts sort of like an "adaptive firewall," with your detection policy dictating what is dropped. Furthermore, when dropping packets, Trellix IPS is very precise and granular. The Sensor can drop only those packets it identifies as malicious or all of the packets related to that flow (a choice that is user configurable).
One of the problems with using firewall reconfiguration actions with current IDS products is that an attacker can spoof large address ranges and mislead you into blocking legitimate traffic with the firewall, creating your own denial of service condition. Trellix IPS only drops the malicious packets, so spoofed traffic doesn't have the same effect.
Packet "scrubbing" – In addition to dropping malicious traffic, Trellix IPS can scrub—or normalize—traffic to take out any ambiguities in protocols that the attacker may be using to try to evade detection. Current IDS products are susceptible to these techniques, and an example of this attempt is IP fragment and TCP segment overlaps. The Sensor can reassemble the IP fragments and TCP segments and enforce a reassembly mode of the user's choice to accept either the old or the new data.
Processing at wire-speed – An obvious requirement with running in-line is to avoid dropping packets and your IDS Sensor becoming a bottleneck. Sensors are able to process packets at wire rates.
High Availability – In in-line mode, the Sensor does become a single point of failure, so the Sensors support complete stateful fail-over, delivering the industry's first true high-availability IPS deployment, similar to what you would find with firewalls. If you're running in-line, Trellix recommends that you deploy two Sensors redundantly for failover protection.
In-line mode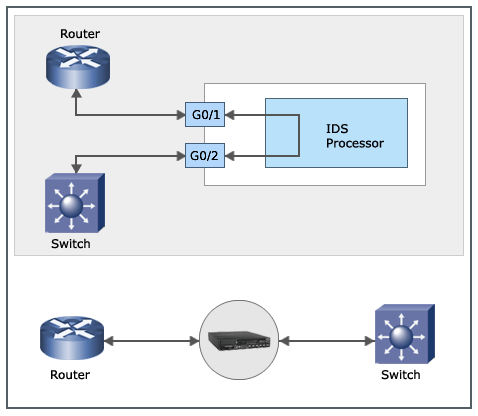
Traffic prioritization – When you deploy a port in inline mode and enable the inline traffic prioritization feature, the Sensor prioritizes packets emerging from the port in inline mode, during heavy network load conditions, over packets emerging from a port in SPAN mode.
The Sensor periodically checks for latency in inline packets. If latency is higher than a stipulated limit and, at the same time, there are several inline packets and SPAN packets in queue to be analyzed by the Sensor, some of the SPAN packets are dropped to prioritize inline packets.
When traffic density returns to normal operating levels, the Sensor stops prioritizing inline packets and traffic is analyzed in the order that it arrives.
Note
Prioritization of inline traffic is disabled by default. You can view or change its status only through the Sensor CLI Debug mode using the following commands:
show inline traffic prioritization status— Displays whether it is enabled or disabledset inline traffic prioritization <enable | disable>— Enables or disables the feature
In inline mode (seen in the previous figure), the Sensor logically acts as a transparent repeater with minimal latency for packet processing. Unlike bridges, routers, or switches, the Sensor does not need to learn MAC addresses or keep an ARP cache or a routing table.
When deployed in-line, you must specify whether the Sensor port is monitoring inside or outside of the network it is protecting. For example, the Sensor shown in the figure in the section Determination of complexity of your network topology? is monitoring links both inside and outside the network.