View traffic sent/received data
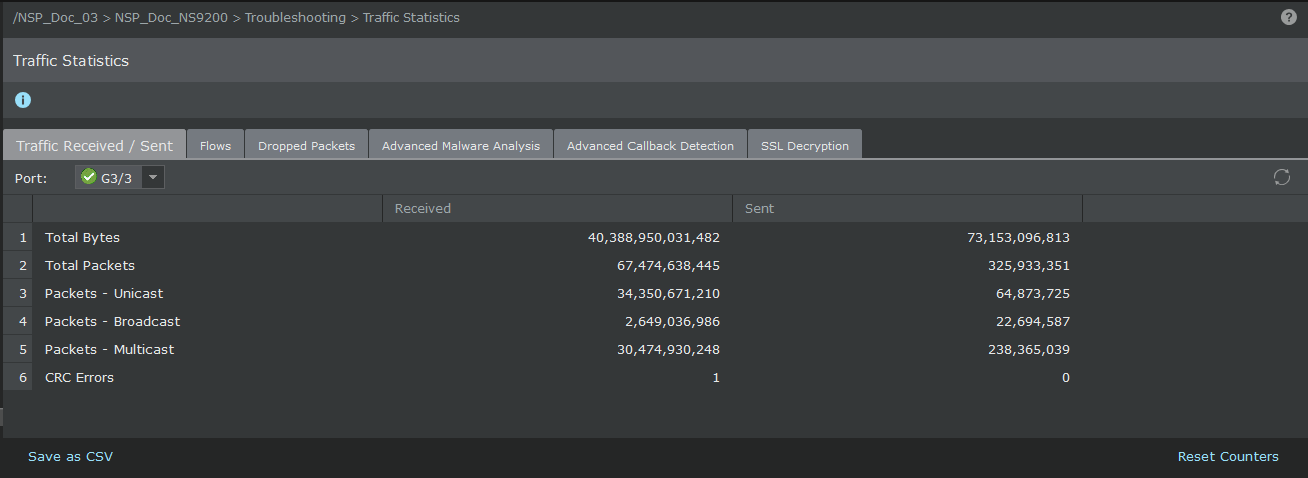
You can view the statistics of the total number of packets received (Rx) and transmitted (Tx) for a given device per port. You can select the port from the Port drop-down list for which you want to view the sent/received data. The All Ports option is selected by default and displays information for all the ports. When you hover the mouse over a port in the Port drop-down list, a tooltip displays the status of the port as Link Up, Link Down, or Disabled. This tab displays the following information:
Total Bytes - Total number of bytes received and sent through the selected interface port
Total Packets - Total number of Unicast, Broadcast, and Multicast packets received and sent through the selected interface port
Packets - Unicast - Total number of Unicast packets received and sent through the selected interface port
Packets - Broadcast - Total number of Broadcast packets received and sent through selected interface port
Packets - Multicast - Total number of Multicast packets received and sent through the selected interface port
CRC Errors - Total number packets with CRC errors received and sent through the selected interface port
View traffic flows
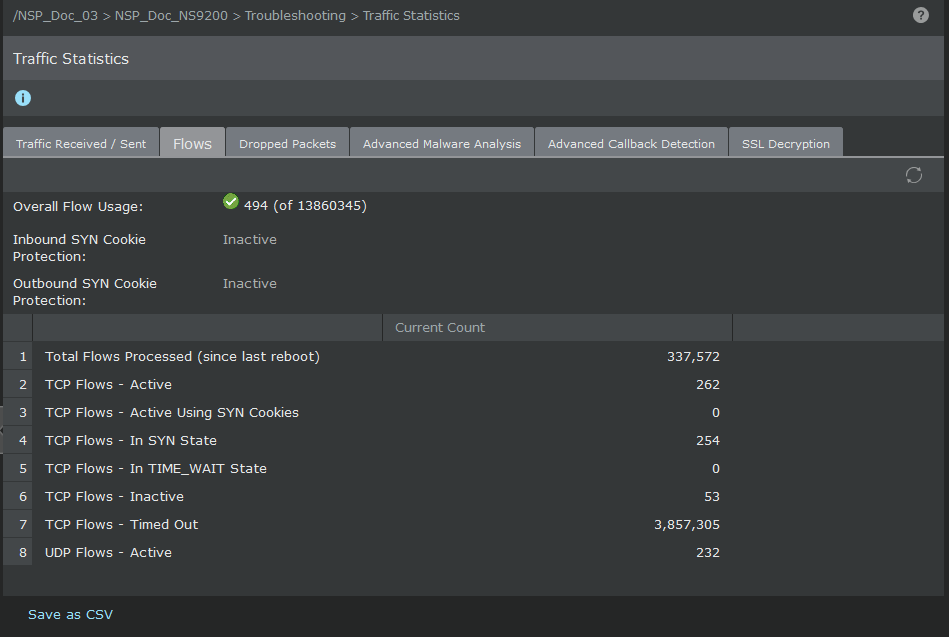
You can view the statistical TCP and UDP flow data processed by a device. Checking your flow rates can help you determine if your device is processing traffic normally. This also provides you with a view of statistics such as the available flows supported, as well as the number of active TCP and UDP flows. This tab displays the following information:
Total Flows Processed (since last reboot) - Total number of flows processed by the Sensor since the last Sensor reboot
TCP Flows - Active - Total number of TCP flows that are currently active
TCP Flows - Active Using SYN Cookies - Total number of active TCP flows that are using SYN cookies
TCP Flows - In SYN State - Total number of TCP flows that are currently in SYN state
TCP Flows - In TIME_WAIT State - Total number of TCP flows that are currently in TIME_WAIT state
TCP Flows - Inactive - Total number of TCP flows that are currently inactive
TCP Flows - Timed Out - Total number of unsuccessful TCP connection completions
UDP Flows - Active - Total number of UDP flows that are currently active
View the dropped packets data
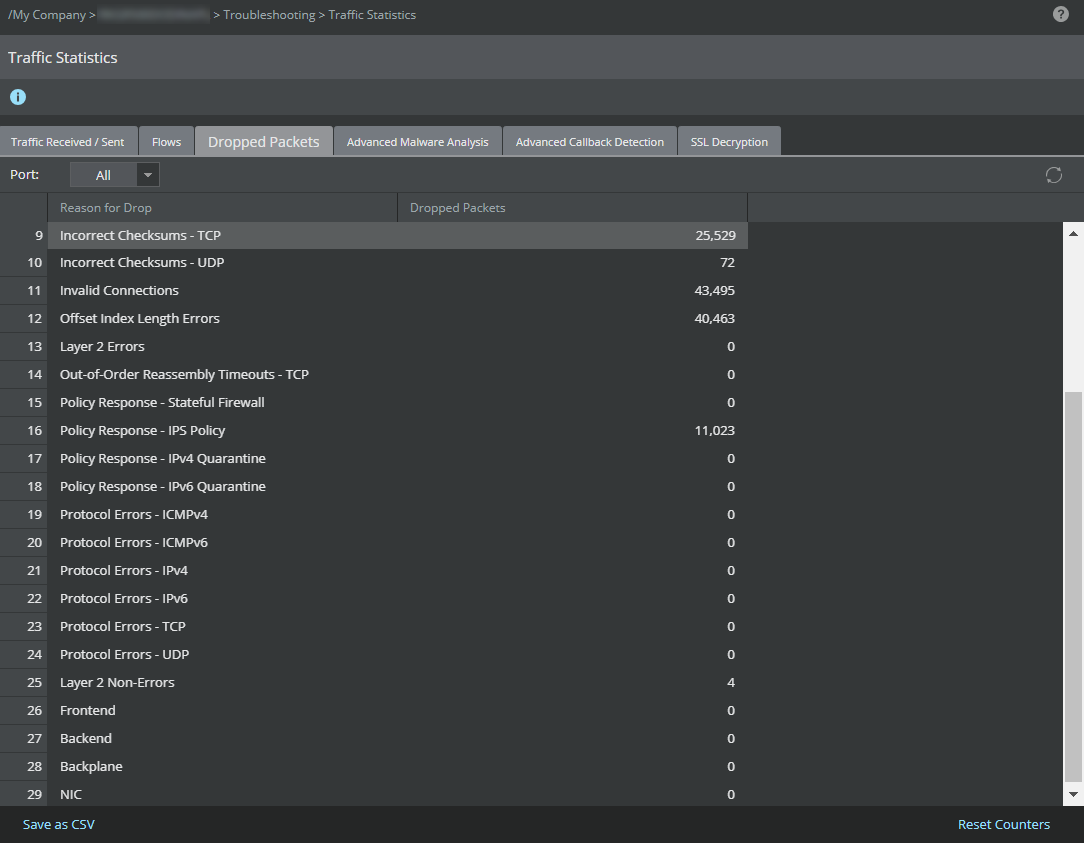
Using this tab, you can view the reason and the packet drop rate on a port for a device. The All option is selected by default and displays information for all the ports. This tab displays the following information:
Backend - Total number of miscellaneous packets dropped at back-end
Backplane - Total number of miscellaneous packets dropped at BMC switch
CRC Failures - Total number of packets dropped due to CRC errors
Device Power Up - Total number of packets dropped during cold start
Device Resource Exhaustion - Total number of packets dropped by the Sensor because of non availability of resources
Fragment Reassembly Timeouts - IPv4 - Total number of packets dropped due to IPV4 fragment reassembly timeout
Fragment Reassembly Timeouts - IPv6 - Total number of packets dropped due to IPV6 fragment reassembly timeout
Frontend - Total number of miscellaneous packets dropped at front-end
Incorrect Checksums - ICMPv4 - Total number of packets dropped due to incorrect ICMP v4 checksum
Incorrect Checksums - ICMPv6 - Total number of packets dropped due to incorrect ICMP v6 checksum
Incorrect Checksums - IP - Total number of packets dropped due to incorrect IP checksum
Incorrect Checksums - TCP - Total number of packets dropped due to incorrect TCP checksum
Incorrect Checksums - UDP - Total number of packets dropped due to incorrect UDP checksum
Invalid Connections - Total number of packets dropped due to of invalid connection
Layer 2 Errors - Total number of packets dropped due to Layer 2 errors
Layer 2 Non-Errors - Total number of Layer-2 packets dropped due to other reasons
NIC - Total number of miscellaneous packets dropped at NIC
Offset Index Length Errors - Total number of packets dropped due to offset index length errors
Out-of-Order Reassembly Timeouts - TCP - Total number of packets dropped due to TCP out-of-order reassembly timeout
Policy Response - Stateful Firewall - Total number of packets dropped due to the configured firewall policy
Policy Response - IPS Attack - Total number of packets dropped due to the configured IPS policy
Policy Response - IPv4 Quarantine - Total number of packets dropped due to the configured IPv4 Quarantine policy
Policy Response - IPv6 Quarantine - Total number of packets dropped due to the configured IPv6 Quarantine policy
Protocol Errors - ICMPv4 - Total number of packets dropped due to ICMPv4 protocol errors
Protocol Errors - ICMPv6 - Total number of packets dropped due to ICMPv6 protocol errors
Protocol Errors - IPv4 - Total number of packets dropped due to IPv4 protocol errors
Protocol Errors - IPv6 - Total number of packets dropped due to IPv6 protocol errors
Protocol Errors - TCP - Total number of packets dropped due to TCP protocol errors
Protocol Errors - UDP - Total number of packets dropped due to UDP protocol errors
Note
The following counters are displayed only when you select the All option in the Port drop-down:
Frontend
Backend
Backplane
Layer 2 Non-Errors
NIC
View the malware analysis data for a device
You can view the statistics of the malware detected for a given device. There are two options provided on this tab:
The By Malware Engine option displays the malware detected data based on the malware engines configured for the device. The following information is displayed when this option is selected -
Files Submitted to Engine - Number of malware files submitted to specific malware engine
Files Ignored by Engine - Number of malware files ignored by the specific malware engine
Files Processed by Engine - Number of malware files processed by the specific malware engine
Trellix Intelligent Sandbox Files Dropped Under Load - Number of malware files dropped by the Trellix Intelligent Sandbox engine due to excessive load
Trellix Intelligent Sandbox Static Analyses - Number of malware files processed by the Trellix Intelligent Sandbox engine based on static analysis using Block list and Allow list, GTI File Reputation, and Gateway Anti-Malware (GAM)
Trellix Intelligent Sandbox Dynamic Analyses - Number of malware files processed by the Trellix Intelligent Sandbox engine based on dynamic analysis using Sanbox and Machine Learning
Trellix Intelligent Sandbox Cache Response Matches - Number of malware results obtained from the Trellix Intelligent Sandbox cache
Clean Files - Number of clean files processed by the specific malware engine
Very High Malware Confidence Matches - Number of malware alerts generated by the specific malware engine and having malware score as very high
High Malware Confidence Matches - Number of malware alerts generated by the specific malware engine and having malware score as high
Medium Malware Confidence Matches - Number of malware alerts generated by the specific malware engine and having malware score as medium
Low Malware Confidence Matches - Number of malware alerts generated by the specific malware engine and having malware score as low
Very Low Malware Confidence Matches - Number of malware alerts generated by the specific malware engine and having malware score as very low
Unknown Malware Confidence Matches - Number of files for which the malware confidence level is not known
Alerts Generated - Number of malware alerts sent to the Manager by the Sensor for the specific malware engine
Files Blocked - Number of malware attacks blocked by the Sensor for the specific malware engine
Connections Reset - Number of malware TCP Resets sent by the Sensor for the specific malware engine
Malware analysis by engines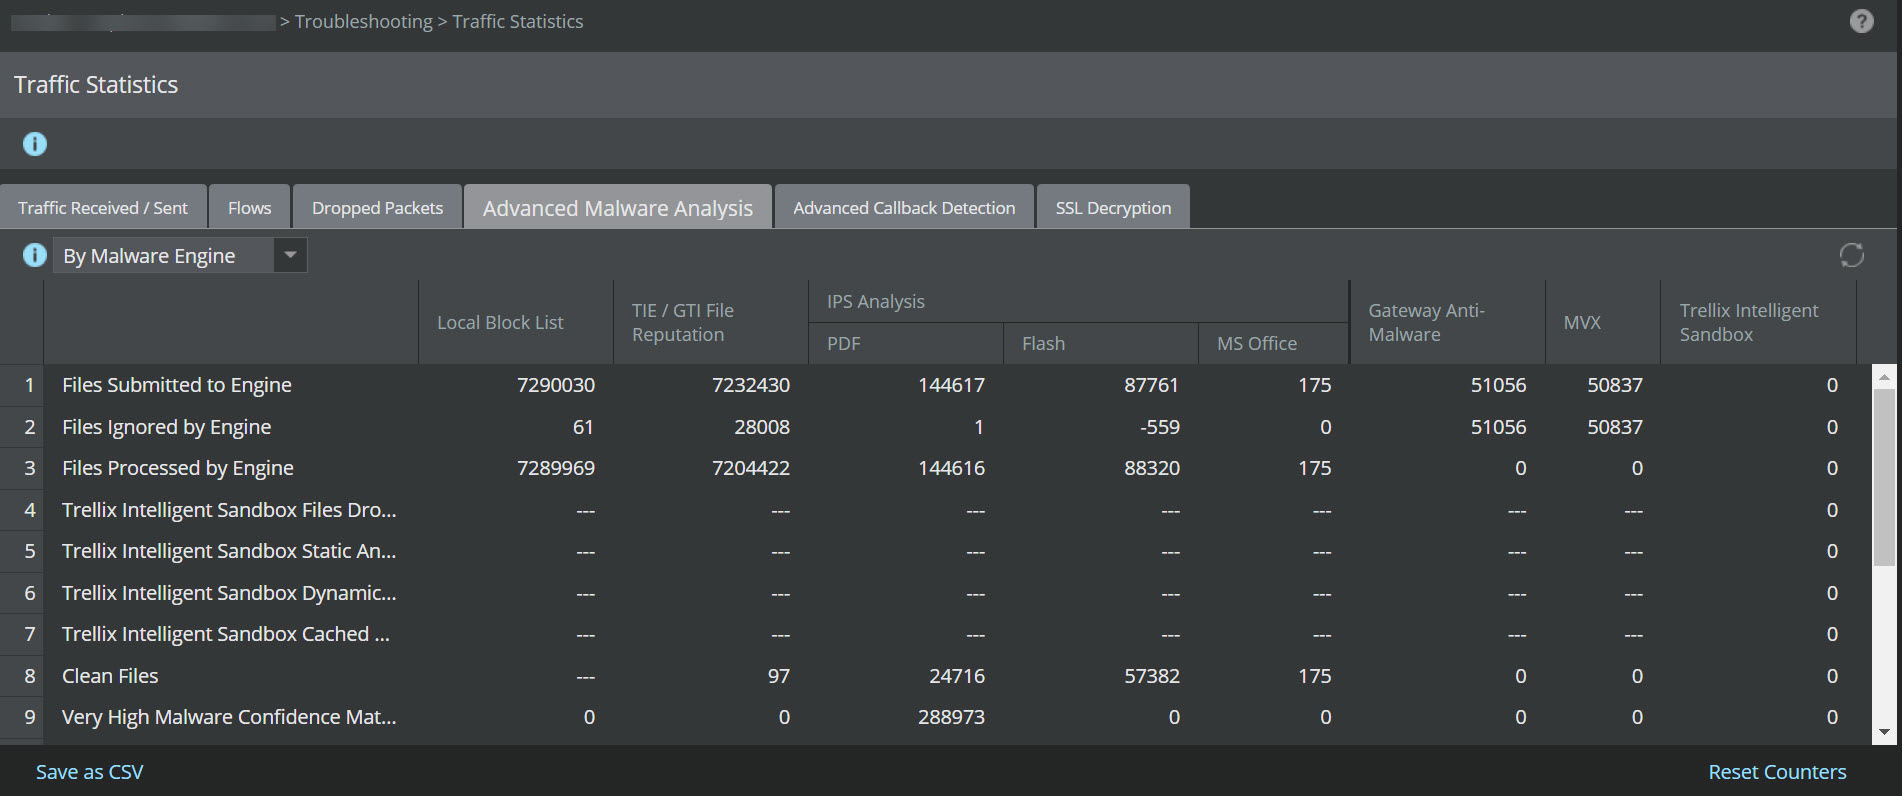
The By File type option displays data based on the file type analyzed. The file types include Executables, MS Office Files, PDF Files, Flash Files, Compressed Files, Android Application Packages, Java Archives, and Script Files.
Malware analysis by filetype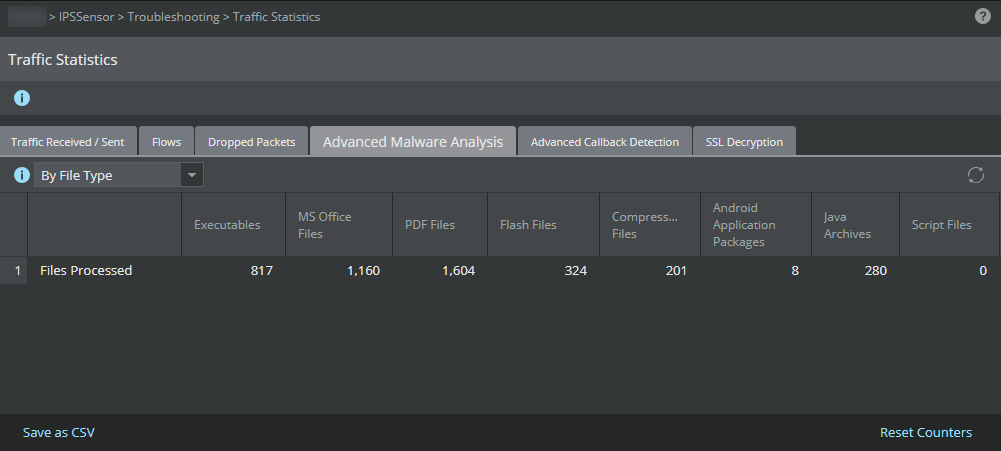
View Advanced Callback Detection
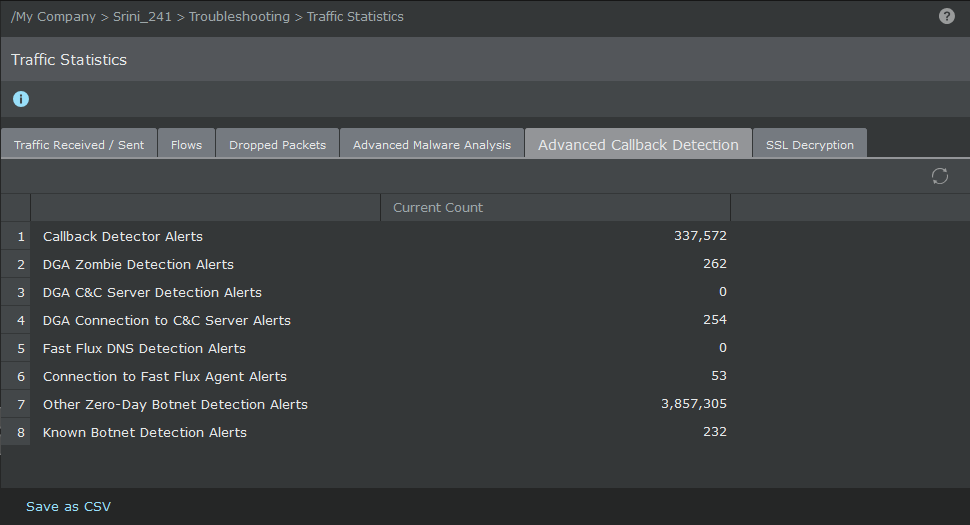
You can view the count for number of alerts generated for various bot activities. This provides information on the amount of callback activity and also communication attempts to the C&C servers. This tab displays the following information:
Callback Detector Alerts - Total number of alerts pertaining to a callback detector match
DGA Zombie Detection Alerts - Total number of alerts for DGA zombies
DGA C&C Server Detection Alerts - Total number of alerts for C&C server suspects
DGA Connection to C&C Server Alerts - Total number of alerts for DGA zombie callback and C&C server
Fast Flux DNS Detection Alerts - Total number of alerts for IP flux botnet activity
Connection to Fast Flux Agent Alerts - Total number of alerts for IP flux agent call back activity
Other Zero-Day Botnet Detection Alerts - Total number of alerts for other Zero-Day botnets
Known Botnet Detection Alerts - Total number of alerts for known botnets
View SSL Decryption statistics
Using this tab, you can view traffic statistics for inbound and outbound SSL decryption:
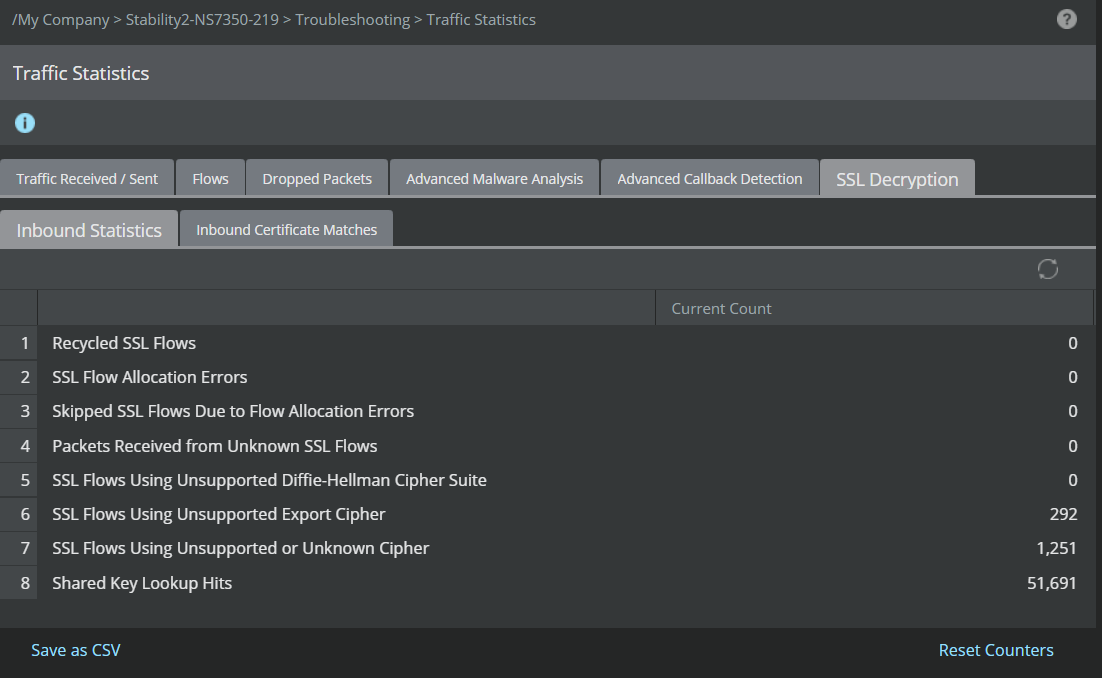
Inbound Statistics: Using this tab, you can view traffic statistics for inbound SSL decryption.
Recycled SSL Flows - Total number of SSL flows that are not used recently and freed by the Sensor
SSL Flow Allocation Errors - Total number of SSL flows the Sensor could not allocate due to resource unavailability
Skipped SSL Flows Due to Flow Allocation Errors - Indicates total SSL flows that were skipped as the Sensor could not process them due to resource unavailability
Packets Received from Unknown SSL Flows - Total number of SSL packets received that did not have a corresponding SSL flow
SSL Flows Using Unsupported Diffie-Hellman Cipher Suite - SSL flows that are negotiated and not decrypted by the Sensor due to unsupported ciphers DH cipher suite in the traffic
SSL Flows Using Unsupported Export Cipher - Total flows with SSLv3/TLS export cipher that are negotiated and not decrypted by the Sensor due to unsupported RSA cipher suite
SSL Flows Using Unsupported or Unknown Cipher - Total flows with unsupported or unknown ciphers
Shared Key Lookup Hits – Displays the number of times the Sensor uses the session key table provided by the Agent to decrypt inbound traffic using Diffie-Hellman cipher suite
Outbound Statistics: Using this tab, you can view traffic statistics for outbound SSL decryption.
Note
Outbound SSL decryption uses Proxy method for traffic decryption and is supported by specific NS-series Sensor models. So, you will be able to see outbound statistics tab being populated only when you add these Sensor models to the Manager. List of NS-series Sensor models supported — NS3600, NS7200, NS7300, NS7500, NS7600, NS9100, NS9200, NS9500 Standalone, NS9600 Standalone, and NS9600 Stack.
SSL Connection Attempts: Clients -> Sensor - Total number of SSL flow attempts from client to Sensor in outbound direction
SSL Connection Attempts: Sensor -> Web Servers - Total number of SSL flow attempts from Sensor to external server in outbound direction
End-to-End SSL Handshakes in Progress - Total number of SSL handshakes in progress in the outbound direction
End-to-End SSL Flows Established - Total number of SSL flows established in the outbound direction
Excluded SSL Flows - Total number of SSL flows in outbound direction that are excluded from getting blocked
Attacks Detected in SSL Flows - Total number of attacks detected in the outbound SSL flows
RSA Flows - Total number of flows seen with RSA key exchange in outbound direction
Diffie-Hellman Flows - Total number of flows seen with Diffie-Hellman key exchange in the outbound direction
Non-SSL Flows - Total number of non-ssl flows seen in the outbound direction
SSL Flows Blocked/Skipped from Unsupported Cipher Suites - Total number of SSL flows blocked or skipped due to unsupported cipher suites found in them
SSL Flows Blocked/Skipped from Unsupported Server Certificates - Total number of SSL flows blocked or skipped due to unsupported certificates found in them
Unknown Server Certificates - Total number of unknown certificates seen in the outbound SSL flows
SSL Flows Blocked/Skipped from Unknown Server Certificates - Total number of outbound SSL flows blocked or skipped due to unknown certificates
Untrusted Server Certificates - Total number of untrusted certificates seen in the outbound SSL flows
SSL Flows Blocked/Skipped from Untrusted Server Certificates - Total number of outbound SSL flows blocked or skipped due to untrusted certificates
SSL Decryption - Outbound Statistics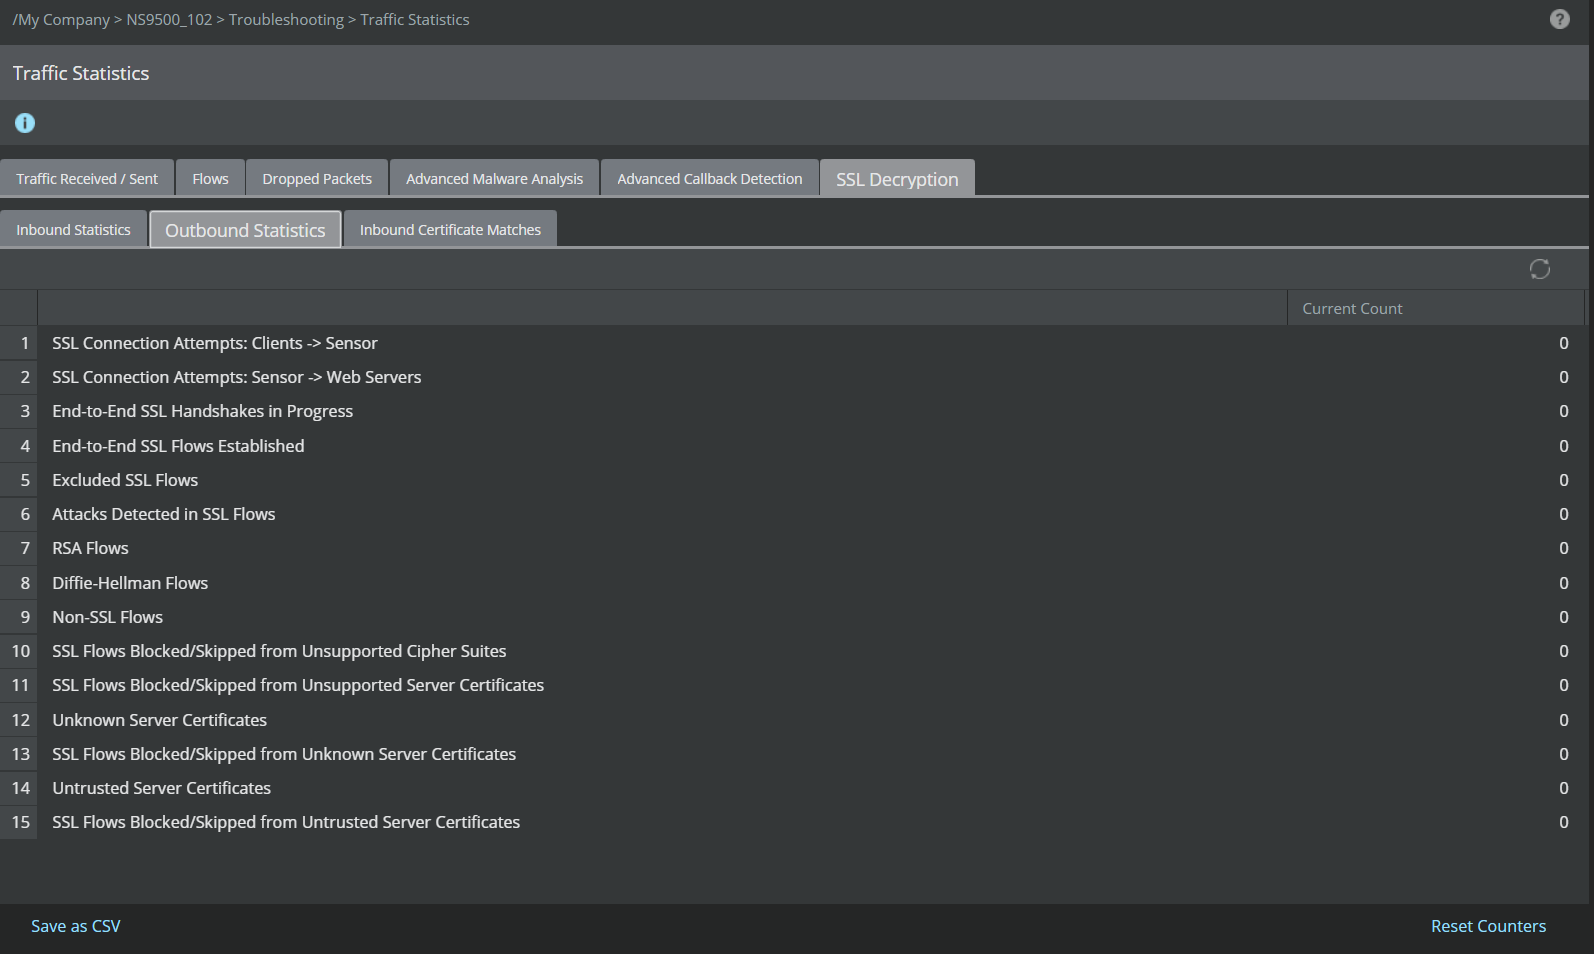
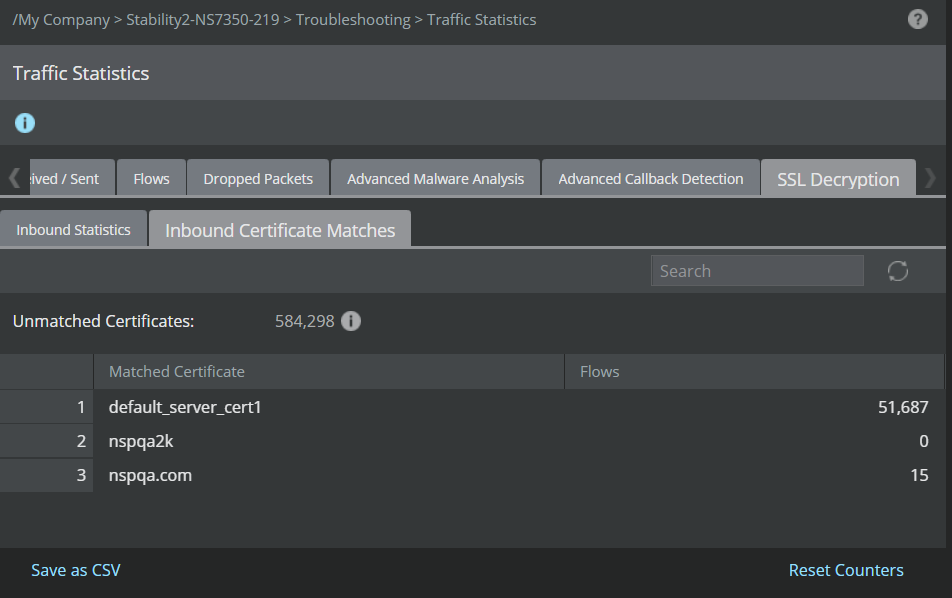
Inbound Certificate Matches: This tab displays the count for unmatched and matched certificates found in inbound SSL traffic.
SSL Decryption - Inbound Certificate Matches