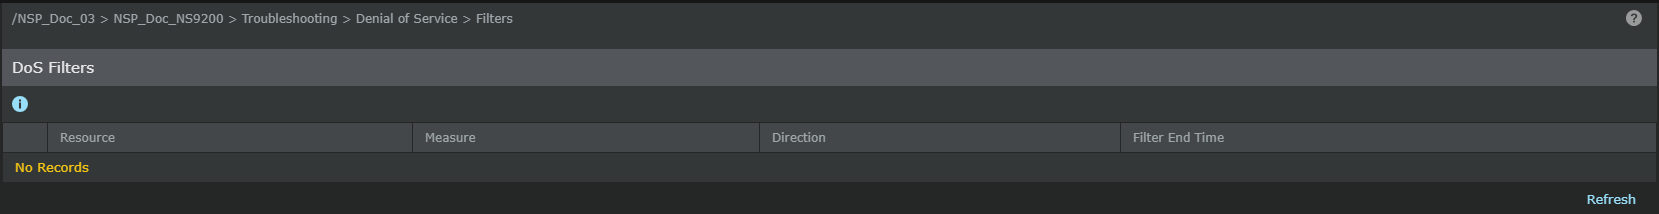
You can view and modify the drop/block packets responses that have been initiated for the DoS learning mode profiles applied for all network identifiers (NIs) within a Sensor. A DoS filter, or blocking rule, is similar to a firewall deny rule in that subsequent traffic that matches the filter parameters is blocked from transmitting further through your network. A network identifier is a Trellix IPS term relating to interface, subinterface, and DoS ID resources. DoS filters are applied exclusively to DoS learning mode attacks.
A DoS filter can be initiated for any DoS learning mode attack, namely the measures within each attack. Each enabled learning mode attack is a combination of traffic flow rate measures, such as the rate of TCP control packets or UDP packets. When a learning mode profile has completed learning the normal traffic behavior, the long-term measure volumes in this profile are matched against short-term volume calculations for each measure. If the short-term volume is outside of the long-term volume, a statistical attack type alert is raised. Once a statistical alert has been raised, the Sensor can initiate an automatic or manual response to block all subsequent packets of the violated measure.
For automatic dropping and blocking, you configure a DoS policy with the drop packets response enabled for one or more measures and apply the policy to a Sensor interface in inline mode. Automatic filters last as long as the short-term volume continues to violate the long-term volume.
For manual blocking, you must initiate the response from IPS Policies for an attack. For more information, see Blocking DoS attacks.
Steps:
To go to the DoS Filters page -
For individual Sensors, navigate to Devices → <Admin Domain Name> → Devices → <Device Name> → Troubleshooting → Denial of Service → Filters.
For Sensors in HA pair, navigate to Devices → <Admin Domain Name> → Devices → <Device Name> → Member Sensors → <HA Pair Node> → Troubleshooting → Denial of Service → Filters.
(Applicable to NS9600 and NS9500 only) For Sensors in a stack and a HA pair of stack Sensors, navigate to Devices → <Admin Domain Name> → Devices → <Device Name> → Member Sensors → <Stackname-node id> → Troubleshooting → Denial of Service → Filters.
The DoS Filters page is displayed.
Do one of the following:
To delete a filter, select a filter and click Delete.
To refresh a filter, select a filter and click Refresh.
To extend a filter, do the following:
Select a filter and click Extend. The Add DoS Filter Time dialog opens.
Type the number of seconds to add to the Filter Time.
Click Save; click Cancel to abort.
Add DoS Filter