---
title: "DoS filter management"
slug: "dos-filter-management"
tags: ["Product Usage", "IPS 10.1.10"]
updated: 2026-10-05T15:39:53Z
published: 2026-10-05T15:39:53Z
canonical: "docs.trellix.com/dos-filter-management"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://docs.trellix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# DoS filter management
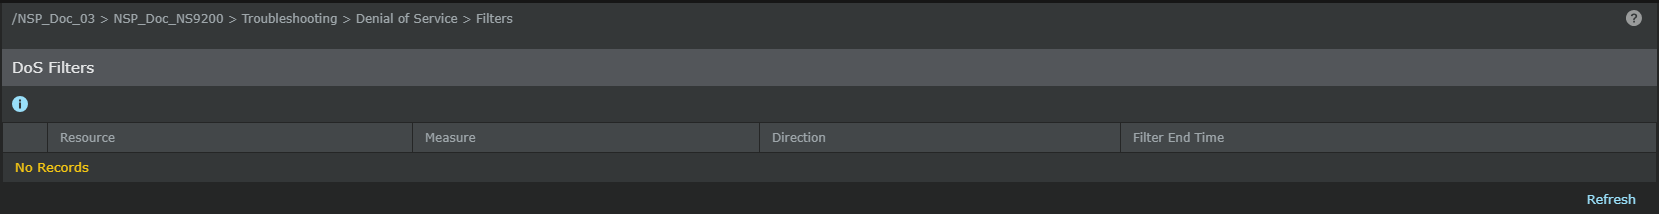
You can view and modify the drop/block packets responses that have been initiated for the DoS learning mode profiles applied for all network identifiers (NIs) within a Sensor. A DoS filter, or blocking rule, is similar to a firewall deny rule in that subsequent traffic that matches the filter parameters is blocked from transmitting further through your network. A network identifier is a Trellix IPS term relating to interface, subinterface, and DoS ID resources. DoS filters are applied exclusively to DoS learning mode attacks.
A DoS filter can be initiated for any DoS learning mode attack, namely the measures within each attack. Each enabled learning mode attack is a combination of traffic flow rate measures, such as the rate of TCP control packets or UDP packets. When a learning mode profile has completed learning the normal traffic behavior, the long-term measure volumes in this profile are matched against short-term volume calculations for each measure. If the short-term volume is outside of the long-term volume, a statistical attack type alert is raised. Once a statistical alert has been raised, the Sensor can initiate an automatic or manual response to block all subsequent packets of the violated measure.
- For automatic dropping and blocking, you configure a DoS policy with the
*drop packets* response enabled for one or more measures and apply the policy to a Sensor interface in inline mode. Automatic filters last as long as the short-term volume continues to violate the long-term volume.
- For manual blocking, you must initiate the response from IPS Policies for an attack.
For more information, see
Blocking DoS attacks.
## Task
1. Click the
**Devices** tab.
2. Select the domain from the
**Domain** drop-down list.
3. In the left pane, click the
**Devices** tab.
4. Select the device from the
**Device** drop-down list.
5. Select
**Troubleshooting** → **Denial of Service** → **Filters**.
Do one of the following:
- To delete a filter, select a filter and click
**Delete**.
- To refresh a filter, select a filter and click
**Refresh**.
- To extend a filter, do the following:
1. Select a filter and click
**Extend**. The
**Add DoS Filter Time** dialog opens.
2. Type the number of seconds to add to the
**Filter Time**.
3. Click
**Save**; click
**Cancel** to abort.
Add DoS Filter